Hansel

Communication Infrastructure
You Actually Own.

End-to-end encryption, DLP, eDiscovery, and full admin control without platform dependency or enterprise markup.

Get Hansel Free
Scroll
THE SOVEREIGNTY PROBLEM

Your Organization's Communication
Doesn't Belong to You.

When your organization runs on Google Workspace or Microsoft 365, you're not the owner — you're a tenant. Your encryption keys live on their servers. Your compliance data flows through their infrastructure. One account suspension and you lose everything overnight.

Hansel was built after exactly that happened. A real organization — locked out of Google overnight. No warning. No appeal window. No data access. That's the vendor lock-in trap. Hansel is the exit.
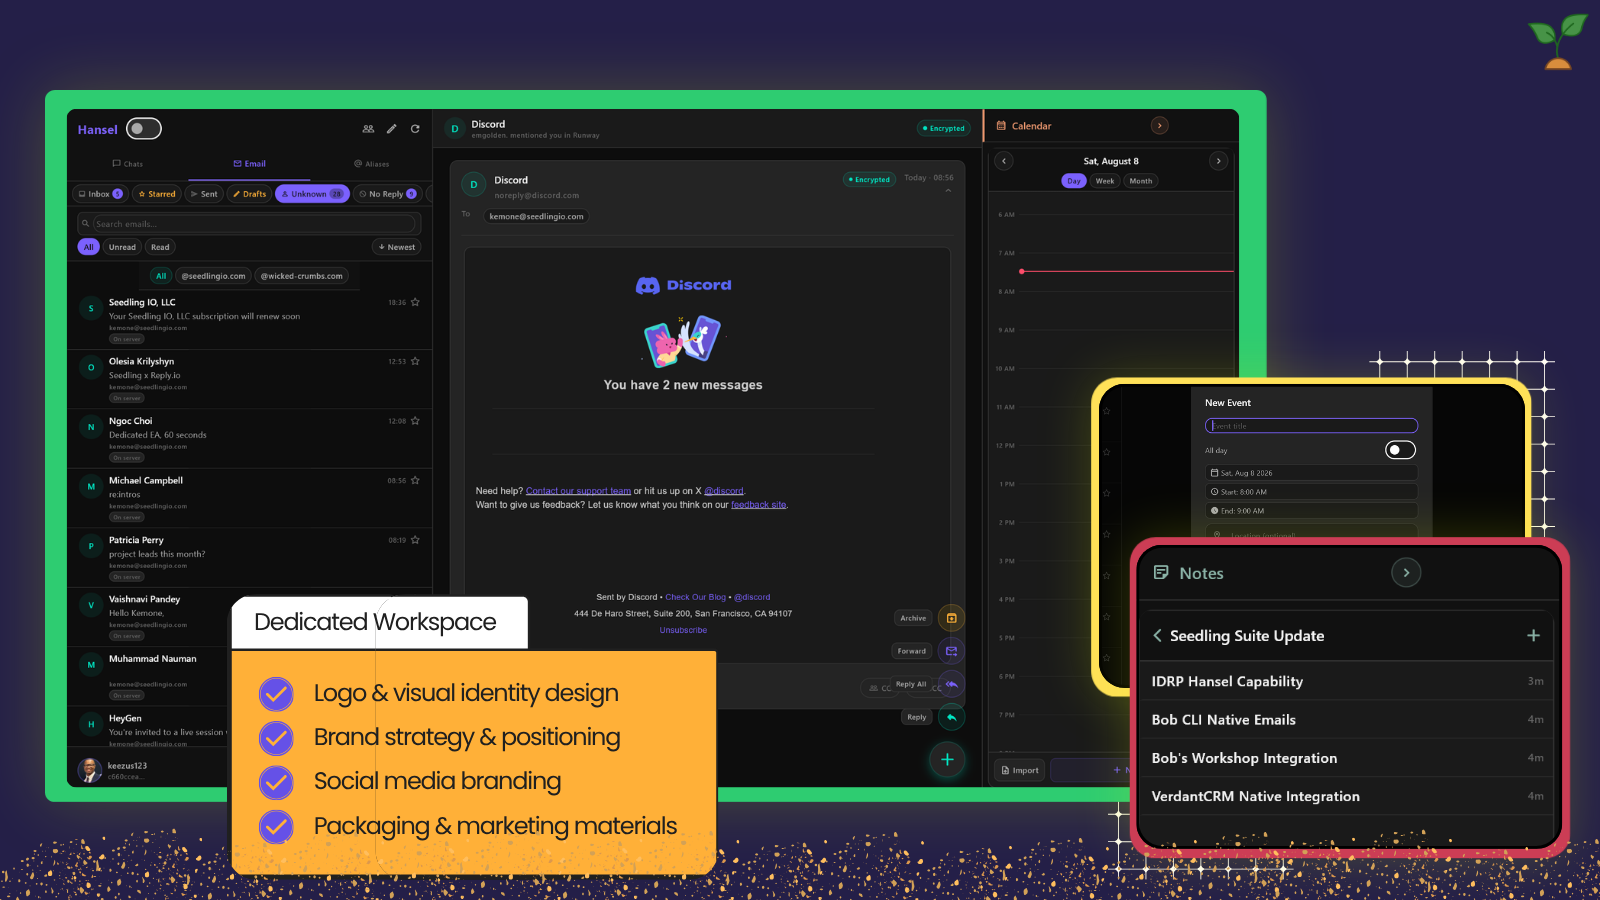
Hansel Workspace
🌐

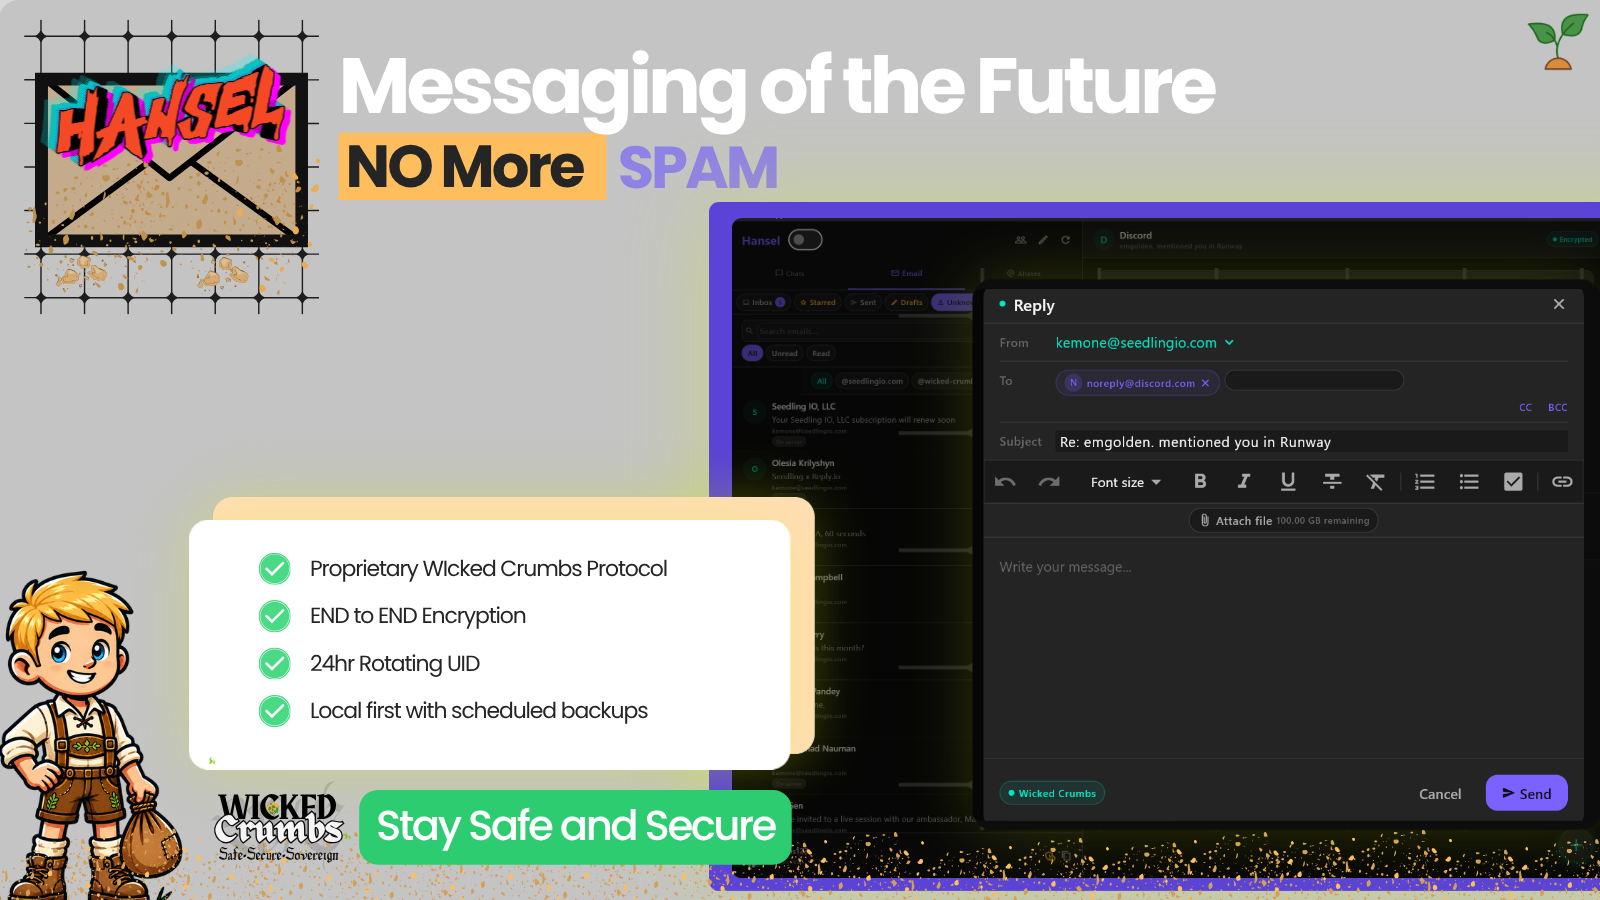
Wicked Crumbs

E2E encrypted messaging with rotating cryptographic identifiers every 15 minutes. Device-bound keys. Tamper-evident chains.

Explore Protocol 📧
📬

Sovereign Email

Your SMTP. Your domain. Intelligent auto-sorting. Encrypted serialization. Full organizational ownership of every message.

Explore Email 📧
🛡️

Admin Controls

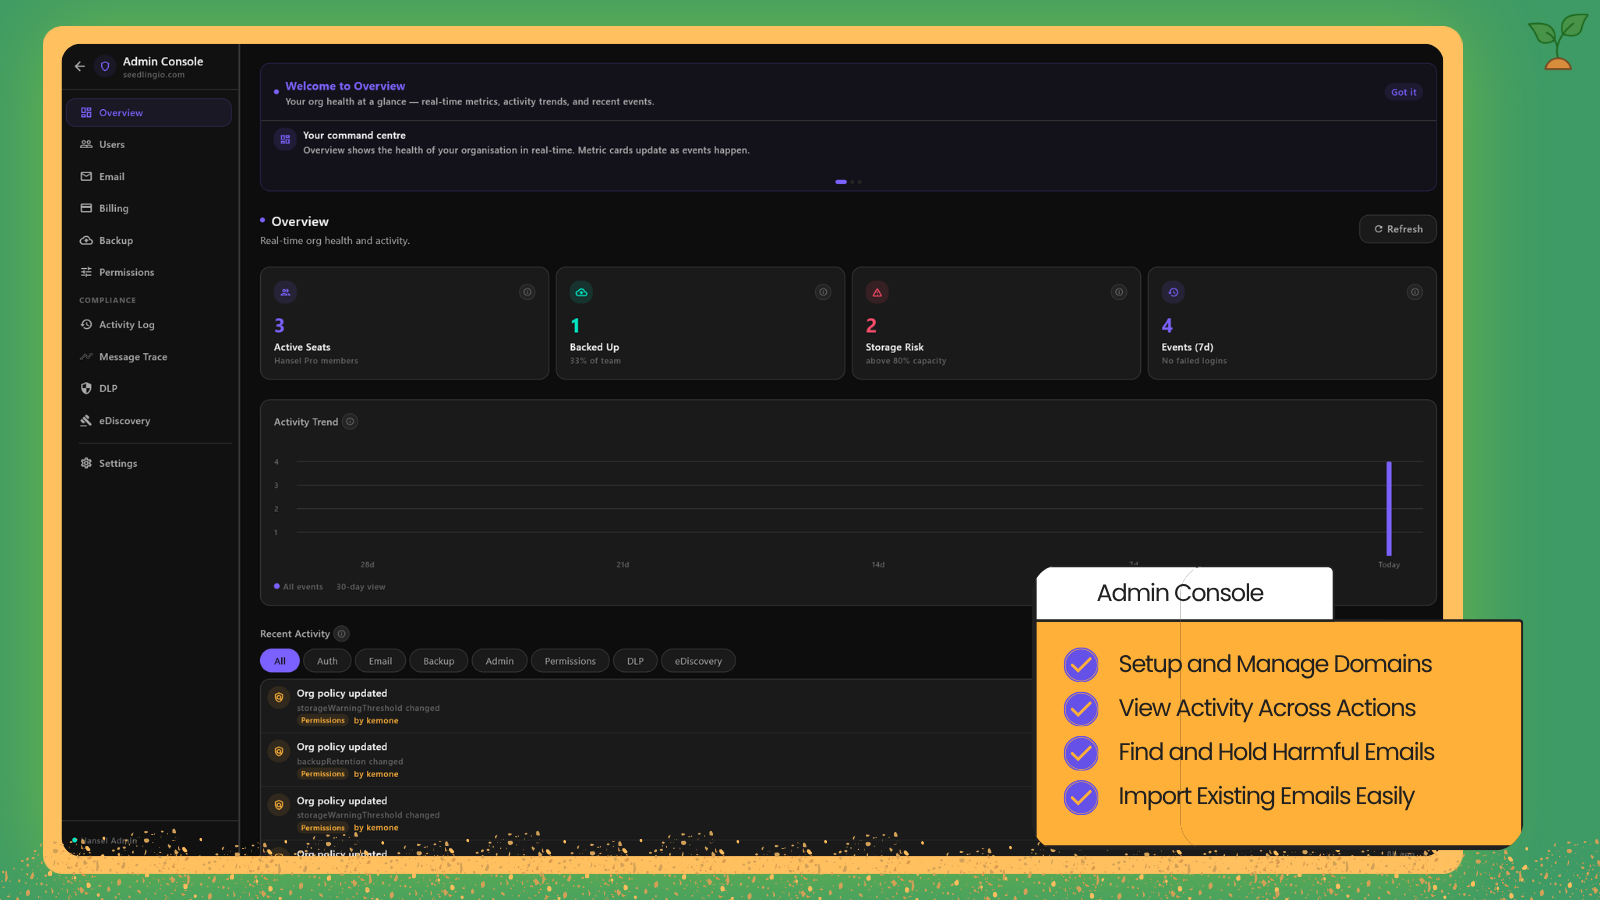
RBAC seat management, DLP, eDiscovery, 365-day immutable audit logs, and real-time org health monitoring.
Explore Admin 📧
Hansel Welcome
Inbox Experience
Admin Console
Admin Console
DLP
DLP Engine
Backups
Backup System
SOVEREIGN POWERHOUSE

Infrastructure you actually own.
Security that never asks for permission.

🧬

Wicked Crumbs Protocol

Industry-leading encryption where keys are generated and stored only on your device. Your communication history is yours to encrypt, back up, or restore at any time.

📬

Sovereign Email Routing

Manage your own SMTP infrastructure, organize mail with intelligent algorithms, and support multiple custom domains—all without relying on a third-party relay.

🏢

Enterprise-First Design

From RBAC to message tracing and automated policy enforcement, the tools regulated industries need are built directly into your dashboard on day one.

🔒

Uncompromised Encryption

Messages that stay between you and your devices. Rotating cryptographic identities and forward-link integrity checks keep data off the server entirely.

📊

Admin-Driven Control

Real-time security intelligence, instant audit export, and complete infrastructure visibility. Compliance tools architecturally enforced, not bolted on.

🏗️

True Infrastructure Ownership

Own your email standards and your user data. No platform dependency means no sudden policy changes, pricing hikes, or locked-out accounts.

Communication infrastructure built to replace what you rent with what you own.
The sovereign communication layer for modern organizations.

PRICING & PLANS

Choose Your Level of Control.

From personal sovereignty to enterprise compliance. No lock-in. You own everything.

🌐
Sovereign
Free
Forever yours
  • ☑️Personal email (1 domain)
  • ☑️Wicked Crumbs messaging
  • ☑️Local device storage
  • ☑️Device-bound keys
  • ☑️Sovereign Reset
  • ☑️Cloud storage
  • ☑️DLP / eDiscovery
  • ☑️Admin dashboard
Get Started Free
🚫
Sovereign Connected
Free
+ Group messaging
  • ☑️Everything in Sovereign
  • ☑️Wicked Crumbs group messaging
  • ☑️1 connected integration
  • ☑️Priority message delivery
  • ☑️Custom domain email
  • ☑️Cloud backup storage
  • ☑️DLP / eDiscovery
Get Started Free
Most Popular
⭐
Sovereign Pro
$4/mo
Per user, billed monthly
  • ☑️Everything in Connected
  • ☑️Custom domain email
  • ☑️15 GB cloud storage
  • ☑️Unlimited integrations
  • ☑️Encrypted backup & restore
  • ☑️Priority support
  • ☑️Admin dashboard
  • ☑️DLP / eDiscovery
Start Pro
🏢
Business Essentials
$7/seat/mo
For growing teams
  • ☑️Everything in Pro
  • ☑️Custom domain email for team
  • ☑️Seat management & RBAC
  • ☑️30 GB per seat storage
  • ☑️Team admin console
  • ☑️DLP engine
  • ☑️eDiscovery & legal hold
  • ☑️365-day audit logs
Start Essentials
⚔️
Business Professional
$12/seat/mo
Full enterprise flagship
  • ☑️Everything in Essentials
  • ☑️Full DLP & eDiscovery
  • ☑️100 GB per seat storage
  • ☑️365-day immutable audit logs
  • ☑️Legal hold & export (PST/MBOX)
  • ☑️Org backup compliance
  • ☑️Message tracing forensics
  • ☑️Security intelligence dashboard
Book a Call

All plans billed monthly as shown — discounted yearly options available.

All prices in $USD.

ONE STACK

One Stack. Sovereign at Any Scale.

What's Shipping

ANSWERS

Find the Answers
that you need.

Everything you need to know about Hansel's features, pricing, encryption, and sovereignty principles.

"Sovereign" means you own and control the infrastructure your communications run on —a third-party vendor. When you use Google Workspace or Microsoft 365, those platforms hold your encryption keys, control your data residency, and can revoke your access without warning. Hansel was literally built after a real organization was locked out of Google overnight. Sovereign communication means your SMTP is yours, your encryption keys never leave your device, and you have a Sovereign Reset option that gives you a clean exit at any time.

Wicked Crumbs is Seedling's proprietary cryptographic protocol. Your encryption keys are generated and stored exclusively on your device — Hansel's servers never see your plaintext. Every 15 minutes, your cryptographic identifier rotates, making long-term surveillance correlation computationally infeasible. Messages are chained with tamper-evident hashes, so any alteration to historical messages is detectable client-side. Identity verification happens through QR code exchange, eliminating impersonation at the protocol level.

iOS and Android clients are currently shipping — this is Hansel's highest-priority platform expansion right now. Hansel's core services, including the Wicked Crumbs protocol, Lambda services, and email infrastructure, are platform-agnostic, meaning the underlying sovereign infrastructure does not change when the client runs on a mobile device. The mobile apps will bring the full Hansel messaging and email experience to the devices you carry every day.

DLP (Data Loss Prevention) scans every outbound email for sensitive information — credit card numbers, SSNs, API keys, PHI — before it ever leaves your organization. If a pattern is detected, the system can block the email, flag it for review, require approval, or auto-redact the sensitive content. If your organization handles any sensitive client, financial, or healthcare data, DLP is not optional. Hansel includes it in Business Essentials at $7/seat — Google and Microsoft require $20–30/user enterprise tiers for equivalent functionality.

Yes — custom domain email is available starting from Sovereign Pro at $4/month. You bring your domain (e.g., me@mybusiness.com) and Hansel provisions the sovereign SMTP infrastructure behind it. The admin console auto-generates your SPF, DKIM, and DMARC DNS records with clear setup instructions, and your domain health is monitored in real time. For teams, Business Essentials and Professional allow you to provision custom domain email addresses for every seat across your entire organization from a single admin console.

Business Essentials ($7/seat/mo) covers custom domain email, seat management, RBAC, a team admin console, 30GB per seat, and the DLP engine — ideal for growing teams that need organizational email controls without deep compliance requirements. Business Professional ($12/seat/mo) adds the full compliance stack on top: eDiscovery with legal hold and export (PST/MBOX/JSON/CSV), 365-day immutable audit logs, message tracing forensics, org-wide backup compliance monitoring, and 100GB per seat. If your organization operates in a regulated industry — legal, healthcare, finance — Professional is the tier designed for you.

Your data is yours — always. Cancelling a Hansel subscription does not mean the platform becomes the owner of your data. You retain full access to export your data before cancellation. If you want a completely clean break, Sovereign Reset allows you to wipe your local profile, trigger server-side cleanup, and return to a factory-fresh state with no residual data or orphaned records. This is a fundamental design principle of Hansel: platform dependency should never trap your data.

Hansel is built for everyone. The reason it can serve such a broad range — individual professionals, startups, and regulated enterprises is that sovereignty is not a company-size problem. A journalist protecting a source, a founder protecting an acquisition discussion, a law firm managing sensitive client communications, and a multinational corporation managing cross-regional infrastructure all share the same underlying need: control the infrastructure your communications depend on. The Sovereign free tier starts at $0, forever, with no expiration.

Hansel's backup system serializes your complete communication state — all email threads, messages, attachments, folder structure, and read/unread status — into an encrypted, Gzip-compressed snapshot. Every backup is timestamped, allowing you to restore to any prior state. Business Professional adds scheduled automatic backups (daily, weekly, or custom cadence) that run silently in the background, plus an org-wide admin dashboard showing per-user backup compliance rates, last backup timestamps, and storage consumption across the entire organization.

Still have questions about pricing specifically?

Own Your Communication Stack.

From personal sovereignty to enterprise compliance. Free forever on the base tier.

Get Hansel Free
PRODUCT — SOVEREIGN EMAIL

Your Email.
Your Infrastructure.

Custom domains, sovereign SMTP, intelligent auto-sorting, and encrypted serialization. No third-party relay. No vendor lock-in. Every message belongs to you.

Sovereign SMTP Architecture

Hansel provisions your own SMTP infrastructure — no shared relays, no dependency on Google or Microsoft. Your domain's SPF, DKIM, and DMARC records are auto-generated and managed from your admin console. Messages never pass through infrastructure you don't control.

  • ☑️ Custom domain provisioning with DNS record auto-generation
  • ☑️ SPF / DKIM / DMARC managed from admin console
  • ☑️ No shared relay infrastructure
  • ☑️ Intelligent auto-sorting: Inbox, Unknown Senders, No Reply, Notifications, Spam
  • ☑️ Encrypted serialization Gzip + encryption at rest
  • 🗓️ Hansel-to-Hansel E2E email encryption Building Next
Hansel Welcome
💾

Backup Serialization

All email data serialized to encrypted snapshots with timestamped restore points.

📜

Gzip Compression

Efficient Gzip compression before encryption reduces storage footprint without sacrificing security.

🔄

Sovereign Reset

Local wipe, server cleanup, factory-fresh state. No residual data, ever.

MORE TOOLS

More Tools to Help You
Scale Your Business

Infrastructure that keeps your operations running smoothly, securely, and on your terms.

SECURITY POSTURE

Stay Secure with Infrastructure
You Actually Own

Cryptographic boundaries, zero-knowledge encryption, and administrative controls built to outlast platform dependency.

0
Platform-Accessible Keys

Private cryptographic keys are generated and stored exclusively on your device. The infrastructure operator has zero mathematical ability to access, read, or decrypt message content or email history—regardless of external requests or policy shifts.

365-Day
Immutable Audit Retention
Business Professional

Every administrative, authentication, and routing event is logged with tamper-evident timestamps. Full 12-month retention ensures legal hold readiness, compliance reporting, and forensic visibility—without archival gaps or vendor lock-in risks.

100%
Infrastructure Ownership

Your SMTP routing, custom domains, and serialized data live under full organizational control. No platform tenancy means forced feature rollouts, pricing overrides, or account dependency never apply to your stack.

Rooted in Wicked Crumbs boundaries and sovereign architecture

PLANS

Choose the plan that's
right for you

Start Free
Sovereign & Sovereign Connected
$0 / forever
Storage
Local-first storage
Zero platform lock-in
Security
Wicked Crumbs keyless encryption
By default, on every tier
Visibility & Support
Full GitBook docs & GitHub release access
Everything you need to get started
Next-Gen Capabilities
QR identity exchange & rotating identifiers
Cryptographic privacy at the protocol level
Recommended
Business SKU
Business Essentials
$7 / seat / mo
Storage
30 GB per seat
Shared org pool, auto-scaled
Team Provisioning
Seat management, unified admin dashboard
Cross-domain routing included
Compliance
DLP patterns, eDiscovery search & legal hold
+ 365-day immutable audit trail retention
Admin Health Snapshots
Per-user backup compliance tracking
Priority routing channel included
Message Tracing Forensics
Sovereign contact sync & device management
Roadmap

* Business Essentials includes all free-tier capabilities scaled for team deployment. Storage pools across seats per organization. Compliance & forensic tooling upgrade automatically to Business Professional ($12/seat) when DLP or legal hold requirements scale.

FAQS

Curious about
Sovereign Email?

Take a look at our FAQs to learn more.

Sovereign email means you own and operate the infrastructure your email runs on. Instead of routing messages through Google's or Microsoft's shared servers, Hansel provisions a dedicated SMTP infrastructure behind your own custom domain. Your DNS records (SPF, DKIM, DMARC) are auto-generated from your admin console. Your messages never pass through infrastructure you don't control — and you can take your data and exit at any time using Sovereign Reset.

Yes. Custom domain email is available on Sovereign Pro ($4/month) and all Business tiers. You bring your domain — for example, you@yourbusiness.com — and Hansel provisions the sovereign SMTP infrastructure behind it. The admin console auto-generates the exact SPF, DKIM, and DMARC DNS records you need, with clear setup instructions. Domain health is monitored in real time so you always know its verification status. For teams, Business Essentials and Professional allow you to provision custom domain addresses for every seat across your entire organization from a single admin console.

Hansel uses an intelligent algorithmic routing engine to automatically classify and sort all incoming messages into purpose-built folders: Inbox (verified contacts), Unknown Senders (quarantined until you approve), No Reply (automated transactional emails such as receipts and confirmations), Notifications (platform alerts from apps and services), and Spam (algorithmic junk filtering). This means unknown senders cannot reach your attention by default — you control who has access to your inbox, not an algorithm owned by a third party.

Hansel's backup system serializes your complete email state — all threads, messages, attachments, folder structure, and read/unread markers — into a single encrypted snapshot. Before storage, data goes through a serialization 📧 Gzip compression 📧 encryption pipeline. Every backup is timestamped so you can restore to any prior state. Business Professional adds scheduled automatic backups (daily, weekly, or custom cadence) that run silently in the background, plus an org-wide admin view showing per-user backup compliance rates and storage consumption.

Yes — Hansel-to-Hansel email encryption is actively Building Next. When both the sender and recipient are Hansel users, Hansel will encrypt the outbound email content using the recipient's Wicked Crumbs public key before the message is transmitted via SMTP. The message still travels across standard email infrastructure, but instead of readable content, the email carries an encrypted payload that only the recipient's private key — held exclusively on their device — can decrypt. Standard email infrastructure. Sovereign message content.

Sovereign Reset is a complete exit mechanism built into Hansel. It wipes your local profile data, triggers a server-side cleanup of all associated records, and returns your device to a factory-fresh Hansel state — no residual data, no orphaned records. You'd use it if you're leaving Hansel entirely and want a clean break, or if you need to reprovision your identity from scratch. This is a core design principle: platform dependency should never trap your data. You own your data, and you have a clean, architecturally-enforced way to take it back.

Ready to Own Your Email?

Get Hansel 📧
Wicked Crumbs

The Wicked Crumbs Protocol

End-to-end encrypted messaging with rotating cryptographic identifiers, device-bound keys, and tamper-evident chains.

Cryptographic Message Flow

Device-Bound Keys & Rotating Identifiers

Every 15 minutes, Wicked Crumbs rotates your cryptographic identifier. This prevents long-term correlation of your messages even if traffic analysis is attempted. Your keys are generated and stored exclusively on your device — Hansel infrastructure never sees plaintext.

  • ☑️ Random timed cryptographic ID rotation
  • ☑️ Device-bound key pairs — no server-side keys
  • ☑️ Tamper-evident crumb chains with forward-link integrity
  • ☑️ QR code identity verification
  • ☑️ Impersonation prevention via cryptographic UID
Identity

Cryptographic Identity

QR code verification pairs your identity to your device keypair. No phone number required.

🔗

Tamper-Evident Chains

Every message references the previous hash. Any tampering breaks the chain — detectable immediately.

💥

Group Messaging Shipping Now

Hybrid encryption with device-held group key state. Scales to teams without compromising E2E security.

Wicked Crumbs vs Signal Protocol

Feature Wicked Crumbs Signal Protocol
SHIPPING NOW 🚀 Group Messaging

The Group Key
Model

Traditional encrypted groups often bottleneck on server-side key management or force platforms to hold master keys for every conversation. Wicked Crumbs flips this: each participant's device maintains the current cryptographic state.

Using a hybrid encryption model, messages are efficiently distributed without requiring identical heavy cryptographic operations for every member. This architecture scales mathematically — no artificial group caps, no performance degradation as membership grows, and zero reliance on a central authority to manage group trust.

🔒
Device-Held State

Each member's device independently maintains the current group key state. No central authority required.

🔗
Hybrid Encryption

Efficient key distribution without per-member heavy cryptographic operations on every message.

📊
Mathematical Scaling

No artificial group caps. No performance degradation as membership grows. Scales by design.

🛡️
Zero Central Trust

No server holds master keys. No platform authority over group trust. Privacy by architecture.

🌐
Group Key
State
📱
Device A
💻
Device B
🖥️
Device C
📲
Device D

Decentralized Key State Propagation

CRYPTOGRAPHIC IDENTITY

Cryptographic Identity &
The QR Verification Layer

Email addresses and passwords are easily spoofed, harvested, or reused. Wicked Crumbs replaces credential-based trust with mathematical proof of identity.

🔒

Identity Through Math, Not Policy

Users establish contact by exchanging cryptographic public keys via QR scan in-person or through trusted networks. This creates a verifiable, tamper-proof connection graph.

Impersonation isn't just blockedit's architecturally impossible. The recipient's device validates the sender's crumb chain against their locally stored key pair before rendering anything.

No credential. No password. Pure cryptography.
01

QR Code Key Exchange

Each user's Hansel identity is anchored to a cryptographic key pair generated on their device. Connecting with someone means exchanging public keys via QR scan — in person or through a trusted digital channel. No central directory. No server-mediated introduction.

02

Tamper-Proof Connection Graph

Once keys are exchanged, a verifiable connection is established. Every subsequent message is cryptographically signed against the stored public key. The connection graph cannot be spoofed retroactively — altering any link in the chain breaks the mathematical proof instantly.

03

Device-Side Validation Before Render

Your device validates the sender's crumb chain against the locally stored key pair before rendering a single message. Nothing reaches your screen without passing cryptographic proof of sender identity. The platform has no role in this — it happens locally, every time.

04

Impersonation is Architecturally Impossible

Without possession of the sender's private key — held exclusively on their device — it is mathematically infeasible to forge a valid crumb chain. There is no credential to steal, no password to reset, and no account recovery flow that can be social-engineered. Identity is proof, not policy.

0
Central Identity Servers

No directory service, no username database, no account recovery server. Identity is established peer-to-peer via cryptographic key exchange.

QR
Scan-to-Trust Protocol

A single QR scan exchanges cryptographic public keys and establishes a verified, tamper-proof identity link between two devices.

♾️
Infeasible to Forge

Without the private key on the sender's device, no valid crumb chain can be constructed. Mathematical infeasibility is the enforcement mechanism —policy, not moderation.

Metadata Blindness Surveillance Resistance

Metadata
Blindness &
Surveillance Resistance.

Even when message content is encrypted, metadata can map entire communication networks. Wicked Crumbs neutralizes this by continuously rotating encrypted identifier paths. Your outbound routing signatures shift on a fixed cycle, breaking traditional call-graph analysis and contact-harvesting models.

Third parties cannot reliably track who communicates with whom, because the metadata itself is cryptographically blinded and non-persistent. Surveillance at scale requires predictable paths. Hansel removes them.

🔄
Rotating Paths

Identifier rotation breaks call-graph correlation across sessions.

🕶️
Blind Metadata

Routing signatures are cryptographically blinded and non-persistent.

🚫
No Predictable Path

Mass surveillance requires consistent routing. Wicked Crumbs denies it.

"Surveillance at scale requires predictable paths.
Hansel removes them."

🏛️¨ Building Next CRYPTOGRAPHY ROADMAP

Forward-Looking
Cryptography

Long-lived encryption keys create a historical vulnerability: compromise of one key can expose past communications. Hansel's next cryptographic evolution introduces per-message key derivation.

Every exchange will generate a session-specific key that expires immediately after use. Even if a current key is compromised, historical messages remain mathematically isolated and protected.

This aligns Wicked Crumbs with modern forward-secrecy standards while preserving your sovereign architecture.

"Today's keys should not become yesterday's messages."

PFS Roadmap Status

Perfect Forward Secrecy is actively Building Next — part of the near-term cryptographic strengthening of the Wicked Crumbs protocol.

Try Wicked Crumbs Protocol

Download Hansel 📧
Admin Console
ADMIN DASHBOARD

The Sovereign
Command Center.

RBAC seat management, DLP engine, eDiscovery, 365-day immutable audit logs, and real-time org health. Full enterprise control from a single console.

Real-Time Org Health Monitoring

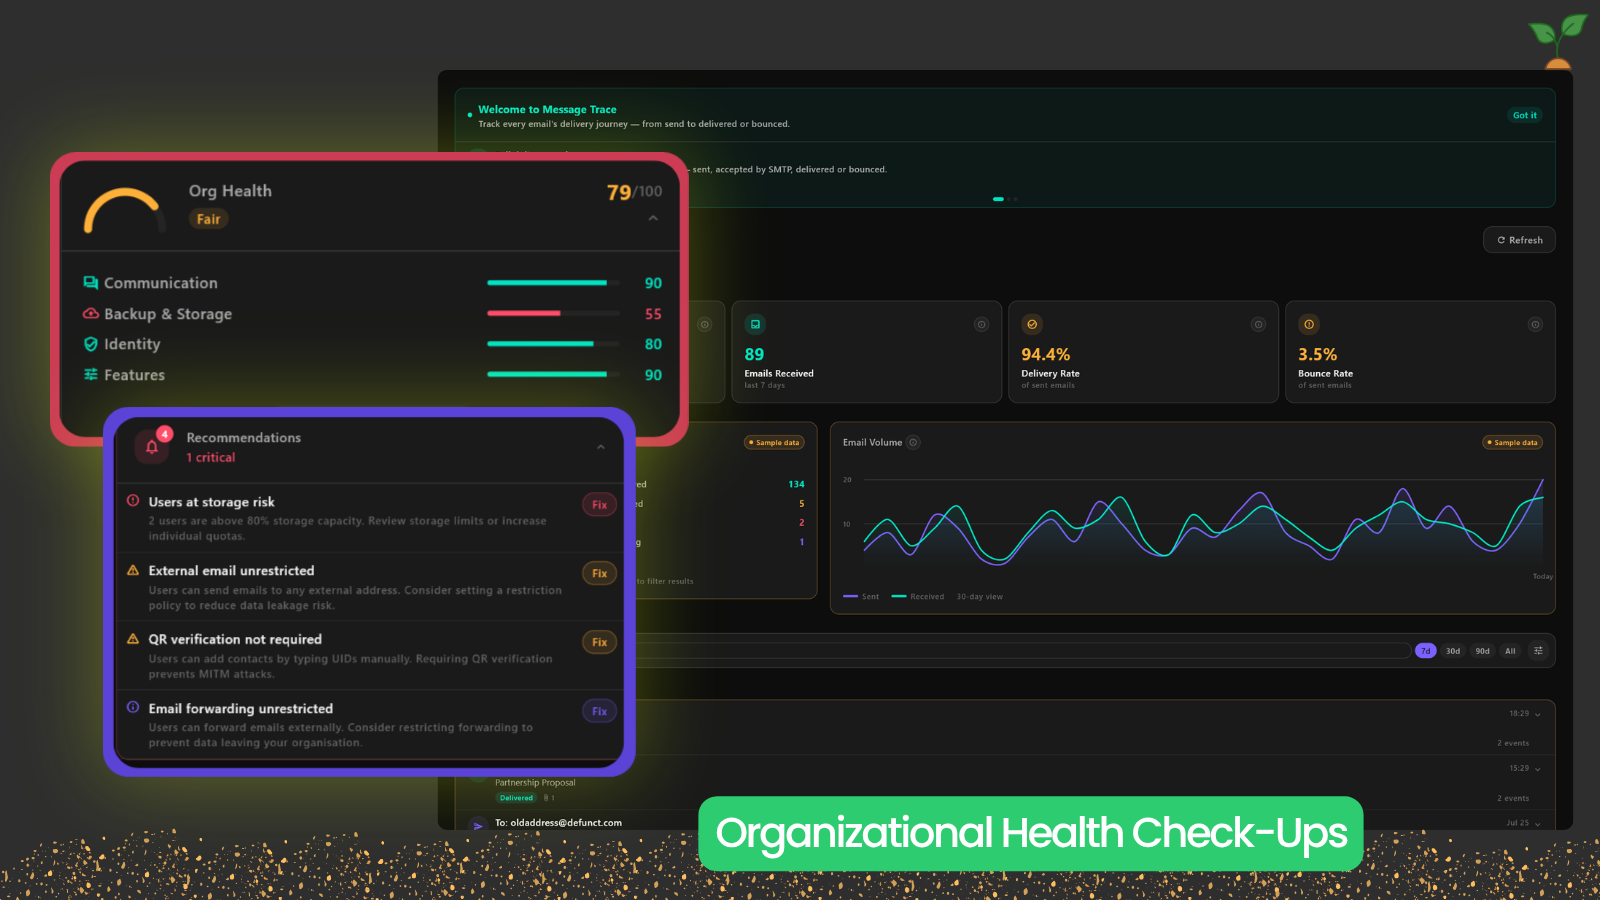
Monitor communication health across your organization in real-time. Backup compliance rates, delivery health, DLP trigger frequency, and seat activity — all surfaced in a unified health dashboard.

  • ☑️ Real-time communication health signals
  • ☑️ Per-user backup compliance rates
  • ☑️ Delivery anomaly detection
Org Health
Policy Config

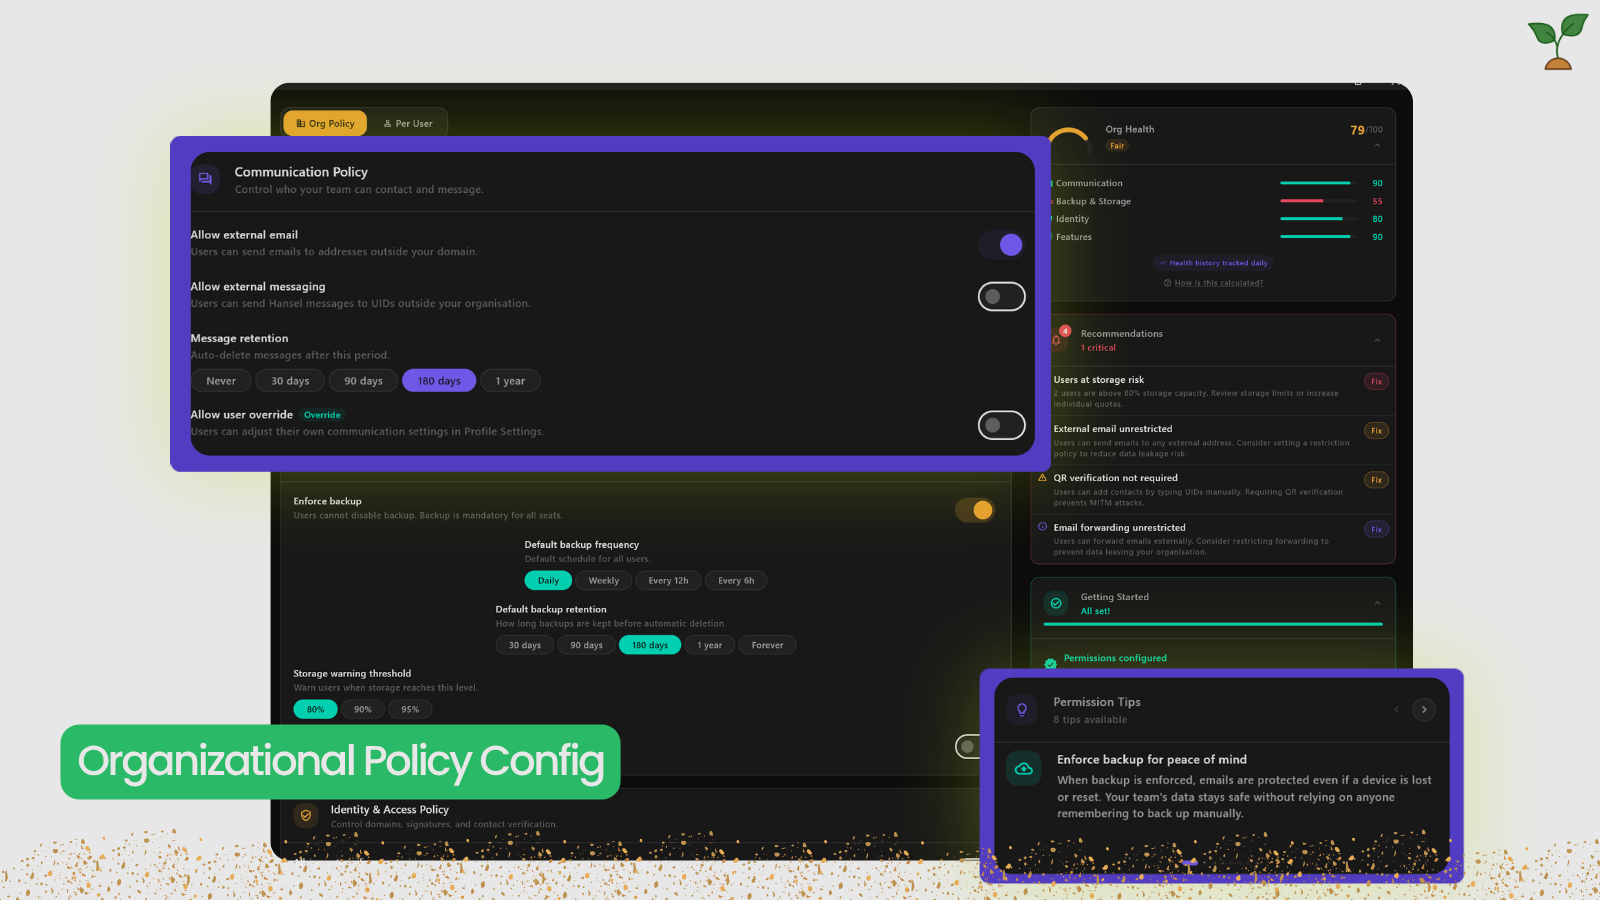
RBAC & Policy Enforcement

Four-tier role system: Super Admin, Dept Admin, Standard User, Read-Only Auditor. Define communication policies at org level — retention windows, external domain restrictions, encryption tier mandates, legal hold parameters.

Super Admin
Full org control
Dept Admin
Team-scoped control
Standard User
Standard access
Read-Only Auditor
Compliance view only

Data Loss Prevention

Pattern-based DLP policies intercept sensitive data before it exits your perimeter. Configure custom regex patterns, keyword triggers, and classification policies. Policy actions: block, flag, approve, or redact. Every trigger creates an immutable audit entry.

  • ☑️ Pattern library: SSN, credit cards, API keys, PHI
  • ☑️ Actions: Block / Flag / Approve / Redact
  • ☑️ Full audit trail for every DLP event
DLP
eDiscovery

eDiscovery & Legal Hold

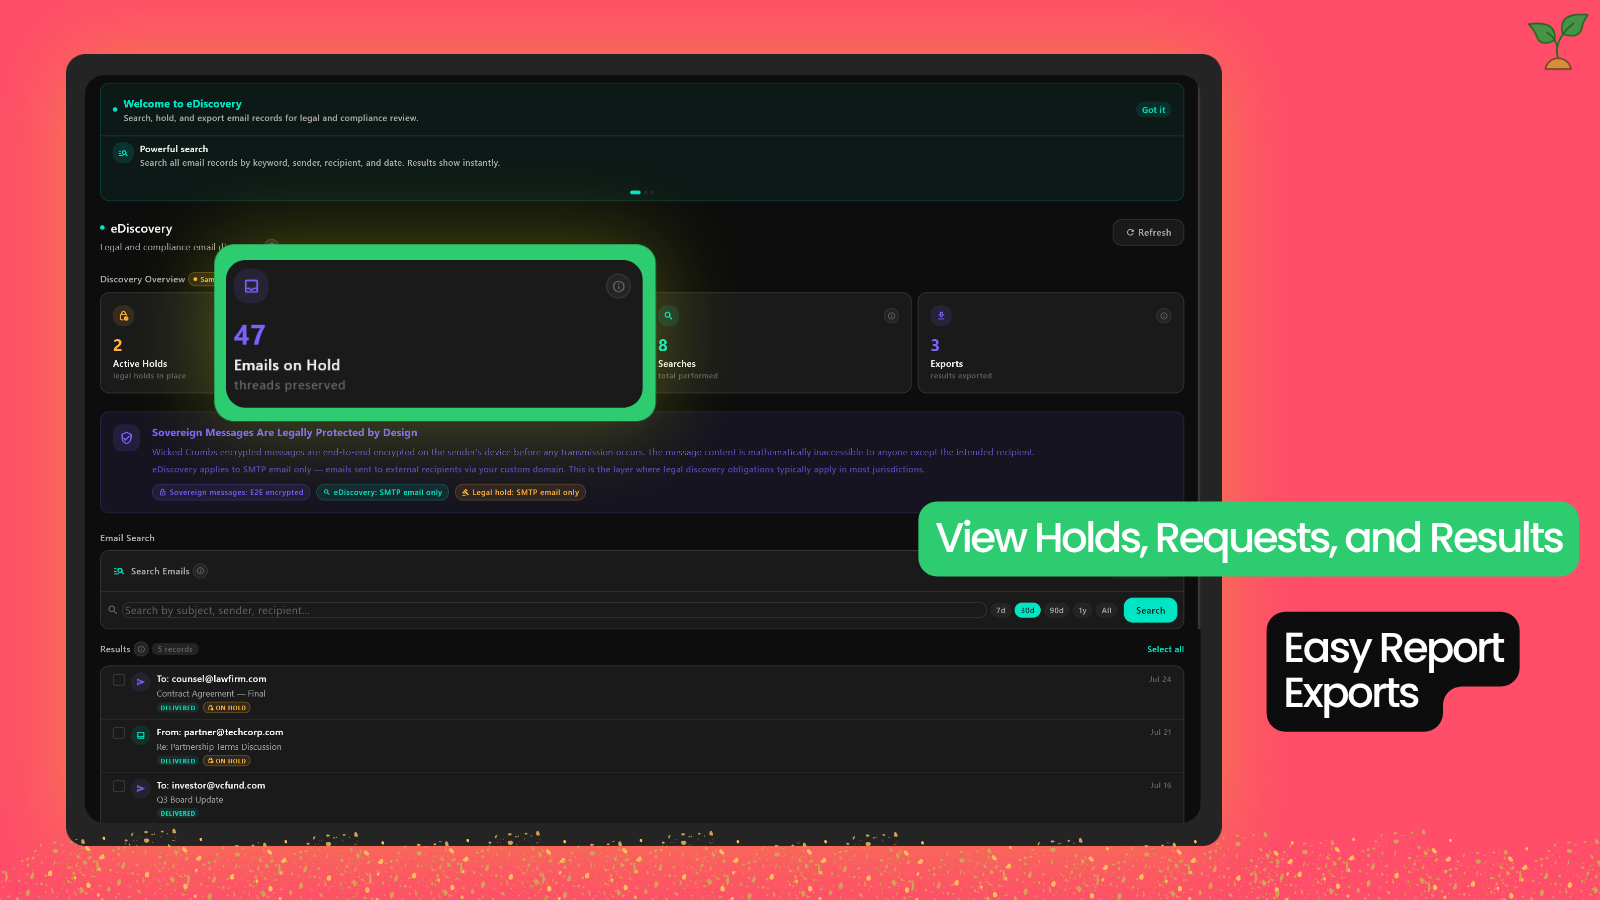
Keyword and pattern search across your entire communication history. Apply legal holds in seconds. Export to PST, MBOX, JSON, or CSV. 365-day immutable audit logs for full compliance posture.

  • ☑️ Cross-channel keyword and pattern search
  • ☑️ Legal hold management with chain-of-custody tracking
  • ☑️ Export: PST / MBOX / JSON / CSV
  • ☑️ 365-day immutable audit logs
SAFER WORK

Safer work with granular,
controls

Move your entire organization's communication infrastructure in one pass. Preserve history, identity, and sovereign control from day one.

DATA PORTABILITY Business Professional

Forensic Export &
Sovereign Data Portability

Enterprise data shouldn't be trapped behind export walls or proprietary formats. Hansel's administrative controls treat data continuity as a first-class entitlement, giving admins full visibility, retention control, and zero-attrition migration paths — whether for compliance audits, legal reviews, or sovereign infrastructure swaps.

📦

Full Metadata-Preserving Export Suite

eDiscovery results, audit trails, and email archives export cleanly to PST, MBOX, JSON, and CSV formats with complete header retention, thread mapping, and cryptographic crumb chain integrity.

PST MBOX JSON CSV
⚖️

Legal Hold & Chain-of-Custody Tracking

Every export, search, or data handoff generates a tamper-evident log entry. Timestamps, admin IDs, and query scopes are preserved for legal and regulatory verification.

Tamper-Evident Logging
🚫

Seamless Sovereign Migration Paths

Admins can trigger full org archival in parallel with legacy provider routing. MX/SPF/DKIM records route cleanly, ensuring zero message loss during transition phases.

MX SPF DKIM
🏛️

True Sovereign Reset Enforcement

On decommission or seat revocation, the system executes a complete profile wipe: local data cleared, server-side orphaned records eliminated, and cryptographic keys permanently revoked. No residual data remains accessible.

Zero Residual Data
Sovereign Data Entitlement

"Enterprise data shouldn't be trapped behind export walls or proprietary formats. Data continuity is a first-class entitlement —a premium add-on."

REAL OPERATIONS

Built for Real Operations.
Not Theoretical Promises.

1.

Administrative efficiency, unlocked across every seat.

One unified console manages seats, domains, policies, DLP, and audit logs. Automate onboarding, enforce compliance baselines, and monitor org health in real time—cutting overhead without sacrificing direct control.

2.

Smooth migration without breaking continuity.

Drag-and-drop mailbox imports, bulk seat provisioning, and parallel DNS routing handled from the same dashboard. Track progress per user, preserve thread history, and switch MX/SPF/DKIM records seamlessly—so you go live without legacy data loss or service interruption.

3.

Verified protection, architecturally enforced.

From DLP pattern blocking and DMARC enforcement to immutable audit trails and legal holds, every compliance control runs on device-to-device cryptography. No bolt-on fees. No platform tenancy. Just continuous, verified security by default.

POLICY INTELLIGENCE Business Professional

Automated Policy Health
& Compliance Gap Detection

Policy management shouldn't require manual audits or quarterly compliance checklists. Hansel's admin console continuously monitors organizational security posture against active policy settings, automatically surfacing configuration gaps before they become risks.

From DMARC enforcement to backup frequency and identity verification, the dashboard acts as a living compliance engine —just a settings repository. Every misconfiguration is flagged in real time, every enforcement action is logged to the immutable audit trail.

📊

Continuous Policy Scoring

Admins receive a real-time Health Score calculated from active permissions, backup compliance rates, and security baseline adherence across all seats. No manual audit required.

🚨

Automated Gap Detection

Systems flag misconfigurations instantly: expired DNS records, unenforced 2FA policies, missing retention rules, or inactive DLP patterns. Surface risk before it becomes an incident.

⚖️

Framework-Aligned Enforcement

Policies map directly to architectural requirements for SOC 2, GDPR, and HIPAA alignment — including immutable audit capture and tamper-evident logging for every enforcement action.

🎛️

Granular Override Layer

Org-wide baselines can be locked while individual users or departments receive scoped permissions — e.g., me@company.com allows external forwarding while finance@company.com remains DLP-restricted.

Policy Enforcement Flow
01
Policy Set
02
Continuous Scan
03
Gap Flagged
04
Admin Alerted
05
Audit Logged

"The dashboard acts as a living compliance engine —just a settings repository."

Policy Health Console
Org Health Score
/ 100
Live  Updated just now
Active Gap Alerts
🚀
2FA Policy Not Enforced
3 seats in Finance dept missing mandatory 2FA enforcement
🏛️
DLP Pattern Inactive
SSN detection pattern disabled — 0 events logged in 14 days
Policy Baseline
DMARC Enforcement ☑️ Active
Backup Compliance Rate 94%
DLP Active Patterns 4 / 5 🚀
2FA Enforcement Partial ☑️
Audit Log Retention 365 days ☑️
hansel.admin · policy.engine
Business Professional
AdminOrganizationPolicyConfig
Policy Config View

Enterprise Feature Pricing Comparison

Feature Google Workspace
$6–$18/user/mo
Microsoft 365
$6–$22/user/mo
Hansel Business Pro
$12/seat/mo
DLP EngineEnterprise+ onlyE3/E5 only☑️ Included
eDiscoveryVault add-onE3/E5 only☑️ Included
365-day Audit LogsLimitedE5 only☑️ Immutable
Sovereign Key Ownership☑️☑️☑️ Always
Message TracingAdmin consoleAdmin center☑️ Full forensics
FAQS

Questions about
the Admin Dashboard?

Everything you need to know about enterprise controls, compliance tooling, and sovereign admin capabilities.

The Hansel Admin Dashboard is a sovereign enterprise command center —a settings page. From a single console, administrators get real-time org health monitoring across every seat, complete email domain management with auto-generated DNS records, a full billing overview, seat lifecycle management, RBAC role assignment, DLP policy enforcement, eDiscovery with legal hold, 365-day immutable audit logs, and message tracing forensics. Everything is on infrastructure your organization controls —a third-party vendor's dashboard you're renting access to.

Hansel uses a four-tier role system. Super Admins have full organizational control — seats, domains, policies, DLP, eDiscovery, billing, and all compliance tools. Department Admins have scoped control over their specific team, allowing delegation without granting root access. Standard Users have no admin privileges and operate their own account only. Read-Only Auditors can view logs, audit trails, and compliance reports but cannot make any changes — ideal for external auditors or compliance officers who need visibility without operational access.

* RBAC roles are an advanced role feature currently in Beta —yet generally available (GA).

Every outbound email passes through Hansel's DLP scanning pipeline before it ever leaves your organization. Administrators configure pattern rules — credit card numbers, SSNs, tax IDs, API keys, custom regex — and assign a policy action per rule. When a pattern is matched, the system can block the email entirely, flag it for manual review, hold it pending approval from a manager, or auto-redact the sensitive content before delivery. Every DLP event is logged with full context — who tried to send what, which rule triggered, what action was taken, and the exact timestampcreating an immutable compliance record.

eDiscovery gives administrators the ability to search, preserve, and export email records for legal, compliance, or investigative purposes. You would need it when responding to legal proceedings (litigation, regulatory investigations), audits, or internal HR investigations. Hansel's eDiscovery lets you search across all organizational email by sender, recipient, subject, message body, date range, and attachment name. You can apply legal holds that freeze specific mailboxes — preventing deletion of relevant messages — and then export findings in PST, MBOX, JSON, or CSV format for legal counsel. Every eDiscovery action is itself logged to the immutable audit trail for chain-of-custody integrity.

Business Professional retains 365 days of immutable audit logs — meaning no user or admin can alter or delete them. Every significant event across the organization is captured: authentication events (logins, failed attempts, device changes), email activity, backup events (created/restored/deleted), administrative actions (user provisioning, domain changes, DLP rule modifications, eDiscovery searches, legal holds applied/lifted), billing events, DLP trigger events, and permission changes. Logs are searchable by user, event type, date range, and severity, and are fully exportable for external compliance reporting.

Standard email logs tell you a message was sent. Message tracing tells you everything that happened to it. Hansel's message tracing shows the full delivery path — every server the message touched, delivery status (delivered, bounced, deferred, rejected), spam filter results and why they fired, SPF/DKIM/DMARC authentication pass/fail results, and the latency breakdown per hop. If a message didn't arrive, message tracing tells you exactly where it stopped and why. If a message looks potentially spoofed, message tracing surfaces the authentication failures that confirm it. Most platforms restrict this level of forensic visibility to enterprise support teams — Hansel gives it directly to your admins.

The core difference is pricing and ownership. Google Workspace requires Enterprise Plus ($30/user/mo) to unlock DLP, eDiscovery, and full audit logging. Microsoft 365 requires E3 or E5 ($22+/user/mo) for comparable compliance tooling. Hansel's Business Professional tier delivers DLP, full eDiscovery with legal hold, 365-day immutable audit logs, and message tracing forensics at $12/seat/month — roughly 40–60% cheaper. Beyond pricing, the structural difference is sovereignty: Google and Microsoft hold your encryption keys, control your data residency, and can lock you out. Hansel's admin console runs on infrastructure your organization controls, and a Sovereign Reset gives you a complete clean exit at any time.

Yes. Organizations can register and manage multiple custom email domains directly from the Hansel admin console. For each domain, the console auto-generates the exact SPF, DKIM, and DMARC DNS records you need, with clear setup instructions that don't require a support ticket or external documentation. Domain health is monitored in real time — you always have immediate visibility into the verification status of every domain your organization uses. This is particularly useful for holding companies, organizations with multiple brand identities, or businesses that have acquired other entities and need to unify email infrastructure under a single admin ledger.

Want to see how Hansel's admin compares to Google and Microsoft pricing?

Take Control of Your Organization

Get Hansel 📧
BACKUP & STORAGE

Your Data. Serialized.
Encrypted. Restored on Demand.

Gzip-compressed encrypted snapshots. Timestamped restore points. Org-wide backup compliance. Sovereign Reset capability.

What Gets Backed Up

All threads, messages, attachments, folder state, and read/unread markers are captured. Backups are serialized, Gzip-compressed, and encrypted before storage. Timestamped restore points let you roll back to any previous state.

  • ☑️ All email threads, messages, attachments
  • ☑️ Folder structure, labels, read/unread state
  • ☑️ Serialization 📧 Gzip 📧 Encryption pipeline
  • ☑️ Timestamped restore points
Backups
Local
Sovereign Free

On-device storage only

15 GB
Sovereign Pro

Cloud-backed sovereign storage

30 GB
Business Essentials

Per seat, org-managed

100 GB
Business Professional

Per seat, with admin compliance

Admin Backup Oversight

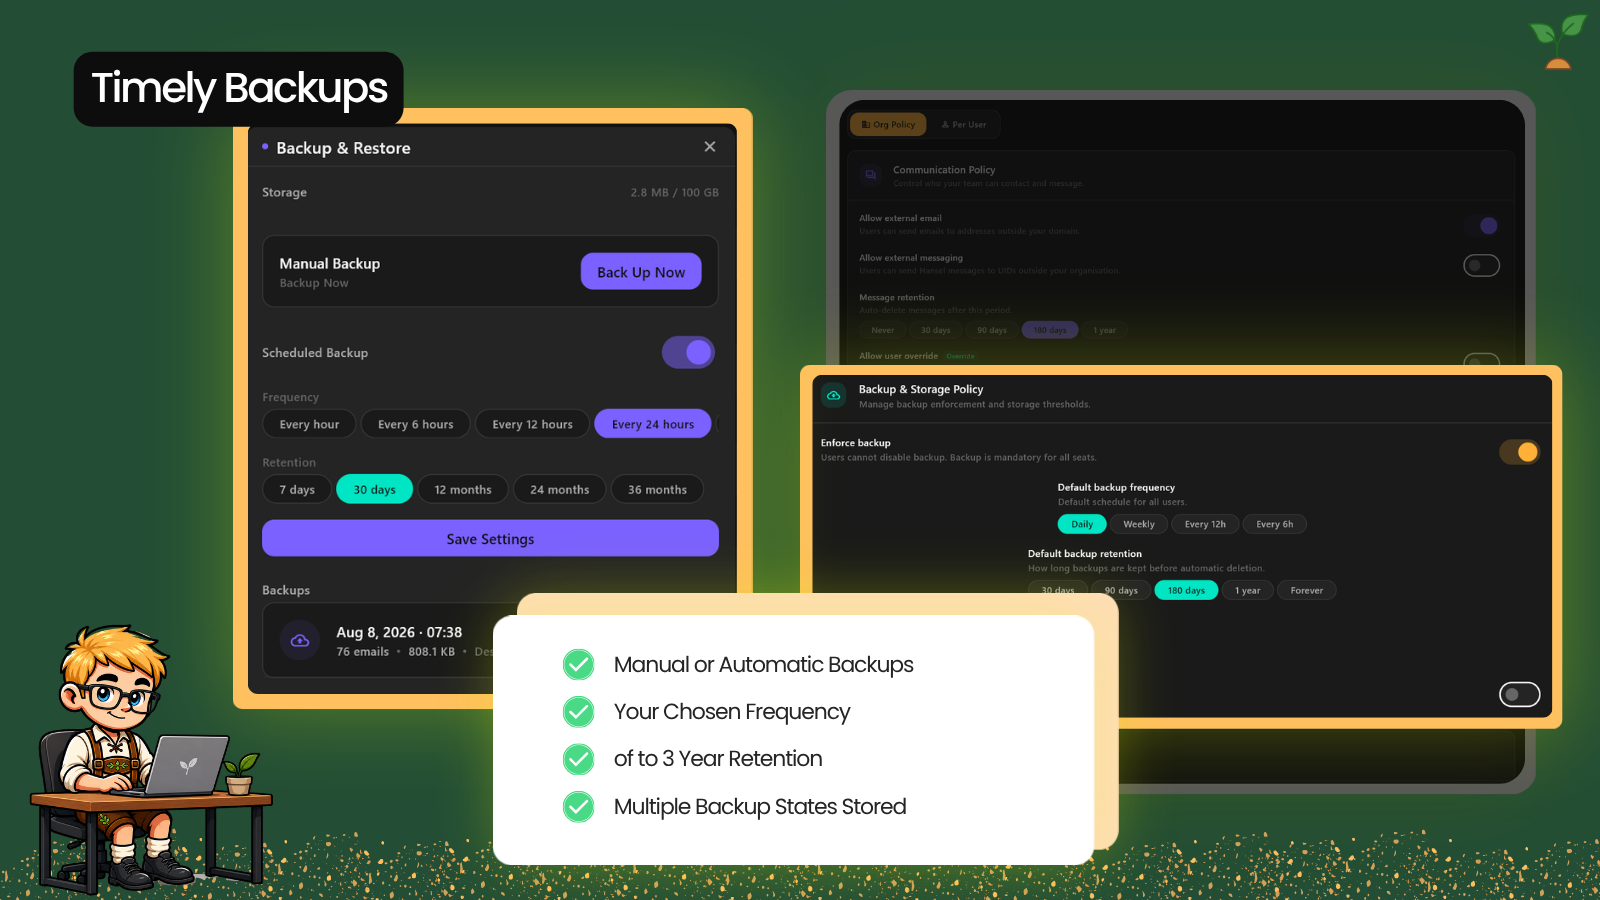
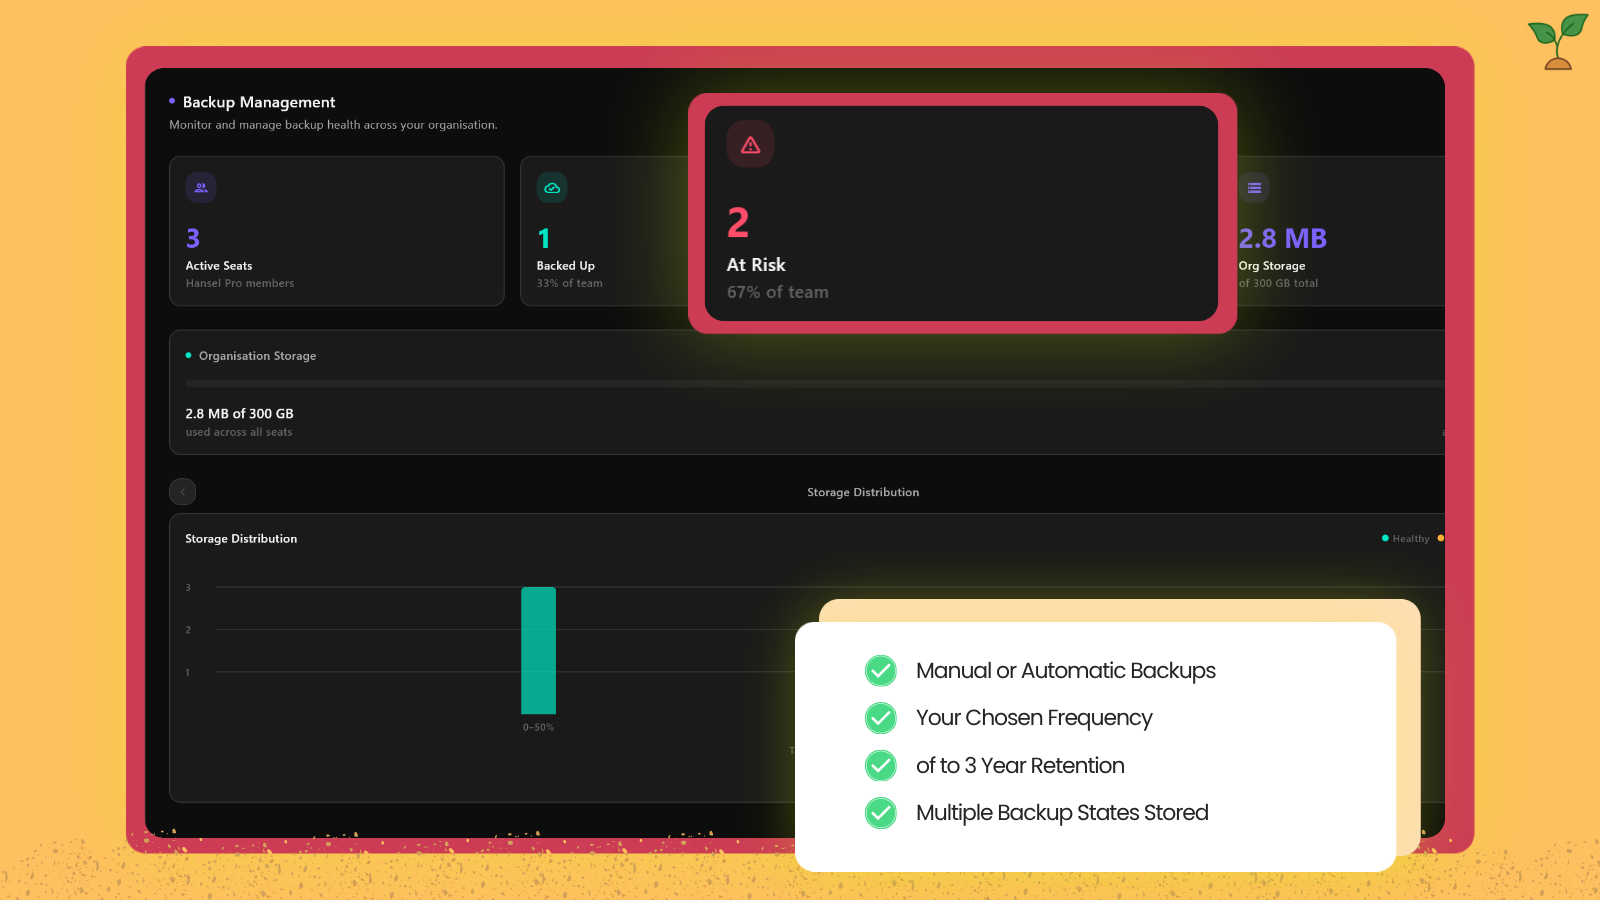
Business Professional includes org-wide backup compliance monitoring. Track per-user compliance rates, last backup timestamps, and storage consumption from the admin console. Scheduled automatic backups: daily, weekly, or custom cadence.

Admin Backup
COMPLIANCE-ALIGNED RETENTION & LEGAL PRESERVATION Business Professional

Backup Integrity Meets
Regulatory Requirements

For regulated operations, data decay is a compliance risk. Hansel aligns its backup lifecycle with business tier boundaries — preserving serialized archives in their original cryptographic state until explicitly purged or restored.

🌐
Backup Integrity

Cryptographic State Preservation

Serialized archives are preserved in their original cryptographic state until explicitly purged or restored. Business Professional seats automatically enforce 365-day immutable archival retention, ensuring backups remain legally admissible and auditable.

365-Day Immutable Retention
📦
Retention Policy

Lifecycle-Aligned Archival

Hansel aligns its backup lifecycle with business tier boundaries. Every archive path is retained across its full retention window — no silent expiry, no platform-side purge without explicit admin action. Regulated industries can rely on this as a structural guarantee, not a policy setting.

Explicit Purge Only
🔗
Chain-of-Custody

Verifiable Audit Without Intervention

Every archive path maintains chain-of-custody logging, so IT can verify integrity dates, compliance states, and export readiness without platform intervention or third-party audit dependencies. No external audit tool required — the evidence chain is native to the stack.

Native Audit Evidence
Compliance-Grade Archival

"For regulated operations, data decay is a compliance risk. Hansel's immutable archival retention ensures backups remain legally admissible without platform intervention or third-party audit dependencies."

VERSIONED SNAPSHOTS & CROSS-DEVICE CONTINUITY

Point-in-Time Recovery
Across Every Device

Backups aren't just archive files — they're versioned cryptographic snapshots. Each restore point captures thread states, attachment indices, folder hierarchy, and message flags at the exact moment of serialization.

Because Hansel operates on a local-first architecture, restored data syncs seamlessly across all authorized devices without platform intermediaries or cache fragmentation. Teams can pivot between desktop, mobile, and browser environments while maintaining exact state continuity — no sync conflicts, no orphaned attachments, zero platform dependency during restoration.

🧵
Thread States

Complete conversation chains captured at serialization time — every message, flag, and attachment index preserved.

📂
Folder Hierarchy

Full folder structure, labels, and read/unread status restored to the exact moment of backup creation.

🔗
Zero Sync Conflicts

Local-first architecture eliminates cache fragmentation and platform intermediaries during cross-device restoration.

🛡️
Zero Platform Dependency

No vendor intermediaries in the restoration path. State continuity is owned entirely by your device and your keys.

*

Mobile and browser support for Hansel is not currently generally available (GA). These capabilities will be rolled out periodically to users after the closed Beta ends, throughout open Beta, until full GA launch.

VERSIONED SNAPSHOT CHAIN SNAPSHOT v1 · T-72h 🌐 enc SNAPSHOT v2 · T-24h 🌐 enc SNAPSHOT v3 · NOW ☑️ LATEST ACTIVE RESTORATION 📧 DEVICE SYNC PATHS 🔄 RESTORE LOCAL-FIRST 🖥️ DESKTOP macOS / Win 🚀 SHIPPING NOW 📱 MOBILE iOS / Android 🏛️¨ BUILDING NEXT 🚫 BROWSER Web Client 🏛️¨ BUILDING NEXT 🧩 EXTENSION Chrome / Browser EXACT STATE CONTINUITY No sync conflicts · No orphaned attachments · Zero platform dependency 🌐 Cryptographic Snapshot · Device Keys Only
ZERO-TOUCH BACKUP ORCHESTRATION Business Professional

Scheduled Protection Without
Administrative Overhead

Business Professional organizations deploy background orchestration that runs silently across every seat. Administrators define cadence — daily, weekly, or custom intervals and the system serializes, compresses, and encrypts in parallel without impacting user workflow. Admin dashboards surface compliance rates, storage consumption deltas, and failed-job alerts instantly. It's enterprise-grade data continuity that operates autonomously, eliminating manual backup fatigue while guaranteeing predictable protection baselines across distributed teams.

AdminBackupManagement
94% Compliance
☑️ All Seats
Admin Backup Dashboard
Real-time org backup health monitoring
🗓️

Admin-Defined Cadence

Administrators set daily, weekly, or custom interval schedules per organization. Once configured, the system runs without any user-facing prompts or interruptions.

🔗

Parallel Serialization Pipeline

Serialization, Gzip compression, and encryption run in parallel across seats — zero impact on active user workflows, even during peak-usage hours.

𠓊

Instant Compliance Surface

Admin dashboards surface compliance rates, storage consumption deltas, and failed-job alerts in real time — no manual audit required to confirm organizational protection status.

Backup Schedule by Plan
Sovereign Pro $4/mo
Manual on-demand
Business Essentials $7/seat
Manual on-demand
Business Professional $12/seat
Scheduled automatic

Daily, weekly, or custom interval scheduling available exclusively on Business Professional. All tiers support manual on-demand backup at any time.

"Enterprise-grade data continuity that operates autonomously, eliminating manual backup fatigue."

Sovereign Decommission Data Lifecycle Control

Full Architectural Ownership
Through
Decommissioning.

True sovereignty includes the right to exit clean. The Sovereign Reset function executes a cryptographic purge: local device profiles are securely wiped, server-side serialized records are permanently decommissioned, and associated encryption keys are revoked at the hardware level.

No orphaned data, no dormant tenant liabilities, no vendor-held archives. For organizations migrating off-stack or retiring legacy infrastructure, this ensures complete data lifecycle closure — audited, verified, and irrevocable.

💻
Local Wipe

Device profiles securely erased. No residual local state remains.

🖥️
Server Purge

Serialized records permanently decommissioned server-side.

🎛️
Key Revocation

Encryption keys revoked at the hardware level. Mathematically final.

"No orphaned data. No dormant tenant liabilities.
No vendor-held archives."

Never Lose Your Data Again

Get Hansel 📧
Individuals

Personal Sovereignty.
No Compromise.

Whether you're a freelancer, journalist, legal professional, or privacy-conscious individual — Hansel gives you communication infrastructure that belongs to you. Sovereign free tier, forever.

Sovereign (Free)

  • ☑️ Personal email on your domain
  • ☑️ Wicked Crumbs E2E messaging
  • ☑️ Local storage — device-bound keys

Sovereign Pro ($4/mo)

  • ☑️ 15GB cloud-backed storage
  • ☑️ Unlimited integrations
  • ☑️ Priority support
THE SOVEREIGNTY SHIFT

Privacy Is an Outcome.
Sovereignty Is the
Architecture.

For individuals and independent professionals, platform dependency isn't just a privacy concernit's a structural business risk. Account suspensions, opaque policy shifts, and third-party data handling can erase years of professional infrastructure overnight.

Hansel answers this by decoupling your communications from centralized control. Your identity verification is cryptographic. Your email routing is sovereign. Privacy protects what others see; sovereignty ensures who controls the system it depends on.

🛡️

Privacy

Controls what others can see about your communications. Encryption in transit. End-to-end message protection.

🏗️

Sovereignty

Ensures who controls the system your communications depend on. Your SMTP. Your keys. Your infrastructure.

Platform Dependency Risks for Professionals
☑️

Account suspensions without warning or meaningful appeal window

☑️

Opaque policy shifts that retroactively restrict how your data is handled

☑️

Third-party data handling that can erase years of professional infrastructure overnight

"Privacy is the outcome.
Sovereignty is the architecture."

SOVEREIGN ARCHITECTURE 🧑 YOU 📬 YOUR SMTP 🔒 YOUR KEYS 💾 YOUR DATA 🔄 SOVEREIGN EXIT PLATFORM DEPENDENCY suspended · locked · no appeal SOVEREIGNTY BOUNDARY
THE ROADMAP VISION

From Sovereign Communication to
Complete Workspace Infrastructure

This is only the first layer. Hansel is actively expanding from encrypted messaging and sovereign email into a broader operational environment.

Roadmap Status

"Your infrastructure scales as your responsibilities do. From individual sovereignty to a complete workspace alternative — one deliberate layer at a time."

Domain & Alias Console
Primary Domain
me@yourbusiness.com
Sovereign SMTP · DKIM ☑️ · SPF ☑️
LIVE
Active Aliases
3 Active
clients@yourbusiness.com
Context: Client comms
Active
vendors@yourbusiness.com
Context: Vendor routing
Active
q4campaign@yourbusiness.com
Context: Campaign Q4
Revoked
identity.sovereign · alias.router
PROFESSIONAL SOVEREIGN IDENTITY

Own Your Address.
Control Your Contexts.

Solopreneurs and professionals don't need more addresses — they need precise control over who reaches them and how they're perceived. Hansel delivers custom domain provisioning with intelligent alias routing.

Assign unique contexts for clients, vendors, or campaigns without exposing your primary identity. Revoke access instantly when engagements end. Your professional brand stays isolated from noise, spam lists, and platform policy shifts.

🚫

Custom Domain Provisioning

Bring your own domain — you@yourbusiness.com — on sovereign SMTP infrastructure with auto-generated SPF, DKIM, and DMARC records.

🏛️€

Intelligent Alias Routing

Create context-specific aliases per client, vendor, or campaign. Each alias routes to your primary inbox while keeping your core identity isolated.

🔗

Instant Revocation

When an engagement ends, revoke the alias instantly. No lingering exposure. No spam list carry-over. Your primary identity stays clean.

🛡️

Platform-Policy Immunity

Your professional brand runs on sovereign infrastructure — immune to third-party policy shifts, deliverability rule changes, or platform-enforced identity resets.

"Your professional brand stays isolated from noise, spam lists, and platform policy shifts."

Available From
Sovereign Pro — $4/month
Custom domain + alias routing + 15GB cloud storage
Get Started
ARCHITECTURAL DEFENSE

Wicked Crumbs:
Encryption Without Compromise

Most platforms promise privacy but retain server-side access to your keys. Hansel's proprietary protocol eliminates that gap entirely.

📱
01

QR Identity Exchange

Cryptographic public keys exchanged via QR scan. No central directory. No server-mediated trust.

🌐
02

Device-Bound Keys

Keys generated and stored exclusively on your device. The platform never sees plaintext. Ever.

📤
03

Encrypted Transmission

Only encrypted blobs traverse the network. Infrastructure routes — it cannot read. Forward-linked crumb chain travels with the payload.

🔗
04

Chain Validation

Recipient's device validates the forward-linked crumb chain. Tampering breaks the chain — detected locally, no server trust needed.

✅
05

Device-Only Decryption

Decryption is isolated to device boundaries. Even compromised network infrastructure cannot expose message content.

Most platforms promise privacy but retain server-side access to your keys. Hansel's proprietary protocol eliminates that gap entirely. Identity verification happens via cryptographic QR exchange — making impersonation mathematically impossible.

Every message leaves a forward-linked chain that only the authorized recipient can validate. Even if network infrastructure is compromised, decryption remains isolated to device boundaries. No trust required. Just verified mathematics.

"No trust required.
Just verified mathematics."

🔄
Rotating Identifiers

Identity paths shift every 15 minutes. Long-term surveillance correlation is computationally infeasible.

🚫
Impersonation: Impossible

Without the private key, no valid crumb chain can be forged. Math enforces identity —policy.

𠏔️
Infrastructure-Agnostic

Even compromised network infrastructure cannot expose message content. Decryption is device-isolated by design.

🌱
Seedling's Own IP

Wicked Crumbs is fully proprietary built, owned, and evolved by Seedling. No dependency on third-party cryptographic libraries.

Startups

Team Infrastructure.
Without the Enterprise Tax.

Custom domain email, team seat provisioning, RBAC access control, and DLP — all at $7/seat/mo. No $18/user Workspace equivalent required.

Business Essentials ($7/seat/mo)

  • ☑️ Custom domain email for the entire team
  • ☑️ Seat management & RBAC
  • ☑️ 30GB storage per seat
  • ☑️ Team admin console
  • ✠DLP engine

Why Not Google or Microsoft?

  • ☑️ You own the keys
  • ☑️ No vendor lock-in risk
  • ☑️ DLP at $7 vs $18+ equivalent
  • ☑️ No shared relay infrastructure
SMALL & MEDIUM BUSINESSES 10–100 Employees

The Compliance Gap.
Closed at $12/seat.

SMBs face mounting regulatory obligations and data protection requirements but lack the IT headcount or budget for $20+/seat platform tiers.

Hansel delivers sovereign infrastructure, DLP pattern blocking, eDiscovery legal holds, and 365-day immutable audit trails at $12/seat/month. No bolt-on fees. No tier fragmentation. Just operational security that scales with your headcount, not your procurement budget.

🏗️

Sovereign Infrastructure

Your SMTP, your domain, your keys. No shared relay infrastructure or platform tenancy risk. Your communication layer belongs to you.

🛡️

DLP Pattern Blocking

Configurable patterns SSNs, credit cards, custom regex scanned on every outbound email before it leaves your perimeter. Block, flag, approve, or redact.

⚖️

eDiscovery Legal Holds

Keyword search across all org email, instant legal hold application, and export to PST/MBOX/JSON/CSV. Built in — no add-on required.

📦

365-Day Immutable Audit Trails

Every admin action, authentication event, DLP trigger, and email routing decision is logged with tamper-evident timestamps. Full year retention, always exportable.

vs. Enterprise Alternatives
Google Enterprise+ $30/user  Â·  Microsoft E3/E5 $22+/user  Â·  Hansel Business Professional $12/seat
40%
cheaper

"Operational security that scales with your headcount, not your procurement budget."

Business Professional
Per Seat / Month
$12
No bolt-on fees · No tier fragmentation
Included at this tier
☑️
Full DLP Engine
Pattern blocking · Block / Flag / Redact
☑️
eDiscovery + Legal Hold
Search · Hold · Export PST/MBOX/JSON
☑️
365-Day Immutable Audit Logs
Tamper-evident · Always exportable
☑️
Sovereign SMTP + Custom Domains
Your infrastructure · Device-bound keys
☑️
100 GB Per Seat
+ Org backup compliance monitoring
Comparable at this tier
Google Enterprise+ $30/user
Microsoft E3/E5 $22+/user
Hansel Business Pro $12/seat ☑️
hansel.smb compliance.engine
Live
Admin Command Console
Seat Provisioning
sarah@acme.com
Role: Dept Admin · Finance
Active
john@acme.com
Role: Standard User · Sales
Active
auditor@acme.com
Role: Read-Only Auditor
Audit
Custom Domain DNS
SPF ☑️ Verified
DKIM ☑️ Verified
DMARC ☑️ Enforced
Policy Enforcement
DLP Patterns Active 5 / 5
Backup Compliance 98%
2FA Enforced All Seats ☑️
hansel.admin · policy.console
Business Professional
CENTRALIZED ADMIN & POLICY CONTROL Business Professional

Complete Team Oversight.
Zero Admin Overhead.

Business Professional includes a unified command console for seat provisioning, custom domain DNS routing, and organization-wide policy enforcement. Administrators set baseline security rules, override permissions per department, monitor backup health across all seats, and enforce communication standards all without dedicated IT staff or third-party management portals.

🪪

Seat Provisioning

Assign, revoke, and manage every organizational seat from a single dashboard. No IT staff required — provision a new team member in seconds.

🚫

Custom Domain DNS Routing

Auto-generated SPF, DKIM, and DMARC records with real-time health monitoring. Know the verification status of every domain in your org at a glance.

🎛️

Org-Wide Policy Enforcement

Set baseline security rules across the entire organization and override permissions per department. Communication standards enforced architecturally —manually.

💾

Backup Health Across All Seats

Per-user backup compliance rates, last backup timestamps, and storage consumption — all monitored from a single admin view without third-party tooling.

No Dedicated IT Staff Required

Every admin control 🪪 seat provisioning, DNS routing, policy enforcement, backup compliance is operable by a non-technical founder or operations lead. No third-party management portals. No vendor support tickets.

1
console
everything

"Complete team oversight. Zero admin overhead."

COST PREDICTABILITY & SOVEREIGN ROUTING Business Professional

Predictable Scaling.
True Infrastructure Ownership.

Every seat unlocks sovereign SMTP routing, custom domain provisioning, end-to-end encrypted messaging, and centralized Stripe billing. As you add team members or departments, costs remain fixed per-seat with zero hidden platform tenancy fees. Your infrastructure scales linearlyyour operationa overhead stays flat.

📤
Per-Seat Entitlement

Sovereign SMTP Routing

Every seat activates dedicated sovereign SMTP routing and custom domain provisioning the moment it's assigned. No shared relay. No platform tenancy. Infrastructure ownership is baked into the per-seat cost —charged as an add-on.

☑️ Custom domain provisioning
☑️ SPF / DKIM / DMARC auto-generated
☑️ No shared relay infrastructure
🌐
Per-Seat Entitlement

End-to-End Encrypted Messaging

Wicked Crumbs protocol is activated across every seat. Device-bound keys, rotating cryptographic identifiers, and tamper-evident chains ensure your team's internal communications are architecturally private —reliant on platform promises or legal interpretations of "encryption."

☑️ Wicked Crumbs E2E on every seat
☑️ Device-bound keys — no server copies
☑️ Group messaging with hybrid encryption
📊
Zero Hidden Fees

Centralized Billing & Linear Scaling

Centralized Stripe billing gives finance complete visibility. As your team grows, cost scales linearly at the fixed per-seat rate with no hidden platform tenancy fees, no overage surprises, and no vendor-controlled pricing shifts. Operational overhead stays flat while infrastructure expands.

Cost per seat
$12 / seat / mo
Overhead as team grows
Flat
☑️ Centralized Stripe billing portal
☑️ No hidden platform tenancy fees
☑️ Infrastructure scales linearly
Sovereign Scaling Principle

"Your infrastructure scales linearlyyour operationa overhead stays flat."

Real-World Application Operational Security

Compliance Built Into
the Workflow.
Not Bolted On After.

For legal firms, consultancies, and financial operations handling confidential client data, Hansel replaces fragmented toolchains with a single sovereign layer.

DLP prevents accidental leaks, eDiscovery preserves records for regulatory review, and audit trails provide verifiable accountability. Move from reactive compliance to architectural control without enterprise procurement friction.

🛡️
DLP

Prevents accidental leaks before sensitive data leaves the org perimeter.

⚖️
eDiscovery

Preserves records for regulatory review with legal hold and structured export.

📦
Audit Trail

Verifiable accountability across every admin action, DLP event, and email operation.

"Move from reactive compliance to architectural control
without enterprise procurement friction."

STARTUPS & FOUNDING TEAMS The Early Infrastructure Decision

Build on Sovereign Ground.
Scale Without Debt.

Founding teams make infrastructure decisions with limited resources and tight deadlines. Once platform dependency takes root, migration breaks workflow and drains capital. Hansel gives early-stage teams sovereign email, crypto-verified messaging, and administrative controls from day one — so your foundation doesn't become a retrofit later.

🚀
Day 1
Sovereign from the start

Infrastructure sovereignty is vastly easier to build at founding than to retrofit after platform dependency has taken root across your team's workflows.

No Retrofit Required
The Platform Dependency Trap

The earliest infrastructure decisions
become the hardest to undo.

Startups default to Google Workspace or Microsoft 365 because they're familiar and fast to provision. But familiarity isn't sovereignty. The moment your team's email, messaging, and documents are routed through a third-party platform, that platform holds structural power over your most sensitive communications — investor conversations, cap table discussions, IP documentation, and competitive strategy.

Platform dependency compounds. Every new hire provisioned through Google is another thread in the dependency web. By Series A, migration is disruptive enough that most founders accept the risk as a permanent operating condition. Hansel removes the trap entirely by being the right decision from day one.

🚀
Account Suspension Risk

A single ToS flag can lock your entire founding team out overnight — no appeal window, no data access.

📉¸
Migration Costs Scale

At 10 people migration is feasible. At 50 it's a full project. At 200 it's a multi-quarter initiative that drains capital and focus.

"The earliest infrastructure decisions become the hardest to undo."

What Hansel Gives Founders

Sovereign email, crypto-verified messaging,
and admin controls from day one.

With Hansel, a two-person founding team gets the same sovereign infrastructure a 200-person organization would need — provisioned in minutes, priced for early stage. Custom domain email on sovereign SMTP, Wicked Crumbs encrypted messaging for sensitive conversations, and an admin console to manage seats as the team scales.

📬
Sovereign Email & Custom Domain

Ship outbound comms from you@yourcompany.com on infrastructure you control —Google's or Microsoft's shared relay.

🌐
Crypto-Verified Messaging

Wicked Crumbs protocol keeps founder conversations — investor updates, cap table discussions, IP strategy — device-bound and architecturally unreadable by any platform.

🛡️
Admin Controls That Scale With You

Provision new seats, manage domains, enforce policies, and monitor backup compliance — all from a single console that grows with your headcount.

💾
Encrypted Backup & Sovereign Reset

Serialized, Gzip-compressed, and encrypted snapshots of your entire communication history. Sovereign Reset gives you a clean architectural exit at any time.

Founding Team Stack
Sovereign Pro
Personal sovereignty layer
$4/mo
Business Essentials
Team + admin console
$7/seat
Business Professional
DLP + eDiscovery + Audit
$12/seat
Your tier grows as your team does
2 founders 50 employees Enterprise
🌱
0
Platform-Accessible Keys

Your encryption keys never leave your devices. Not even Hansel can read your messages.

Day 1
Sovereign by default

Not a feature unlocked later. Sovereignty is the architectural foundation —an upgrade path.

When Hansel Makes Sense

The earlier sovereignty becomes
part of the architecture,
the less disruptive it is.

Hansel is particularly relevant for startups that handle sensitive intellectual property, are actively raising capital, communicate with investors or strategic partners, work with confidential customer information, and want sovereign infrastructure before complexity takes over.

☑️ Handling sensitive IP or fundraising discussions
☑️ Communicating with investors or strategic partners
☑️ Building toward stronger compliance requirements
☑️ Wanting infrastructure that scales without migration debt
Start Sovereign Today
From Sovereign Pro at $4/mo to Business Essentials at $7/seat
No trial expiry. No lock-in. Upgrade as your team grows.
Get Hansel Free

"Your foundation shouldn't become a retrofit later."

SECURING IP, CAPITAL & STRATEGIC COMMS

Protect What Matters Most.
Architecturally.

Seed rounds, cap tables, product roadmaps, and investor communications require strict access boundaries. Wicked Crumbs ensures only authorized devices can decrypt sensitive discussions. QR-verified identity exchange prevents impersonation. Your most critical conversations stay isolated from platform telemetry and third-party tracking.

🌐
01
Encryption

Device-Bound Cryptographic Keys

Seed round documents, cap table discussions, and investor strategy sessions are encrypted on your device before leaving it. Only authorized recipient devices — holding the correct private keys — can ever decrypt the content. Hansel's infrastructure routes the message; it cannot read it. Platform telemetry captures nothing meaningful.

☑️ Wicked Crumbs device-bound keys
☑️ Zero platform access to plaintext
☑️ Tamper-evident forward-link chains
📱
02
Identity Verification

QR-Verified Identity Exchange

In high-stakes startup conversations — investor intros, co-founder agreements, legal counsel coordination — impersonation is an existential risk. Wicked Crumbs eliminates it architecturally. Contacts are established via cryptographic QR key exchange. No valid crumb chain, no message delivery. Impersonation is mathematically infeasible, not just policy-restricted.

☑️ QR cryptographic key exchange
☑️ No central directory or password
☑️ Impersonation architecturally impossible
🛡️
03
Data Isolation

Isolated from Platform Telemetry

Google and Microsoft infrastructure logs routing metadata, session patterns, and behavioral signals — even when message content is encrypted in transit. Hansel's rotating cryptographic identifiers continuously break correlation graphs. Third parties cannot reliably map who communicates with whom, how often, or from where. Your investor pipeline and strategic roadmap stay invisible to surveillance infrastructure.

☑️ Rotating identifier metadata blindness
☑️ No third-party tracking or telemetry
☑️ Communication pattern correlation broken
Sovereign from the First Conversation

"Seed rounds, cap tables, and investor communications require strict access boundaries. Wicked Crumbs ensures only authorized devices can decrypt — by design, not by policy."

Get Hansel
SECTION 3 — ADMINISTRATIVE BASELINES FOR EARLY TEAMS

Founder-Level Admin.
Enterprise-Grade Boundaries.

You don't need a full IT department to enforce security. Hansel's admin console lets founders set baseline policies, manage custom domains, provision seats as the team grows, and monitor backup compliance across all devices. Sovereignty scales with your hiring pipeline —your technical capacity.

Founder Admin Console
Baseline Policies
2FA Enforcement
All seats · Org-wide
Active
DLP Pattern Blocking
SSN · CC · Custom Regex
5 Rules
Backup Compliance
Weekly schedule · All devices
96%
Custom Domains
startup.com ☑️ Live
SPF / DKIM / DMARC ☑️ All Verified
Seat Growth
6 / 10 seats
4 seats available · +$12/seat to expand
Administrative Baselines Business Professional

Sovereignty scales with your
hiring pipeline —
not your technical capacity.

You don't need a full IT department to enforce security. Hansel's admin console gives founders the power to set org-wide baseline policies from day one — before your team has a dedicated ops person, before your first compliance audit, and before platform dependency turns into a structural liability.

Provision seats as you hire. Manage custom domains from the same console that auto-generates your SPF, DKIM, and DMARC records. Monitor backup compliance across every device in your organization. Set baseline 2FA enforcement that applies automatically to every new seat. The admin layer grows with your team without requiring you to scale your technical capacity alongside it.

🎛️

Baseline Policy Enforcement

Set 2FA requirements, session timeout rules, email retention windows, and DLP patterns at the org level. Every new seat inherits the baseline automatically.

🚫

Custom Domain Management

Register your startup's domain and provision team email addresses from the same console. Auto-generated SPF, DKIM, and DMARC records with real-time health monitoring — no DNS expertise required.

🪪

Seat Provisioning as You Hire

Add new team members in seconds. Each new seat inherits org-wide policy settings instantly — no manual configuration, no onboarding overhead, no IT ticket required.

💾

Backup Compliance Across All Devices

Monitor per-seat backup compliance rates, last backup timestamps, and storage consumption from a single admin view. Know exactly which devices are protected without chasing individuals.

"Sovereignty scales with your hiring pipeline —
not your technical capacity."

Available On
Business Professional — $12/seat/month
Full admin console + DLP + eDiscovery + 365-day audit logs + org backup compliance
Get Hansel
ENTERPRISE & REGULATED INDUSTRIES COMPLIANCE & SOVEREIGNTY

The Hidden Risk of
Platform Tenancy.

"Free commercial tiers and shared cloud suites operate under vendor terms that often contradict regulatory mandates — from GDPR territorial borders to student privacy acts. Relying on 'platform promises' instead of architectural sovereignty is a structural liability."

⚠️
Vulnerable State

Platform Promise

  • ☑️Vendor controls your keys
  • ☑️Foreign jurisdiction exposure
  • ☑️No data residency guarantee
  • ☑️Account suspension risk
migrate to
🏛️
Assess Risk

Infrastructure Audit

  • 📧Map data flows & borders
  • 📧Identify regulatory gaps
  • 📧Quantify liability exposure
  • 📧Evaluate vendor terms
deploy
VERIFIED
🎛️
Verified State

Sovereign Infrastructure

  • ☑️Device-bound cryptographic keys
  • ☑️Territorial data jurisdiction
  • ☑️Immutable compliance audit trail
  • ☑️Sovereign Reset — clean exit always

"This isn't about features. It's about infrastructure liability.
The question isn't whether your platform can be compelledit's whether yours can."

LARGE ENTERPRISES (1000+ Employees) The Coexistence Model

Sovereign Perimeters for
Your Most Critical Workflows.

You don't need to replace Microsoft or Google overnight. Hansel introduces a coexistence model: deploying sovereign infrastructure strictly around M&A teams, General Counsel, and R&D leadership. This creates an encrypted, isolated channel for market-moving conversations that runs parallel to — and completely independent of — your corporate cloud suites.

For a large enterprise, the near-term opportunity is not replacing Google or Microsoft across thousands of seats. It is protecting the conversations that could move markets, compromise acquisitions, or expose litigation strategy — starting today, without disruption.

Targeted Deployment Scenarios
⚖️
Legal

General Counsel & confidential litigation strategy

🤝
M&A

Deal-side negotiations & acquisition reviews

🏛️¬
R&D

Proprietary research & trade secret protection

🏢
Executive

Board-level strategy isolated from cloud admin reach

"Sovereignty begins where the risk is highest —
not where the migration is easiest."

COEXISTENCE ARCHITECTURE CORPORATE CLOUD SUITE (unchanged) 📬 Microsoft 365 General employees 📂 Google Workspace Collaboration & docs 💬 Slack / Teams Day-to-day comms SOVEREIGN PERIMETER HANSEL SOVEREIGN CHANNEL (isolated) 🤝 M&A Team ⚖️ General Counsel 🏛️¬ R&D Leadership 🌐 End-to-end encrypted · Device-bound keys Cryptographically isolated from corporate cloud EXISTING STACK SOVEREIGN LAYER
GOVERNMENT AGENCIES Jurisdictional Immunity

Eliminate Foreign
Jurisdiction Exposure.

"Your organization's data should never be subject to foreign intelligence access requests via the CLOUD Act. Hansel enables government bodies to deploy sovereign infrastructure on local servers within your own national borders, establishing jurisdictional immunity for public records, policy discussions, and citizen data."

01
The Problem

Jurisdictional Risk

Google and Microsoft are US companies subject to the CLOUD Act, which allows US authorities to compel access to data regardless of where it physically resides. For government agencies outside the US — and within it — foreign jurisdictional exposure is a disqualifying characteristic.

CLOUD Act Exposure
Foreign compulsion regardless of data location

When a government body's communications run through Google or Microsoft infrastructure, those communications become legally accessible to US authorities under CLOUD Act provisions — regardless of where the physical servers are located, and regardless of bilateral agreements.

For municipal, regional, and national government bodies handling citizen records, public policy discussions, and sensitive administrative communications, this is not a theoretical risk. It is an active operational vulnerability that contradicts legal data sovereignty mandates in most jurisdictions.

CLOUD Act Compulsion Foreign Intelligence Risk Extraterritorial Warrants

Hansel resolves this by enabling government agencies to deploy their own communication infrastructure on servers physically located inside their own jurisdiction running Hansel's encrypted protocol and administrative tooling under direct institutional control.

The infrastructure belongs to the government body. No US company holds the keys. No foreign court order can reach what a foreign company does not possess. Communications governed by local law —vendor terms and conditions.

On-Premises Deployment National Border Data Residency Institutional Key Ownership
02
The Solution

Local Server Deployment

☑️

Servers within national borders

☑️

Hansel protocol & tooling on your hardware

☑️

No foreign entity holds keys or data

03
The Result

Total Territorial Control

100%
Jurisdictional Immunity

No foreign authority can compel access to infrastructure your government physically owns and operates.

The result is complete territorial control. Public records, policy discussions, and citizen data are governed exclusively by the laws and institutions of the jurisdiction in which they reside —by the corporate terms of a foreign technology vendor.

Every administrative action is logged in an immutable, tamper-evident audit trail. eDiscovery tools enable public records requests without third-party platform delays. The government body is, for the first time, the actual owner of its own communication infrastructure.

eDiscovery
Native public records request processing
365-Day
Immutable audit retention built-in

"Public records under the sole authority
of the people they serve."

Education Institutions Institutional Stewardship

Protecting Academic
Discourse and
Student Trust.

"Student records and faculty correspondence are under increasing scrutiny. Instead of relying on free commercial platforms with opaque data practices, establish genuine sovereignty over your institution's intellectual property and staff communications — fulfilling strict data privacy mandates from the ground up."

Free offerings from Google and Microsoft dominate education because they're convenient. But their centralized infrastructure creates persistent data sovereignty questions that regulators are increasingly scrutinizing. Platform terms are not architected around sovereign student data protection. Hansel is.

🎓
FERPA

Student records privacy — US education institutions

🧒
COPPA

Children's online privacy — under-13 data protection

🇪🇺
GDPR

EU data sovereignty — territorial residency mandates

🌐
SOVEREIGN

Institutional infrastructure ownership — guaranteed exit

"School communications and student records
should never be treated as commoditized platform data."

UNIFIED TECHNICAL CAPABILITY Business Professional

Forensic-Ready Compliance,
Built into the Workflow.

Across all three sectors — large enterprises, government agencies, and educational institutions — Hansel delivers a unified command center for verification and regulatory compliance.

🏛️
eDiscovery

Search & Export

Process public records requests and legal holds natively. Full-text and pattern search across all organizational email and messaging history. Export results in JSON or CSV format for legal counsel or regulatory submission — with complete chain-of-custody logging for every action.

JSON CSV PST MBOX Legal Hold
📦
Audit Trails

365-Day Immutable Retention

Tamper-evident visibility into every admin action and data handoff. Authentication events, email activity, DLP triggers, eDiscovery searches, legal hold applications — every significant action is logged with precise timestamps. Immutable: no user or admin can alter or delete records.

Retention Period
365 Days
Tamper-Evident
🛡️
DLP Enforcement

Architectural Pattern Blocking

Prevent accidental leakage of sensitive IP or citizen data before it ever leaves your organization. Configurable patterns SSNs, health identifiers, API keys, custom regex scanned on every outbound email. Policy actions: Block, Flag, Approve, or Redact. Every trigger generates an immutable compliance record.

Block Transmission ☑️
Auto-Redact Content ☑️
Custom Regex Patterns ☑️
Unified Across All Three Sectors

"Whether you're a multinational enterprise protecting M&A conversations, a government agency processing public records requests, or a university fulfilling FERPA obligations the same forensic-grade compliance toolkit is available at a single tier."

STRATEGIC CLOSING Regulated Growth

Build a Compliant Infrastructure
That Outlasts Platform Trends.

"For enterprises, government bodies, and institutions, sovereignty isn't a featureit's the baseline requirement for operational longevity. Establish your sovereign communication layer today on a stack designed for regulatory adherence and absolute control."

🏛️ eDiscovery + Legal Hold
📦 365-Day Audit Trails
🛡️ DLP Pattern Blocking
🌐 Sovereign Key Ownership
Business Professional
$12
per seat / month
No bolt-on fees · No tier fragmentation
All compliance tools included at this tier
Download Admin Brief

Part of the Seedling ecosystem Let's Grow Together.

SECURITY & COMPLIANCE

Infrastructure Ownership
vs. Platform Dependency.

The difference isn't a featureit's a fundamental architectural choice that determines whether you control your communication or merely rent access to it.

Origin

The Origin Story

Hansel was founded after a real organization was locked out of their Google Workspace account overnight. No warning, no appeal window, no data access. Every email, every file, every communication - inaccessible. This is the vendor lock-in trap. Hansel was architected so this can never happen to you.

Own the Infrastructure

Your SMTP, your relay, your servers not shared Google infrastructure.

Own the Keys

Device-bound cryptographic keys. Hansel never sees plaintext.

Own the Exit

Sovereign Reset: local wipe, server cleanup, factory-fresh state.

Warning

The Vendor Lock-In Anatomy

When you use Google Workspace or Microsoft 365, they control your encryption keys, your data residency, your account access, and your compliance evidence. A Terms of Service violation — real or automated — and your organization loses everything, with no recourse. This is by design, not accident.

Platform Dependency Risks

  • ☑️ Account suspension without appeal
  • ☑️ Keys held by vendor
  • ☑️ Data residency not guaranteed
  • ☑️ Compliance tools locked to highest tiers
  • ☑️ No exit without data loss risk
PROTOCOL INDEPENDENCE POLICY RESILIENCE

Architecture That Doesn't Blink
When Platforms Change.

Commercial cloud suites operate on centralized control. They update APIs, throttle deliverability, shift pricing models, or sunset features without warning. Sovereign infrastructure breaks this dependency chain by design.

🔗
01 — Platform Volatility

API updates, pricing model shifts, feature sunsets without warning, without consent.

🔗
02 — Vendor Roadmap Dependency

Your operational continuity becomes hostage to their product decisions and release cadence.

🎛️
03 — Sovereign Determinism

Your stack runs on open standards. You control the deployment cadence. No consent required.

Sovereign infrastructure breaks the dependency chain by design. Your communication stack runs on deterministic, open standards — SMTP routing, Wicked Crumbs cryptographic exchange, local-first serialization — that don't require consent from a third-party vendor to function.

When market volatility hits, policies fracture, or platform roadmaps drift, your infrastructure operates deterministically. You don't adapt to their updates — you control your own deployment cadence.

📤
SMTP Routing

Open standard. No vendor permission required to route your email.

🌐
Wicked Crumbs

Proprietary cryptographic exchange. Device-bound. Platform-independent.

💾
Local-First

Serialized, encrypted, restorable on demand. You hold the keys.

"You don't adapt to their updates —
you control your own deployment cadence."

SOVEREIGN STACK — DETERMINISTIC PLATFORM VOLATILITY API changes · pricing shifts · feature sunsets policy fractures · vendor roadmap drift SOVEREIGN SHIELD YOUR INFRASTRUCTURE — DETERMINISTIC 📤 SMTP WICKED CRUMBS 💾 LOCAL-FIRST YOU CONTROL THE DEPLOYMENT CADENCE Open standards · No vendor consent required OPERATIONAL CONTINUITY Regardless of market volatility · policy fracture · roadmap drift HANSEL · SOVEREIGN ARCHITECTURE
The Real Cost Shared Tenancy

The Invisible Debt of
Shared Infrastructure.

Platform dependency is rarely just about the monthly subscription. It's about feature fragmentation, data gravity, and integration debt. Third-party suites force you through a vendor's routing logic, unified UI layers, and bundled feature sets that prioritize their ecosystem over your operational needs.

Sovereign infrastructure eliminates this gravity model. Every component — custom domain provisioning, cryptographic identity, backup serialization, and DLP enforcement — operates independently under your governance. This clears hidden TCO: no forced bundle upgrades, no feature rot as vendor priorities shift, and zero exit friction when your organization outgrows the platform's designed perimeter.

True ownership compounds; shared tenancy depreciates.

🚫
No Forced Upgrades

Features you need don't disappear behind a higher tier you didn't budget for.

🛡️
No Feature Rot

Vendor priority shifts don't erode the capabilities your operations depend on.

0
Zero Exit Friction

Sovereign Reset gives you a clean architectural exit — always, on your terms.

"True ownership compounds;
shared tenancy depreciates."

Technical Sovereignty Matrix

Architectural Layer Legacy Cloud
(Google / Microsoft)
Zero-Knowledge Cloud
(Proton)
Open Cloud
(Fastmail)
Hansel
(Seedling.io)
Cryptography & Key Custody Server-side management. Provider generates, holds, and rotates keys; content is accessible to internal automated systems for indexing. Client-side PGP. Keys generated in-browser/app. Encrypted key blobs are backed up to centralized remote servers. Transport/Rest Encryption. Standard server-controlled data keys. No built-in client-side zero-knowledge framework. Local-First Asymmetric. Keys are generated and stored exclusively on local physical hardware. Zero remote backup footprint or external exposure.
DLP & Auditing Enterprise Tier Add-on. Complete compliance logging, dictionary matching, and eDiscovery via expensive corporate custom licensing. Highly Restricted. Zero-knowledge architecture natively conflicts with standard server-side deep content inspection and global compliance filtering. Basic Rules Engine. Standard sieve filtering, custom headers, and retention controls, but lacks native behavior-based corporate policy triggers. Local Deterministic DLP. Local pattern-matching engines process streaming content natively on-device before sync queues. Ingests without central leaks at <$12/seat.
Identity & Control Centralized Provider. Profile is tied directly to vendor identity systems. The platform reserves administrative rights to suspend or terminate access. Centralized Identity. While data is encrypted, account authentication depends on hosted identity clusters. Subject to remote vendor lockouts. Centralized Independent. Private infrastructure provider. Full customer service path for account recovery, but access remains vendor-dependent. Sovereign Instance. System operates as an isolated node. No parent organization or central identity registry possesses a remote kill switch or exit block.
Mail Transport (SMTP) Proprietary Relays. Outbound/Inbound traffic travels exclusively through massive centralized IP pools with built-in metadata profiling. Central Private Relays. Fully hosted infrastructure routed through secure, private network pipelines controlled by a single company. Open Protocol Clusters. Standard cloud-hosted MX infrastructure utilizing modern open extensions (JMAP, IMAP). Sovereign Local Relay. Operates containerized local SMTP configurations. Integrates direct P2P validation vectors to isolate outbound transport.
Spam Mitigation Heuristic / AI Scanning. Massive centralized ML models ingest and parse global inbound message bodies to calculate probability scores. Content-Blind Filters. Relies heavily on network reputation, IP blocklists, and user-defined sender/domain logic due to encrypted bodies. Heuristic Bayesian Engine. Standard collaborative cloud spam networks analyzing message header properties and known bad attachment fingerprints. Cryptographic Verification. Rejects untrusted incoming network requests at the perimeter connection layer unless signed by authorized validation keys.
DLP & LEGAL CONTROLS

Data Loss Prevention
& Legal Controls.

Pattern-based DLP, legal hold, eDiscovery export, message tracing forensics, and 365-day immutable audit logs built into Business Professional.

DLP Pattern Library & Policy Actions

Define custom patterns or use the pre-built library: SSN, credit card numbers, IBAN, API keys, health identifiers (PHI). Each pattern maps to a policy action: Block transmission, Flag for review, Auto-approve with logging, or Redact before delivery.

DLP
eDiscovery

eDiscovery Search, Hold & Export

Full-text and pattern search across email and messaging history. Apply legal holds instantly content is preserved immutably. Export packages support PST (Outlook-compatible), MBOX (universal), JSON (structured), and CSV (tabular) formats for legal counsel and compliance submissions.

DLP PATTERN LIBRARY Business Professional

Precision Rule Matching with
Configurable Policy Execution

Every outbound message is evaluated against a layered rule engine before transmission. Administrators deploy five pre-configured recognition patterns (credit card numbers, Social Security numbers, API keys/credentials, plaintext passwords, phone numbers) or define unlimited custom regex rules tailored to organizational identifiers.

Each pattern triggers a strictly configurable policy action. Every action captures sender identity, matched pattern type, timestamp, and routing context into the immutable audit log. DLP rules operate deterministically against traffic at the SMTP relay layer reactive post-hoc audits.

🚫

Block

The message is withheld from sending at the client endpoint. The sender receives a contextual prompt explaining the violation, and the event is logged with full metadata.

🚩

Flag

The message routes normally but generates a compliance alert for administrator review, preserving workflow continuity while capturing risk exposure.

Pre-Configured Pattern Library
💳 Credit Card Numbers 🏛️¢ Social Security Numbers 🔒 API Keys / Credentials 🌐 Plaintext Passwords 📞 Phone Numbers ✏️ Unlimited Custom Regex

"DLP rules operate deterministically against traffic at the SMTP relay layer —
not as reactive post-hoc audits."

HanselDLPScreenshot
Active Pattern Rules
SSN Pattern BLOCK
Credit Card BLOCK
API Key FLAG
Custom Regex #1 FLAG
eDISCOVERY CHAIN-OF-CUSTODY EXPORT Business Professional

eDiscovery Search Scope &
Chain-of-Custody Export

Targeted Historical Retrieval with Preserved Legal Integrity

When compliance or litigation requires structured record production, the eDiscovery engine executes cross-mailbox searches across the entire organization. Admins filter by sender, recipient, subject keywords, date ranges, and attachment metadata to isolate relevant correspondence.

Targeted mailboxes can be placed under legal hold, freezing both existing and newly received messages from deletion until explicitly released. Retrieved records export natively in PST, MBOX, JSON, or CSV formats, preserving original message headers, thread mappings, and cryptographic crumb chain verification markers.

Every search query, hold creation/modification, and export action is logged with tamper-evident timestamps to establish court-admissible chain of custody. Compliance tools operate as architecturally enforced layers bolt-on third-party connectors.

🏛️
Search Scope

Cross-Mailbox Search

Execute cross-mailbox searches across the entire organization. Filter by sender, recipient, subject keywords, date ranges, and attachment metadata to isolate relevant correspondence with precision.

Sender Recipient Keywords Date Range Attachments
🔒
Legal Hold State

Immutable Hold Management

Place targeted mailboxes under legal hold, freezing both existing and newly received messages from deletion until explicitly released. Hold status is invisible to the end user — preventing tampering while preserving legal integrity.

Hold Status
Admin-Only
Invisible to User
📦
Chain-of-Custody Export

Court-Admissible Record Production

Export in PST, MBOX, JSON, or CSV preserving original headers, thread mappings, and cryptographic crumb chain verification markers. Every action logged with tamper-evident timestamps.

PST MBOX JSON CSV

"Compliance tools operate as architecturally enforced layers bolt-on third-party connectors."

Hansel | Sovereign Communication Infrastructure
Hansel

Communication Infrastructure
You Actually Own.

End-to-end encryption, DLP, eDiscovery, and full admin control without platform dependency or enterprise markup.

Get Hansel Free
Scroll
THE SOVEREIGNTY PROBLEM

Your Organization's Communication
Doesn't Belong to You.

When your organization runs on Google Workspace or Microsoft 365, you're not the owner — you're a tenant. Your encryption keys live on their servers. Your compliance data flows through their infrastructure. One account suspension and you lose everything overnight.

Hansel was built after exactly that happened. A real organization — locked out of Google overnight. No warning. No appeal window. No data access. That's the vendor lock-in trap. Hansel is the exit.

Hansel Workspace
🔑

Wicked Crumbs

E2E encrypted messaging with rotating cryptographic identifiers every 15 minutes. Device-bound keys. Tamper-evident chains.

Explore Protocol 📧
📬

Sovereign Email

Your SMTP. Your domain. Intelligent auto-sorting. Encrypted serialization. Full organizational ownership of every message.

Explore Email 📧
🛡️

Admin Controls

RBAC seat management, DLP, eDiscovery, 365-day immutable audit logs, and real-time org health monitoring.
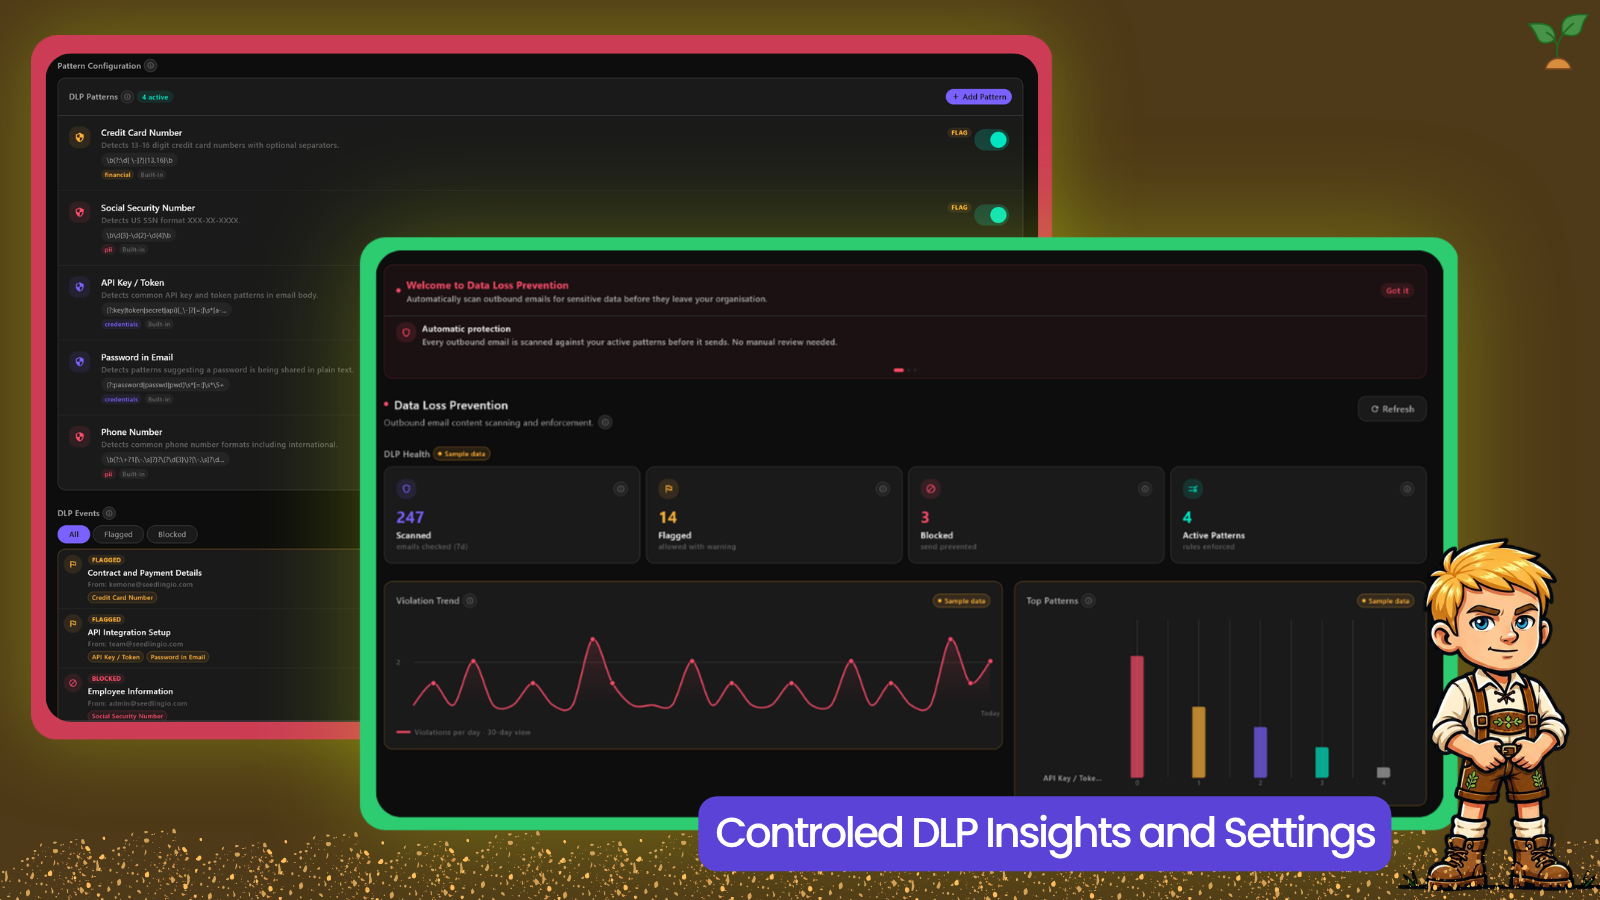
Explore Admin 📧
Hansel Welcome
Inbox Experience
Admin Console
Admin Console
DLP
DLP Engine
Backups
Backup System
SOVEREIGN POWERHOUSE

Infrastructure you actually own.
Security that never asks for permission.

🧬

Wicked Crumbs Protocol

Industry-leading encryption where keys are generated and stored only on your device. Your communication history is yours to encrypt, back up, or restore at any time.

📬

Sovereign Email Routing

Manage your own SMTP infrastructure, organize mail with intelligent algorithms, and support multiple custom domains—all without relying on a third-party relay.

🏢

Enterprise-First Design

From RBAC to message tracing and automated policy enforcement, the tools regulated industries need are built directly into your dashboard on day one.

🔒

Uncompromised Encryption

Messages that stay between you and your devices. Rotating cryptographic identities and forward-link integrity checks keep data off the server entirely.

📊

Admin-Driven Control

Real-time security intelligence, instant audit export, and complete infrastructure visibility. Compliance tools architecturally enforced, not bolted on.

🏗️

True Infrastructure Ownership

Own your email standards and your user data. No platform dependency means no sudden policy changes, pricing hikes, or locked-out accounts.

Communication infrastructure built to replace what you rent with what you own.
The sovereign communication layer for modern organizations.

PRICING & PLANS

Choose Your Level of Control.

From personal sovereignty to enterprise compliance. No lock-in. You own everything.

🌐
Sovereign
Free
Forever yours
  • ☑️Personal email (1 domain)
  • ☑️Wicked Crumbs messaging
  • ☑️Local device storage
  • ☑️Device-bound keys
  • ☑️Sovereign Reset
  • ☑️Cloud storage
  • ☑️DLP / eDiscovery
  • ☑️Admin dashboard
Get Started Free
🚫
Sovereign Connected
Free
+ Group messaging
  • ☑️Everything in Sovereign
  • ☑️Wicked Crumbs group messaging
  • ☑️1 connected integration
  • ☑️Priority message delivery
  • ☑️Custom domain email
  • ☑️Cloud backup storage
  • ☑️DLP / eDiscovery
Get Started Free
Most Popular
⭐
Sovereign Pro
$4/mo
Per user, billed monthly
  • ☑️Everything in Connected
  • ☑️Custom domain email
  • ☑️15 GB cloud storage
  • ☑️Unlimited integrations
  • ☑️Encrypted backup & restore
  • ☑️Priority support
  • ☑️Admin dashboard
  • ☑️DLP / eDiscovery
Start Pro
🏢
Business Essentials
$7/seat/mo
For growing teams
  • ☑️Everything in Pro
  • ☑️Custom domain email for team
  • ☑️Seat management & RBAC
  • ☑️30 GB per seat storage
  • ☑️Team admin console
  • ☑️DLP engine
  • ☑️eDiscovery & legal hold
  • ☑️365-day audit logs
Start Essentials
⚔️
Business Professional
$12/seat/mo
Full enterprise flagship
  • ☑️Everything in Essentials
  • ☑️Full DLP & eDiscovery
  • ☑️100 GB per seat storage
  • ☑️365-day immutable audit logs
  • ☑️Legal hold & export (PST/MBOX)
  • ☑️Org backup compliance
  • ☑️Message tracing forensics
  • ☑️Security intelligence dashboard
Book a Call

All plans billed monthly as shown — discounted yearly options available.

All prices in $USD.

ONE STACK

One Stack. Sovereign at Any Scale.

What's Shipping

ANSWERS

Find the Answers
that you need.

Everything you need to know about Hansel's features, pricing, encryption, and sovereignty principles.

"Sovereign" means you own and control the infrastructure your communications run on —a third-party vendor. When you use Google Workspace or Microsoft 365, those platforms hold your encryption keys, control your data residency, and can revoke your access without warning. Hansel was literally built after a real organization was locked out of Google overnight. Sovereign communication means your SMTP is yours, your encryption keys never leave your device, and you have a Sovereign Reset option that gives you a clean exit at any time.

Wicked Crumbs is Seedling's proprietary cryptographic protocol. Your encryption keys are generated and stored exclusively on your device — Hansel's servers never see your plaintext. Every 15 minutes, your cryptographic identifier rotates, making long-term surveillance correlation computationally infeasible. Messages are chained with tamper-evident hashes, so any alteration to historical messages is detectable client-side. Identity verification happens through QR code exchange, eliminating impersonation at the protocol level.

iOS and Android clients are currently shipping — this is Hansel's highest-priority platform expansion right now. Hansel's core services, including the Wicked Crumbs protocol, Lambda services, and email infrastructure, are platform-agnostic, meaning the underlying sovereign infrastructure does not change when the client runs on a mobile device. The mobile apps will bring the full Hansel messaging and email experience to the devices you carry every day.

DLP (Data Loss Prevention) scans every outbound email for sensitive information — credit card numbers, SSNs, API keys, PHI — before it ever leaves your organization. If a pattern is detected, the system can block the email, flag it for review, require approval, or auto-redact the sensitive content. If your organization handles any sensitive client, financial, or healthcare data, DLP is not optional. Hansel includes it in Business Essentials at $7/seat — Google and Microsoft require $20–30/user enterprise tiers for equivalent functionality.

Yes — custom domain email is available starting from Sovereign Pro at $4/month. You bring your domain (e.g., me@mybusiness.com) and Hansel provisions the sovereign SMTP infrastructure behind it. The admin console auto-generates your SPF, DKIM, and DMARC DNS records with clear setup instructions, and your domain health is monitored in real time. For teams, Business Essentials and Professional allow you to provision custom domain email addresses for every seat across your entire organization from a single admin console.

Business Essentials ($7/seat/mo) covers custom domain email, seat management, RBAC, a team admin console, 30GB per seat, and the DLP engine — ideal for growing teams that need organizational email controls without deep compliance requirements. Business Professional ($12/seat/mo) adds the full compliance stack on top: eDiscovery with legal hold and export (PST/MBOX/JSON/CSV), 365-day immutable audit logs, message tracing forensics, org-wide backup compliance monitoring, and 100GB per seat. If your organization operates in a regulated industry — legal, healthcare, finance — Professional is the tier designed for you.

Your data is yours — always. Cancelling a Hansel subscription does not mean the platform becomes the owner of your data. You retain full access to export your data before cancellation. If you want a completely clean break, Sovereign Reset allows you to wipe your local profile, trigger server-side cleanup, and return to a factory-fresh state with no residual data or orphaned records. This is a fundamental design principle of Hansel: platform dependency should never trap your data.

Hansel is built for everyone. The reason it can serve such a broad range — individual professionals, startups, and regulated enterprises is that sovereignty is not a company-size problem. A journalist protecting a source, a founder protecting an acquisition discussion, a law firm managing sensitive client communications, and a multinational corporation managing cross-regional infrastructure all share the same underlying need: control the infrastructure your communications depend on. The Sovereign free tier starts at $0, forever, with no expiration.

Hansel's backup system serializes your complete communication state — all email threads, messages, attachments, folder structure, and read/unread status — into an encrypted, Gzip-compressed snapshot. Every backup is timestamped, allowing you to restore to any prior state. Business Professional adds scheduled automatic backups (daily, weekly, or custom cadence) that run silently in the background, plus an org-wide admin dashboard showing per-user backup compliance rates, last backup timestamps, and storage consumption across the entire organization.

Still have questions about pricing specifically?

Own Your Communication Stack.

From personal sovereignty to enterprise compliance. Free forever on the base tier.
Get Hansel Free
PRODUCT — SOVEREIGN EMAIL

Your Email.
Your Infrastructure.

Custom domains, sovereign SMTP, intelligent auto-sorting, and encrypted serialization. No third-party relay. No vendor lock-in. Every message belongs to you.

Sovereign SMTP Architecture

Hansel provisions your own SMTP infrastructure — no shared relays, no dependency on Google or Microsoft. Your domain's SPF, DKIM, and DMARC records are auto-generated and managed from your admin console. Messages never pass through infrastructure you don't control.

  • ☑️ Custom domain provisioning with DNS record auto-generation
  • ☑️ SPF / DKIM / DMARC managed from admin console
  • ☑️ No shared relay infrastructure
  • ☑️ Intelligent auto-sorting: Inbox, Unknown Senders, No Reply, Notifications, Spam
  • ☑️ Encrypted serialization Gzip + encryption at rest
  • 🗓️ Hansel-to-Hansel E2E email encryption Building Next
Hansel Welcome
💾

Backup Serialization

All email data serialized to encrypted snapshots with timestamped restore points.

📜

Gzip Compression

Efficient Gzip compression before encryption reduces storage footprint without sacrificing security.

🔄

Sovereign Reset

Local wipe, server cleanup, factory-fresh state. No residual data, ever.

MORE TOOLS

More Tools to Help You
Scale Your Business

Infrastructure that keeps your operations running smoothly, securely, and on your terms.

SECURITY POSTURE

Stay Secure with Infrastructure
You Actually Own

Cryptographic boundaries, zero-knowledge encryption, and administrative controls built to outlast platform dependency.

0
Platform-Accessible Keys

Private cryptographic keys are generated and stored exclusively on your device. The infrastructure operator has zero mathematical ability to access, read, or decrypt message content or email history regardless of external requests or policy shifts.

365-Day
Immutable Audit Retention
Business Professional

Every administrative, authentication, and routing event is logged with tamper-evident timestamps. Full 12-month retention ensures legal hold readiness, compliance reporting, and forensic visibility—without archival gaps or vendor lock-in risks.

100%
Infrastructure Ownership

Your SMTP routing, custom domains, and serialized data live under full organizational control. No platform tenancy means forced feature rollouts, pricing overrides, or account dependency never apply to your stack.

Rooted in Wicked Crumbs boundaries and sovereign architecture

PLANS

Choose the plan that's
right for you

Start Free
Sovereign & Sovereign Connected
$0 / forever
Storage
Local-first storage
Zero platform lock-in
Security
Wicked Crumbs keyless encryption
By default, on every tier
Visibility & Support
Full GitBook docs & GitHub release access
Everything you need to get started
Next-Gen Capabilities
QR identity exchange & rotating identifiers
Cryptographic privacy at the protocol level
Recommended
Business SKU
Business Essentials
$7 / seat / mo
Storage
30 GB per seat
Shared org pool, auto-scaled
Team Provisioning
Seat management, unified admin dashboard
Cross-domain routing included
Compliance
DLP patterns, eDiscovery search & legal hold
+ 365-day immutable audit trail retention
Admin Health Snapshots
Per-user backup compliance tracking
Priority routing channel included
Message Tracing Forensics
Sovereign contact sync & device management
Roadmap

* Business Essentials includes all free-tier capabilities scaled for team deployment. Storage pools across seats per organization. Compliance & forensic tooling upgrade automatically to Business Professional ($12/seat) when DLP or legal hold requirements scale.

FAQS

Curious about
Sovereign Email?

Take a look at our FAQs to learn more.

Sovereign email means you own and operate the infrastructure your email runs on. Instead of routing messages through Google's or Microsoft's shared servers, Hansel provisions a dedicated SMTP infrastructure behind your own custom domain. Your DNS records (SPF, DKIM, DMARC) are auto-generated from your admin console. Your messages never pass through infrastructure you don't control — and you can take your data and exit at any time using Sovereign Reset.

Yes. Custom domain email is available on Sovereign Pro ($4/month) and all Business tiers. You bring your domain — for example, you@yourbusiness.com — and Hansel provisions the sovereign SMTP infrastructure behind it. The admin console auto-generates the exact SPF, DKIM, and DMARC DNS records you need, with clear setup instructions. Domain health is monitored in real time so you always know its verification status. For teams, Business Essentials and Professional allow you to provision custom domain addresses for every seat across your entire organization from a single admin console.

Hansel uses an intelligent algorithmic routing engine to automatically classify and sort all incoming messages into purpose-built folders: Inbox (verified contacts), Unknown Senders (quarantined until you approve), No Reply (automated transactional emails such as receipts and confirmations), Notifications (platform alerts from apps and services), and Spam (algorithmic junk filtering). This means unknown senders cannot reach your attention by default — you control who has access to your inbox, not an algorithm owned by a third party.

Hansel's backup system serializes your complete email state — all threads, messages, attachments, folder structure, and read/unread markers — into a single encrypted snapshot. Before storage, data goes through a serialization 📧 Gzip compression 📧 encryption pipeline. Every backup is timestamped so you can restore to any prior state. Business Professional adds scheduled automatic backups (daily, weekly, or custom cadence) that run silently in the background, plus an org-wide admin view showing per-user backup compliance rates and storage consumption.

Yes — Hansel-to-Hansel email encryption is actively Building Next. When both the sender and recipient are Hansel users, Hansel will encrypt the outbound email content using the recipient's Wicked Crumbs public key before the message is transmitted via SMTP. The message still travels across standard email infrastructure, but instead of readable content, the email carries an encrypted payload that only the recipient's private key — held exclusively on their device — can decrypt. Standard email infrastructure. Sovereign message content.

Sovereign Reset is a complete exit mechanism built into Hansel. It wipes your local profile data, triggers a server-side cleanup of all associated records, and returns your device to a factory-fresh Hansel state — no residual data, no orphaned records. You'd use it if you're leaving Hansel entirely and want a clean break, or if you need to reprovision your identity from scratch. This is a core design principle: platform dependency should never trap your data. You own your data, and you have a clean, architecturally-enforced way to take it back.

Ready to Own Your Email?

Get Hansel 📧
Wicked Crumbs

The Wicked Crumbs Protocol

End-to-end encrypted messaging with rotating cryptographic identifiers, device-bound keys, and tamper-evident chains.

Cryptographic Message Flow

Device-Bound Keys & Rotating Identifiers

Every 15 minutes, Wicked Crumbs rotates your cryptographic identifier. This prevents long-term correlation of your messages even if traffic analysis is attempted. Your keys are generated and stored exclusively on your device — Hansel infrastructure never sees plaintext.

  • ☑️ Random timed cryptographic ID rotation
  • ☑️ Device-bound key pairs — no server-side keys
  • ☑️ Tamper-evident crumb chains with forward-link integrity
  • ☑️ QR code identity verification
  • ☑️ Impersonation prevention via cryptographic UID
Identity

Cryptographic Identity

QR code verification pairs your identity to your device keypair. No phone number required.

🔗

Tamper-Evident Chains

Every message references the previous hash. Any tampering breaks the chain — detectable immediately.

💥

Group Messaging Shipping Now

Hybrid encryption with device-held group key state. Scales to teams without compromising E2E security.

Wicked Crumbs vs Signal Protocol

Feature Wicked Crumbs Signal Protocol
SHIPPING NOW 🚀 Group Messaging

The Group Key
Model

Traditional encrypted groups often bottleneck on server-side key management or force platforms to hold master keys for every conversation. Wicked Crumbs flips this: each participant's device maintains the current cryptographic state.

Using a hybrid encryption model, messages are efficiently distributed without requiring identical heavy cryptographic operations for every member. This architecture scales mathematically — no artificial group caps, no performance degradation as membership grows, and zero reliance on a central authority to manage group trust.

🔒
Device-Held State

Each member's device independently maintains the current group key state. No central authority required.

🔗
Hybrid Encryption

Efficient key distribution without per-member heavy cryptographic operations on every message.

📊
Mathematical Scaling

No artificial group caps. No performance degradation as membership grows. Scales by design.

🛡️
Zero Central Trust

No server holds master keys. No platform authority over group trust. Privacy by architecture.

🌐
Group Key
State
📱
Device A
💻
Device B
🖥️
Device C
📲
Device D

Decentralized Key State Propagation

CRYPTOGRAPHIC IDENTITY

Cryptographic Identity &
The QR Verification Layer

Email addresses and passwords are easily spoofed, harvested, or reused. Wicked Crumbs replaces credential-based trust with mathematical proof of identity.

🔒

Identity Through Math, Not Policy

Users establish contact by exchanging cryptographic public keys via QR scan in-person or through trusted networks. This creates a verifiable, tamper-proof connection graph.

Impersonation isn't just blockedit's architecturally impossible. The recipient's device validates the sender's crumb chain against their locally stored key pair before rendering anything.

No credential. No password. Pure cryptography.
01

QR Code Key Exchange

Each user's Hansel identity is anchored to a cryptographic key pair generated on their device. Connecting with someone means exchanging public keys via QR scan — in person or through a trusted digital channel. No central directory. No server-mediated introduction.

02

Tamper-Proof Connection Graph

Once keys are exchanged, a verifiable connection is established. Every subsequent message is cryptographically signed against the stored public key. The connection graph cannot be spoofed retroactively — altering any link in the chain breaks the mathematical proof instantly.

03

Device-Side Validation Before Render

Your device validates the sender's crumb chain against the locally stored key pair before rendering a single message. Nothing reaches your screen without passing cryptographic proof of sender identity. The platform has no role in this — it happens locally, every time.

04

Impersonation is Architecturally Impossible

Without possession of the sender's private key — held exclusively on their device — it is mathematically infeasible to forge a valid crumb chain. There is no credential to steal, no password to reset, and no account recovery flow that can be social-engineered. Identity is proof, not policy.

0
Central Identity Servers

No directory service, no username database, no account recovery server. Identity is established peer-to-peer via cryptographic key exchange.

QR
Scan-to-Trust Protocol

A single QR scan exchanges cryptographic public keys and establishes a verified, tamper-proof identity link between two devices.

♾️
Infeasible to Forge

Without the private key on the sender's device, no valid crumb chain can be constructed. Mathematical infeasibility is the enforcement mechanism —policy, not moderation.

Metadata Blindness Surveillance Resistance

Metadata
Blindness &
Surveillance Resistance.

Even when message content is encrypted, metadata can map entire communication networks. Wicked Crumbs neutralizes this by continuously rotating encrypted identifier paths. Your outbound routing signatures shift on a fixed cycle, breaking traditional call-graph analysis and contact-harvesting models.

Third parties cannot reliably track who communicates with whom, because the metadata itself is cryptographically blinded and non-persistent. Surveillance at scale requires predictable paths. Hansel removes them.

🔄
Rotating Paths

Identifier rotation breaks call-graph correlation across sessions.

🕶️
Blind Metadata

Routing signatures are cryptographically blinded and non-persistent.

🚫
No Predictable Path

Mass surveillance requires consistent routing. Wicked Crumbs denies it.

"Surveillance at scale requires predictable paths.
Hansel removes them."

🏛️¨ Building Next CRYPTOGRAPHY ROADMAP

Forward-Looking
Cryptography

Long-lived encryption keys create a historical vulnerability: compromise of one key can expose past communications. Hansel's next cryptographic evolution introduces per-message key derivation.

Every exchange will generate a session-specific key that expires immediately after use. Even if a current key is compromised, historical messages remain mathematically isolated and protected.

This aligns Wicked Crumbs with modern forward-secrecy standards while preserving your sovereign architecture.

"Today's keys should not become yesterday's messages."

PFS Roadmap Status

Perfect Forward Secrecy is actively Building Next — part of the near-term cryptographic strengthening of the Wicked Crumbs protocol.

Try Wicked Crumbs Protocol

Download Hansel 📧
Admin Console
ADMIN DASHBOARD

The Sovereign
Command Center.

RBAC seat management, DLP engine, eDiscovery, 365-day immutable audit logs, and real-time org health. Full enterprise control from a single console.

Real-Time Org Health Monitoring

Monitor communication health across your organization in real-time. Backup compliance rates, delivery health, DLP trigger frequency, and seat activity — all surfaced in a unified health dashboard.

  • ☑️ Real-time communication health signals
  • ☑️ Per-user backup compliance rates
  • ☑️ Delivery anomaly detection
Org Health
Policy Config

RBAC & Policy Enforcement

Four-tier role system: Super Admin, Dept Admin, Standard User, Read-Only Auditor. Define communication policies at org level — retention windows, external domain restrictions, encryption tier mandates, legal hold parameters.

Super Admin
Full org control
Dept Admin
Team-scoped control
Standard User
Standard access
Read-Only Auditor
Compliance view only

Data Loss Prevention

Pattern-based DLP policies intercept sensitive data before it exits your perimeter. Configure custom regex patterns, keyword triggers, and classification policies. Policy actions: block, flag, approve, or redact. Every trigger creates an immutable audit entry.

  • ☑️ Pattern library: SSN, credit cards, API keys, PHI
  • ☑️ Actions: Block / Flag / Approve / Redact
  • ☑️ Full audit trail for every DLP event
DLP
eDiscovery

eDiscovery & Legal Hold

Keyword and pattern search across your entire communication history. Apply legal holds in seconds. Export to PST, MBOX, JSON, or CSV. 365-day immutable audit logs for full compliance posture.

  • ☑️ Cross-channel keyword and pattern search
  • ☑️ Legal hold management with chain-of-custody tracking
  • ☑️ Export: PST / MBOX / JSON / CSV
  • ☑️ 365-day immutable audit logs
SAFER WORK

Safer work with granular,
controls

Move your entire organization's communication infrastructure in one pass. Preserve history, identity, and sovereign control from day one.

DATA PORTABILITY Business Professional

Forensic Export &
Sovereign Data Portability

Enterprise data shouldn't be trapped behind export walls or proprietary formats. Hansel's administrative controls treat data continuity as a first-class entitlement, giving admins full visibility, retention control, and zero-attrition migration paths — whether for compliance audits, legal reviews, or sovereign infrastructure swaps.

📦

Full Metadata-Preserving Export Suite

eDiscovery results, audit trails, and email archives export cleanly to PST, MBOX, JSON, and CSV formats with complete header retention, thread mapping, and cryptographic crumb chain integrity.

PST MBOX JSON CSV
⚖️

Legal Hold & Chain-of-Custody Tracking

Every export, search, or data handoff generates a tamper-evident log entry. Timestamps, admin IDs, and query scopes are preserved for legal and regulatory verification.

Tamper-Evident Logging
🚫

Seamless Sovereign Migration Paths

Admins can trigger full org archival in parallel with legacy provider routing. MX/SPF/DKIM records route cleanly, ensuring zero message loss during transition phases.

MX SPF DKIM
🏛️

True Sovereign Reset Enforcement

On decommission or seat revocation, the system executes a complete profile wipe: local data cleared, server-side orphaned records eliminated, and cryptographic keys permanently revoked. No residual data remains accessible.

Zero Residual Data
Sovereign Data Entitlement

"Enterprise data shouldn't be trapped behind export walls or proprietary formats. Data continuity is a first-class entitlement —a premium add-on."

REAL OPERATIONS

Built for Real Operations.
Not Theoretical Promises.

1.

Administrative efficiency, unlocked across every seat.

One unified console manages seats, domains, policies, DLP, and audit logs. Automate onboarding, enforce compliance baselines, and monitor org health in real time—cutting overhead without sacrificing direct control.

2.

Smooth migration without breaking continuity.

Drag-and-drop mailbox imports, bulk seat provisioning, and parallel DNS routing handled from the same dashboard. Track progress per user, preserve thread history, and switch MX/SPF/DKIM records seamlessly—so you go live without legacy data loss or service interruption.

3.

Verified protection, architecturally enforced.

From DLP pattern blocking and DMARC enforcement to immutable audit trails and legal holds, every compliance control runs on device-to-device cryptography. No bolt-on fees. No platform tenancy. Just continuous, verified security by default.

POLICY INTELLIGENCE Business Professional

Automated Policy Health
& Compliance Gap Detection

Policy management shouldn't require manual audits or quarterly compliance checklists. Hansel's admin console continuously monitors organizational security posture against active policy settings, automatically surfacing configuration gaps before they become risks.

From DMARC enforcement to backup frequency and identity verification, the dashboard acts as a living compliance engine —just a settings repository. Every misconfiguration is flagged in real time, every enforcement action is logged to the immutable audit trail.

📊

Continuous Policy Scoring

Admins receive a real-time Health Score calculated from active permissions, backup compliance rates, and security baseline adherence across all seats. No manual audit required.

🚨

Automated Gap Detection

Systems flag misconfigurations instantly: expired DNS records, unenforced 2FA policies, missing retention rules, or inactive DLP patterns. Surface risk before it becomes an incident.

⚖️

Framework-Aligned Enforcement

Policies map directly to architectural requirements for SOC 2, GDPR, and HIPAA alignment — including immutable audit capture and tamper-evident logging for every enforcement action.

🎛️

Granular Override Layer

Org-wide baselines can be locked while individual users or departments receive scoped permissions — e.g., me@company.com allows external forwarding while finance@company.com remains DLP-restricted.

Policy Enforcement Flow
01
Policy Set
02
Continuous Scan
03
Gap Flagged
04
Admin Alerted
05
Audit Logged

"The dashboard acts as a living compliance engine —just a settings repository."

Policy Health Console
Org Health Score
/ 100
Live · Updated just now
Active Gap Alerts
🚀
2FA Policy Not Enforced
3 seats in Finance dept missing mandatory 2FA enforcement
🏛️
DLP Pattern Inactive
SSN detection pattern disabled — 0 events logged in 14 days
Policy Baseline
DMARC Enforcement ☑️ Active
Backup Compliance Rate 94%
DLP Active Patterns 4 / 5 🚀
2FA Enforcement Partial ☑️
Audit Log Retention 365 days ☑️
hansel.admin · policy.engine
Business Professional
AdminOrganizationPolicyConfig
Policy Config View

Enterprise Feature Pricing Comparison

Feature Google Workspace
$6–$18/user/mo
Microsoft 365
$6–$22/user/mo
Hansel Business Pro
$12/seat/mo
DLP EngineEnterprise+ onlyE3/E5 only☑️ Included
eDiscoveryVault add-onE3/E5 only☑️ Included
365-day Audit LogsLimitedE5 only☑️ Immutable
Sovereign Key Ownership☑️☑️☑️ Always
Message TracingAdmin consoleAdmin center☑️ Full forensics
FAQS

Questions about
the Admin Dashboard?

Everything you need to know about enterprise controls, compliance tooling, and sovereign admin capabilities.

The Hansel Admin Dashboard is a sovereign enterprise command center —a settings page. From a single console, administrators get real-time org health monitoring across every seat, complete email domain management with auto-generated DNS records, a full billing overview, seat lifecycle management, RBAC role assignment, DLP policy enforcement, eDiscovery with legal hold, 365-day immutable audit logs, and message tracing forensics. Everything is on infrastructure your organization controls —a third-party vendor's dashboard you're renting access to.

Hansel uses a four-tier role system. Super Admins have full organizational control — seats, domains, policies, DLP, eDiscovery, billing, and all compliance tools. Department Admins have scoped control over their specific team, allowing delegation without granting root access. Standard Users have no admin privileges and operate their own account only. Read-Only Auditors can view logs, audit trails, and compliance reports but cannot make any changes — ideal for external auditors or compliance officers who need visibility without operational access.

* RBAC roles are an advanced role feature currently in Beta —yet generally available (GA).

Every outbound email passes through Hansel's DLP scanning pipeline before it ever leaves your organization. Administrators configure pattern rules — credit card numbers, SSNs, tax IDs, API keys, custom regex — and assign a policy action per rule. When a pattern is matched, the system can block the email entirely, flag it for manual review, hold it pending approval from a manager, or auto-redact the sensitive content before delivery. Every DLP event is logged with full context — who tried to send what, which rule triggered, what action was taken, and the exact timestampcreating an immutable compliance record.

eDiscovery gives administrators the ability to search, preserve, and export email records for legal, compliance, or investigative purposes. You would need it when responding to legal proceedings (litigation, regulatory investigations), audits, or internal HR investigations. Hansel's eDiscovery lets you search across all organizational email by sender, recipient, subject, message body, date range, and attachment name. You can apply legal holds that freeze specific mailboxes — preventing deletion of relevant messages — and then export findings in PST, MBOX, JSON, or CSV format for legal counsel. Every eDiscovery action is itself logged to the immutable audit trail for chain-of-custody integrity.

Business Professional retains 365 days of immutable audit logs — meaning no user or admin can alter or delete them. Every significant event across the organization is captured: authentication events (logins, failed attempts, device changes), email activity, backup events (created/restored/deleted), administrative actions (user provisioning, domain changes, DLP rule modifications, eDiscovery searches, legal holds applied/lifted), billing events, DLP trigger events, and permission changes. Logs are searchable by user, event type, date range, and severity, and are fully exportable for external compliance reporting.

Standard email logs tell you a message was sent. Message tracing tells you everything that happened to it. Hansel's message tracing shows the full delivery path — every server the message touched, delivery status (delivered, bounced, deferred, rejected), spam filter results and why they fired, SPF/DKIM/DMARC authentication pass/fail results, and the latency breakdown per hop. If a message didn't arrive, message tracing tells you exactly where it stopped and why. If a message looks potentially spoofed, message tracing surfaces the authentication failures that confirm it. Most platforms restrict this level of forensic visibility to enterprise support teams — Hansel gives it directly to your admins.

The core difference is pricing and ownership. Google Workspace requires Enterprise Plus ($30/user/mo) to unlock DLP, eDiscovery, and full audit logging. Microsoft 365 requires E3 or E5 ($22+/user/mo) for comparable compliance tooling. Hansel's Business Professional tier delivers DLP, full eDiscovery with legal hold, 365-day immutable audit logs, and message tracing forensics at $12/seat/month — roughly 40–60% cheaper. Beyond pricing, the structural difference is sovereignty: Google and Microsoft hold your encryption keys, control your data residency, and can lock you out. Hansel's admin console runs on infrastructure your organization controls, and a Sovereign Reset gives you a complete clean exit at any time.

Yes. Organizations can register and manage multiple custom email domains directly from the Hansel admin console. For each domain, the console auto-generates the exact SPF, DKIM, and DMARC DNS records you need, with clear setup instructions that don't require a support ticket or external documentation. Domain health is monitored in real time — you always have immediate visibility into the verification status of every domain your organization uses. This is particularly useful for holding companies, organizations with multiple brand identities, or businesses that have acquired other entities and need to unify email infrastructure under a single admin ledger.

Want to see how Hansel's admin compares to Google and Microsoft pricing?

Take Control of Your Organization

Get Hansel 📧
BACKUP & STORAGE

Your Data. Serialized.
Encrypted. Restored on Demand.

Gzip-compressed encrypted snapshots. Timestamped restore points. Org-wide backup compliance. Sovereign Reset capability.

What Gets Backed Up

All threads, messages, attachments, folder state, and read/unread markers are captured. Backups are serialized, Gzip-compressed, and encrypted before storage. Timestamped restore points let you roll back to any previous state.

  • ☑️ All email threads, messages, attachments
  • ☑️ Folder structure, labels, read/unread state
  • ☑️ Serialization 📧 Gzip 📧 Encryption pipeline
  • ☑️ Timestamped restore points
Backups
Local
Sovereign Free

On-device storage only

15 GB
Sovereign Pro

Cloud-backed sovereign storage

30 GB
Business Essentials

Per seat, org-managed

100 GB
Business Professional

Per seat, with admin compliance

Admin Backup Oversight

Business Professional includes org-wide backup compliance monitoring. Track per-user compliance rates, last backup timestamps, and storage consumption from the admin console. Scheduled automatic backups: daily, weekly, or custom cadence.

Admin Backup
COMPLIANCE-ALIGNED RETENTION & LEGAL PRESERVATION Business Professional

Backup Integrity Meets
Regulatory Requirements

For regulated operations, data decay is a compliance risk. Hansel aligns its backup lifecycle with business tier boundaries — preserving serialized archives in their original cryptographic state until explicitly purged or restored.

🌐
Backup Integrity

Cryptographic State Preservation

Serialized archives are preserved in their original cryptographic state until explicitly purged or restored. Business Professional seats automatically enforce 365-day immutable archival retention, ensuring backups remain legally admissible and auditable.

365-Day Immutable Retention
📦
Retention Policy

Lifecycle-Aligned Archival

Hansel aligns its backup lifecycle with business tier boundaries. Every archive path is retained across its full retention window — no silent expiry, no platform-side purge without explicit admin action. Regulated industries can rely on this as a structural guarantee, not a policy setting.

Explicit Purge Only
🔗
Chain-of-Custody

Verifiable Audit Without Intervention

Every archive path maintains chain-of-custody logging, so IT can verify integrity dates, compliance states, and export readiness without platform intervention or third-party audit dependencies. No external audit tool required — the evidence chain is native to the stack.

Native Audit Evidence
Compliance-Grade Archival

"For regulated operations, data decay is a compliance risk. Hansel's immutable archival retention ensures backups remain legally admissible without platform intervention or third-party audit dependencies."

VERSIONED SNAPSHOTS & CROSS-DEVICE CONTINUITY

Point-in-Time Recovery
Across Every Device

Backups aren't just archive files — they're versioned cryptographic snapshots. Each restore point captures thread states, attachment indices, folder hierarchy, and message flags at the exact moment of serialization.

Because Hansel operates on a local-first architecture, restored data syncs seamlessly across all authorized devices without platform intermediaries or cache fragmentation. Teams can pivot between desktop, mobile, and browser environments while maintaining exact state continuity — no sync conflicts, no orphaned attachments, zero platform dependency during restoration.

🧵
Thread States

Complete conversation chains captured at serialization time — every message, flag, and attachment index preserved.

📂
Folder Hierarchy

Full folder structure, labels, and read/unread status restored to the exact moment of backup creation.

🔗
Zero Sync Conflicts

Local-first architecture eliminates cache fragmentation and platform intermediaries during cross-device restoration.

🛡️
Zero Platform Dependency

No vendor intermediaries in the restoration path. State continuity is owned entirely by your device and your keys.

*

Mobile and browser support for Hansel is not currently generally available (GA). These capabilities will be rolled out periodically to users after the closed Beta ends, throughout open Beta, until full GA launch.

VERSIONED SNAPSHOT CHAIN SNAPSHOT v1 · T-72h 🌐 enc SNAPSHOT v2 · T-24h 🌐 enc SNAPSHOT v3 · NOW ☑️ LATEST ACTIVE RESTORATION 📧 DEVICE SYNC PATHS 🔄 RESTORE LOCAL-FIRST 🖥️ DESKTOP macOS / Win 🚀 SHIPPING NOW 📱 MOBILE iOS / Android 🏛️¨ BUILDING NEXT 🚫 BROWSER Web Client 🏛️¨ BUILDING NEXT 🧩 EXTENSION Chrome / Browser EXACT STATE CONTINUITY No sync conflicts · No orphaned attachments · Zero platform dependency 🌐 Cryptographic Snapshot · Device Keys Only
ZERO-TOUCH BACKUP ORCHESTRATION Business Professional

Scheduled Protection Without
Administrative Overhead

Business Professional organizations deploy background orchestration that runs silently across every seat. Administrators define cadence daily, weekly, or custom intervals — and the system serializes, compresses, and encrypts in parallel without impacting user workflow. Admin dashboards surface compliance rates, storage consumption deltas, and failed-job alerts instantly. It's enterprise-grade data continuity that operates autonomously, eliminating manual backup fatigue while guaranteeing predictable protection baselines across distributed teams.

AdminBackupManagement
94% Compliance
☑️ All Seats
Admin Backup Dashboard
Real-time org backup health monitoring
🗓️

Admin-Defined Cadence

Administrators set daily, weekly, or custom interval schedules per organization. Once configured, the system runs without any user-facing prompts or interruptions.

🔗

Parallel Serialization Pipeline

Serialization, Gzip compression, and encryption run in parallel across seats — zero impact on active user workflows, even during peak-usage hours.

📊

Instant Compliance Surface

Admin dashboards surface compliance rates, storage consumption deltas, and failed-job alerts in real time — no manual audit required to confirm organizational protection status.

Backup Schedule by Plan
Sovereign Pro $4/mo
Manual on-demand
Business Essentials $7/seat
Manual on-demand
Business Professional $12/seat
Scheduled automatic

Daily, weekly, or custom interval scheduling available exclusively on Business Professional. All tiers support manual on-demand backup at any time.

"Enterprise-grade data continuity that operates autonomously, eliminating manual backup fatigue."

Sovereign Decommission Data Lifecycle Control

Full Architectural Ownership
Through
Decommissioning.

True sovereignty includes the right to exit clean. The Sovereign Reset function executes a cryptographic purge: local device profiles are securely wiped, server-side serialized records are permanently decommissioned, and associated encryption keys are revoked at the hardware level.

No orphaned data, no dormant tenant liabilities, no vendor-held archives. For organizations migrating off-stack or retiring legacy infrastructure, this ensures complete data lifecycle closure — audited, verified, and irrevocable.

💻
Local Wipe

Device profiles securely erased. No residual local state remains.

🖥️
Server Purge

Serialized records permanently decommissioned server-side.

🎛️
Key Revocation

Encryption keys revoked at the hardware level. Mathematically final.

"No orphaned data. No dormant tenant liabilities.
No vendor-held archives."

Never Lose Your Data Again

Get Hansel 📧
Individuals

Personal Sovereignty.
No Compromise.

Whether you're a freelancer, journalist, legal professional, or privacy-conscious individual — Hansel gives you communication infrastructure that belongs to you. Sovereign free tier, forever.

Sovereign (Free)

  • ☑️ Personal email on your domain
  • ☑️ Wicked Crumbs E2E messaging
  • ☑️ Local storage — device-bound keys

Sovereign Pro ($4/mo)

  • ☑️ 15GB cloud-backed storage
  • ☑️ Unlimited integrations
  • ☑️ Priority support
THE SOVEREIGNTY SHIFT

Privacy Is an Outcome.
Sovereignty Is the
Architecture.

For individuals and independent professionals, platform dependency isn't just a privacy concernit's a structural business risk. Account suspensions, opaque policy shifts, and third-party data handling can erase years of professional infrastructure overnight.

Hansel answers this by decoupling your communications from centralized control. Your identity verification is cryptographic. Your email routing is sovereign. Privacy protects what others see; sovereignty ensures who controls the system it depends on.

🛡️

Privacy

Controls what others can see about your communications. Encryption in transit. End-to-end message protection.

🏗️

Sovereignty

Ensures who controls the system your communications depend on. Your SMTP. Your keys. Your infrastructure.

Platform Dependency Risks for Professionals
☑️

Account suspensions without warning or meaningful appeal window

☑️

Opaque policy shifts that retroactively restrict how your data is handled

☑️

Third-party data handling that can erase years of professional infrastructure overnight

"Privacy is the outcome.
Sovereignty is the architecture."

SOVEREIGN ARCHITECTURE 🧑 YOU 📬 YOUR SMTP 🔒 YOUR KEYS 💾 YOUR DATA 🔄 SOVEREIGN EXIT PLATFORM DEPENDENCY suspended · locked · no appeal SOVEREIGNTY BOUNDARY
THE ROADMAP VISION

From Sovereign Communication to
Complete Workspace Infrastructure

This is only the first layer. Hansel is actively expanding from encrypted messaging and sovereign email into a broader operational environment.

Roadmap Status

"Your infrastructure scales as your responsibilities do. From individual sovereignty to a complete workspace alternative — one deliberate layer at a time."

Domain & Alias Console
Primary Domain
me@yourbusiness.com
Sovereign SMTP · DKIM ☑️ · SPF ☑️
LIVE
Active Aliases
3 Active
clients@yourbusiness.com
Context: Client comms
Active
vendors@yourbusiness.com
Context: Vendor routing
Active
q4campaign@yourbusiness.com
Context: Campaign Q4
Revoked
identity.sovereign · alias.router
PROFESSIONAL SOVEREIGN IDENTITY

Own Your Address.
Control Your Contexts.

Solopreneurs and professionals don't need more addresses — they need precise control over who reaches them and how they're perceived. Hansel delivers custom domain provisioning with intelligent alias routing.

Assign unique contexts for clients, vendors, or campaigns without exposing your primary identity. Revoke access instantly when engagements end. Your professional brand stays isolated from noise, spam lists, and platform policy shifts.

🚫

Custom Domain Provisioning

Bring your own domain — you@yourbusiness.com — on sovereign SMTP infrastructure with auto-generated SPF, DKIM, and DMARC records.

🏛️€

Intelligent Alias Routing

Create context-specific aliases per client, vendor, or campaign. Each alias routes to your primary inbox while keeping your core identity isolated.

🔗

Instant Revocation

When an engagement ends, revoke the alias instantly. No lingering exposure. No spam list carry-over. Your primary identity stays clean.

🛡️

Platform-Policy Immunity

Your professional brand runs on sovereign infrastructure — immune to third-party policy shifts, deliverability rule changes, or platform-enforced identity resets.

"Your professional brand stays isolated from noise, spam lists, and platform policy shifts."

Available From
Sovereign Pro — $4/month
Custom domain + alias routing + 15GB cloud storage
Get Started
ARCHITECTURAL DEFENSE

Wicked Crumbs:
Encryption Without Compromise

Most platforms promise privacy but retain server-side access to your keys. Hansel's proprietary protocol eliminates that gap entirely.

📱
01

QR Identity Exchange

Cryptographic public keys exchanged via QR scan. No central directory. No server-mediated trust.

🌐
02

Device-Bound Keys

Keys generated and stored exclusively on your device. The platform never sees plaintext. Ever.

📤
03

Encrypted Transmission

Only encrypted blobs traverse the network. Infrastructure routes — it cannot read. Forward-linked crumb chain travels with the payload.

🔗
04

Chain Validation

Recipient's device validates the forward-linked crumb chain. Tampering breaks the chain — detected locally, no server trust needed.

✅
05

Device-Only Decryption

Decryption is isolated to device boundaries. Even compromised network infrastructure cannot expose message content.

Most platforms promise privacy but retain server-side access to your keys. Hansel's proprietary protocol eliminates that gap entirely. Identity verification happens via cryptographic QR exchange — making impersonation mathematically impossible.

Every message leaves a forward-linked chain that only the authorized recipient can validate. Even if network infrastructure is compromised, decryption remains isolated to device boundaries. No trust required. Just verified mathematics.

"No trust required.
Just verified mathematics."

🔄
Rotating Identifiers

Identity paths shift every 15 minutes. Long-term surveillance correlation is computationally infeasible.

🚫
Impersonation: Impossible

Without the private key, no valid crumb chain can be forged. Math enforces identity —policy.

🏛️¸
Infrastructure-Agnostic

Even compromised network infrastructure cannot expose message content. Decryption is device-isolated by design.

🌱
Seedling's Own IP

Wicked Crumbs is fully proprietary built, owned, and evolved by Seedling. No dependency on third-party cryptographic libraries.

Startups

Team Infrastructure.
Without the Enterprise Tax.

Custom domain email, team seat provisioning, RBAC access control, and DLP — all at $7/seat/mo. No $18/user Workspace equivalent required.

Business Essentials ($7/seat/mo)

  • ☑️ Custom domain email for the entire team
  • ☑️ Seat management & RBAC
  • ☑️ 30GB storage per seat
  • ☑️ Team admin console
  • ☑️ DLP engine

Why Not Google or Microsoft?

  • ☑️ You own the keys
  • ☑️ No vendor lock-in risk
  • ☑️ DLP at $7 vs $18+ equivalent
  • ☑️ No shared relay infrastructure
SMALL & MEDIUM BUSINESSES 10–100 Employees

The Compliance Gap.
Closed at $12/seat.

SMBs face mounting regulatory obligations and data protection requirements but lack the IT headcount or budget for $20+/seat platform tiers.

Hansel delivers sovereign infrastructure, DLP pattern blocking, eDiscovery legal holds, and 365-day immutable audit trails at $12/seat/month. No bolt-on fees. No tier fragmentation. Just operational security that scales with your headcount, not your procurement budget.

🏗️

Sovereign Infrastructure

Your SMTP, your domain, your keys. No shared relay infrastructure or platform tenancy risk. Your communication layer belongs to you.

🛡️

DLP Pattern Blocking

Configurable patterns SSNs, credit cards, custom regex scanned on every outbound email before it leaves your perimeter. Block, flag, approve, or redact.

⚖️

eDiscovery Legal Holds

Keyword search across all org email, instant legal hold application, and export to PST/MBOX/JSON/CSV. Built in — no add-on required.

📦

365-Day Immutable Audit Trails

Every admin action, authentication event, DLP trigger, and email routing decision is logged with tamper-evident timestamps. Full year retention, always exportable.

vs. Enterprise Alternatives
Google Enterprise+ $30/user  Â·  Microsoft E3/E5 $22+/user  Â·  Hansel Business Professional $12/seat
40%
cheaper

"Operational security that scales with your headcount, not your procurement budget."

Business Professional
Per Seat / Month
$12
No bolt-on fees · No tier fragmentation
Included at this tier
☑️
Full DLP Engine
Pattern blocking · Block / Flag / Redact
☑️
eDiscovery + Legal Hold
Search · Hold · Export PST/MBOX/JSON
☑️
365-Day Immutable Audit Logs
Tamper-evident · Always exportable
☑️
Sovereign SMTP + Custom Domains
Your infrastructure · Device-bound keys
☑️
100 GB Per Seat
+ Org backup compliance monitoring
Comparable at this tier
Google Enterprise+ $30/user
Microsoft E3/E5 $22+/user
Hansel Business Pro $12/seat ☑️
hansel.smb compliance.engine
Live
Admin Command Console
Seat Provisioning
sarah@acme.com
Role: Dept Admin · Finance
Active
john@acme.com
Role: Standard User · Sales
Active
auditor@acme.com
Role: Read-Only Auditor
Audit
Custom Domain DNS
SPF ☑️ Verified
DKIM ☑️ Verified
DMARC ☑️ Enforced
Policy Enforcement
DLP Patterns Active 5 / 5
Backup Compliance 98%
2FA Enforced All Seats ☑️
hansel.admin · policy.console
Business Professional
CENTRALIZED ADMIN & POLICY CONTROL Business Professional

Complete Team Oversight.
Zero Admin Overhead.

Business Professional includes a unified command console for seat provisioning, custom domain DNS routing, and organization-wide policy enforcement. Administrators set baseline security rules, override permissions per department, monitor backup health across all seats, and enforce communication standards all without dedicated IT staff or third-party management portals.

🪪

Seat Provisioning

Assign, revoke, and manage every organizational seat from a single dashboard. No IT staff required — provision a new team member in seconds.

🚫

Custom Domain DNS Routing

Auto-generated SPF, DKIM, and DMARC records with real-time health monitoring. Know the verification status of every domain in your org at a glance.

🎛️

Org-Wide Policy Enforcement

Set baseline security rules across the entire organization and override permissions per department. Communication standards enforced architecturally —manually.

💾

Backup Health Across All Seats

Per-user backup compliance rates, last backup timestamps, and storage consumption — all monitored from a single admin view without third-party tooling.

No Dedicated IT Staff Required

Every admin control 🪪 seat provisioning, DNS routing, policy enforcement, backup compliance is operable by a non-technical founder or operations lead. No third-party management portals. No vendor support tickets.

1
console
everything

"Complete team oversight. Zero admin overhead."

COST PREDICTABILITY & SOVEREIGN ROUTING Business Professional

Predictable Scaling.
True Infrastructure Ownership.

Every seat unlocks sovereign SMTP routing, custom domain provisioning, end-to-end encrypted messaging, and centralized Stripe billing. As you add team members or departments, costs remain fixed per-seat with zero hidden platform tenancy fees. Your infrastructure scales linearlyyour operationa overhead stays flat.

📤
Per-Seat Entitlement

Sovereign SMTP Routing

Every seat activates dedicated sovereign SMTP routing and custom domain provisioning the moment it's assigned. No shared relay. No platform tenancy. Infrastructure ownership is baked into the per-seat cost —charged as an add-on.

☑️ Custom domain provisioning
☑️ SPF / DKIM / DMARC auto-generated
☑️ No shared relay infrastructure
🌐
Per-Seat Entitlement

End-to-End Encrypted Messaging

Wicked Crumbs protocol is activated across every seat. Device-bound keys, rotating cryptographic identifiers, and tamper-evident chains ensure your team's internal communications are architecturally private —reliant on platform promises or legal interpretations of "encryption."

☑️ Wicked Crumbs E2E on every seat
☑️ Device-bound keys — no server copies
☑️ Group messaging with hybrid encryption
📊
Zero Hidden Fees

Centralized Billing & Linear Scaling

Centralized Stripe billing gives finance complete visibility. As your team grows, cost scales linearly at the fixed per-seat rate with no hidden platform tenancy fees, no overage surprises, and no vendor-controlled pricing shifts. Operational overhead stays flat while infrastructure expands.

Cost per seat
$12 / seat / mo
Overhead as team grows
Flat
☑️ Centralized Stripe billing portal
☑️ No hidden platform tenancy fees
☑️ Infrastructure scales linearly
Sovereign Scaling Principle

"Your infrastructure scales linearlyyour operationa overhead stays flat."

Real-World Application Operational Security

Compliance Built Into
the Workflow.
Not Bolted On After.

For legal firms, consultancies, and financial operations handling confidential client data, Hansel replaces fragmented toolchains with a single sovereign layer.

DLP prevents accidental leaks, eDiscovery preserves records for regulatory review, and audit trails provide verifiable accountability. Move from reactive compliance to architectural control without enterprise procurement friction.

🛡️
DLP

Prevents accidental leaks before sensitive data leaves the org perimeter.

⚖️
eDiscovery

Preserves records for regulatory review with legal hold and structured export.

📦
Audit Trail

Verifiable accountability across every admin action, DLP event, and email operation.

"Move from reactive compliance to architectural control
without enterprise procurement friction."

STARTUPS & FOUNDING TEAMS The Early Infrastructure Decision

Build on Sovereign Ground.
Scale Without Debt.

Founding teams make infrastructure decisions with limited resources and tight deadlines. Once platform dependency takes root, migration breaks workflow and drains capital. Hansel gives early-stage teams sovereign email, crypto-verified messaging, and administrative controls from day one — so your foundation doesn't become a retrofit later.

🚀
Day 1
Sovereign from the start

Infrastructure sovereignty is vastly easier to build at founding than to retrofit after platform dependency has taken root across your team's workflows.

No Retrofit Required
The Platform Dependency Trap

The earliest infrastructure decisions
become the hardest to undo.

Startups default to Google Workspace or Microsoft 365 because they're familiar and fast to provision. But familiarity isn't sovereignty. The moment your team's email, messaging, and documents are routed through a third-party platform, that platform holds structural power over your most sensitive communications — investor conversations, cap table discussions, IP documentation, and competitive strategy.

Platform dependency compounds. Every new hire provisioned through Google is another thread in the dependency web. By Series A, migration is disruptive enough that most founders accept the risk as a permanent operating condition. Hansel removes the trap entirely by being the right decision from day one.

🚀
Account Suspension Risk

A single ToS flag can lock your entire founding team out overnight — no appeal window, no data access.

📉¸
Migration Costs Scale

At 10 people migration is feasible. At 50 it's a full project. At 200 it's a multi-quarter initiative that drains capital and focus.

"The earliest infrastructure decisions become the hardest to undo."

What Hansel Gives Founders

Sovereign email, crypto-verified messaging,
and admin controls from day one.

With Hansel, a two-person founding team gets the same sovereign infrastructure a 200-person organization would need — provisioned in minutes, priced for early stage. Custom domain email on sovereign SMTP, Wicked Crumbs encrypted messaging for sensitive conversations, and an admin console to manage seats as the team scales.

📬
Sovereign Email & Custom Domain

Ship outbound comms from you@yourcompany.com on infrastructure you control —Google's or Microsoft's shared relay.

🌐
Crypto-Verified Messaging

Wicked Crumbs protocol keeps founder conversations — investor updates, cap table discussions, IP strategy — device-bound and architecturally unreadable by any platform.

🛡️
Admin Controls That Scale With You

Provision new seats, manage domains, enforce policies, and monitor backup compliance — all from a single console that grows with your headcount.

💾
Encrypted Backup & Sovereign Reset

Serialized, Gzip-compressed, and encrypted snapshots of your entire communication history. Sovereign Reset gives you a clean architectural exit at any time.

Founding Team Stack
Sovereign Pro
Personal sovereignty layer
$4/mo
Business Essentials
Team + admin console
$7/seat
Business Professional
DLP + eDiscovery + Audit
$12/seat
Your tier grows as your team does
2 founders 50 employees Enterprise
🌱
0
Platform-Accessible Keys

Your encryption keys never leave your devices. Not even Hansel can read your messages.

Day 1
Sovereign by default

Not a feature unlocked later. Sovereignty is the architectural foundation —an upgrade path.

When Hansel Makes Sense

The earlier sovereignty becomes
part of the architecture,
the less disruptive it is.

Hansel is particularly relevant for startups that handle sensitive intellectual property, are actively raising capital, communicate with investors or strategic partners, work with confidential customer information, and want sovereign infrastructure before complexity takes over.

☑️ Handling sensitive IP or fundraising discussions
☑️ Communicating with investors or strategic partners
☑️ Building toward stronger compliance requirements
☑️ Wanting infrastructure that scales without migration debt
Start Sovereign Today
From Sovereign Pro at $4/mo to Business Essentials at $7/seat
No trial expiry. No lock-in. Upgrade as your team grows.
Get Hansel Free

"Your foundation shouldn't become a retrofit later."

SECURING IP, CAPITAL & STRATEGIC COMMS

Protect What Matters Most.
Architecturally.

Seed rounds, cap tables, product roadmaps, and investor communications require strict access boundaries. Wicked Crumbs ensures only authorized devices can decrypt sensitive discussions. QR-verified identity exchange prevents impersonation. Your most critical conversations stay isolated from platform telemetry and third-party tracking.

🌐
01
Encryption

Device-Bound Cryptographic Keys

Seed round documents, cap table discussions, and investor strategy sessions are encrypted on your device before leaving it. Only authorized recipient devices — holding the correct private keys — can ever decrypt the content. Hansel's infrastructure routes the message; it cannot read it. Platform telemetry captures nothing meaningful.

☑️ Wicked Crumbs device-bound keys
☑️ Zero platform access to plaintext
☑️ Tamper-evident forward-link chains
📱
02
Identity Verification

QR-Verified Identity Exchange

In high-stakes startup conversations — investor intros, co-founder agreements, legal counsel coordination — impersonation is an existential risk. Wicked Crumbs eliminates it architecturally. Contacts are established via cryptographic QR key exchange. No valid crumb chain, no message delivery. Impersonation is mathematically infeasible, not just policy-restricted.

☑️ QR cryptographic key exchange
☑️ No central directory or password
☑️ Impersonation architecturally impossible
🛡️
03
Data Isolation

Isolated from Platform Telemetry

Google and Microsoft infrastructure logs routing metadata, session patterns, and behavioral signals — even when message content is encrypted in transit. Hansel's rotating cryptographic identifiers continuously break correlation graphs. Third parties cannot reliably map who communicates with whom, how often, or from where. Your investor pipeline and strategic roadmap stay invisible to surveillance infrastructure.

☑️ Rotating identifier metadata blindness
☑️ No third-party tracking or telemetry
☑️ Communication pattern correlation broken
Sovereign from the First Conversation

"Seed rounds, cap tables, and investor communications require strict access boundaries. Wicked Crumbs ensures only authorized devices can decrypt — by design, not by policy."

Get Hansel
SECTION 3 — ADMINISTRATIVE BASELINES FOR EARLY TEAMS

Founder-Level Admin.
Enterprise-Grade Boundaries.

You don't need a full IT department to enforce security. Hansel's admin console lets founders set baseline policies, manage custom domains, provision seats as the team grows, and monitor backup compliance across all devices. Sovereignty scales with your hiring pipeline —your technical capacity.

Founder Admin Console
Baseline Policies
2FA Enforcement
All seats · Org-wide
Active
DLP Pattern Blocking
SSN · CC · Custom Regex
5 Rules
Backup Compliance
Weekly schedule · All devices
96%
Custom Domains
startup.com ☑️ Live
SPF / DKIM / DMARC ☑️ All Verified
Seat Growth
6 / 10 seats
4 seats available · +$12/seat to expand
Administrative Baselines Business Professional

Sovereignty scales with your
hiring pipeline —
not your technical capacity.

You don't need a full IT department to enforce security. Hansel's admin console gives founders the power to set org-wide baseline policies from day one — before your team has a dedicated ops person, before your first compliance audit, and before platform dependency turns into a structural liability.

Provision seats as you hire. Manage custom domains from the same console that auto-generates your SPF, DKIM, and DMARC records. Monitor backup compliance across every device in your organization. Set baseline 2FA enforcement that applies automatically to every new seat. The admin layer grows with your team without requiring you to scale your technical capacity alongside it.

🎛️

Baseline Policy Enforcement

Set 2FA requirements, session timeout rules, email retention windows, and DLP patterns at the org level. Every new seat inherits the baseline automatically.

🚫

Custom Domain Management

Register your startup's domain and provision team email addresses from the same console. Auto-generated SPF, DKIM, and DMARC records with real-time health monitoring — no DNS expertise required.

🪪

Seat Provisioning as You Hire

Add new team members in seconds. Each new seat inherits org-wide policy settings instantly — no manual configuration, no onboarding overhead, no IT ticket required.

💾

Backup Compliance Across All Devices

Monitor per-seat backup compliance rates, last backup timestamps, and storage consumption from a single admin view. Know exactly which devices are protected without chasing individuals.

"Sovereignty scales with your hiring pipeline —
not your technical capacity."

Available On
Business Professional — $12/seat/month
Full admin console + DLP + eDiscovery + 365-day audit logs + org backup compliance
Get Hansel
ENTERPRISE & REGULATED INDUSTRIES COMPLIANCE & SOVEREIGNTY

The Hidden Risk of
Platform Tenancy.

"Free commercial tiers and shared cloud suites operate under vendor terms that often contradict regulatory mandates — from GDPR territorial borders to student privacy acts. Relying on 'platform promises' instead of architectural sovereignty is a structural liability."

🚀
Vulnerable State

Platform Promise

  • ☑️Vendor controls your keys
  • ☑️Foreign jurisdiction exposure
  • ☑️No data residency guarantee
  • ☑️Account suspension risk
migrate to
🏛️
Assess Risk

Infrastructure Audit

  • 📧Map data flows & borders
  • 📧Identify regulatory gaps
  • 📧Quantify liability exposure
  • 📧Evaluate vendor terms
deploy
VERIFIED
🎛️
Verified State

Sovereign Infrastructure

  • ☑️Device-bound cryptographic keys
  • ☑️Territorial data jurisdiction
  • ☑️Immutable compliance audit trail
  • ☑️Sovereign Reset — clean exit always

"This isn't about features. It's about infrastructure liability.
The question isn't whether your platform can be compelledit's whether yours can."

LARGE ENTERPRISES (1000+ Employees) The Coexistence Model

Sovereign Perimeters for
Your Most Critical Workflows.

You don't need to replace Microsoft or Google overnight. Hansel introduces a coexistence model: deploying sovereign infrastructure strictly around M&A teams, General Counsel, and R&D leadership. This creates an encrypted, isolated channel for market-moving conversations that runs parallel to — and completely independent of — your corporate cloud suites.

For a large enterprise, the near-term opportunity is not replacing Google or Microsoft across thousands of seats. It is protecting the conversations that could move markets, compromise acquisitions, or expose litigation strategy — starting today, without disruption.

Targeted Deployment Scenarios
⚖️
Legal

General Counsel & confidential litigation strategy

🤝
M&A

Deal-side negotiations & acquisition reviews

🏛️¬
R&D

Proprietary research & trade secret protection

🏢
Executive

Board-level strategy isolated from cloud admin reach

"Sovereignty begins where the risk is highest —
not where the migration is easiest."

COEXISTENCE ARCHITECTURE CORPORATE CLOUD SUITE (unchanged) 📬 Microsoft 365 General employees 📂 Google Workspace Collaboration & docs 💬 Slack / Teams Day-to-day comms SOVEREIGN PERIMETER HANSEL SOVEREIGN CHANNEL (isolated) 🤝 M&A Team ⚖️ General Counsel 🏛️¬ R&D Leadership 🌐 End-to-end encrypted · Device-bound keys Cryptographically isolated from corporate cloud EXISTING STACK SOVEREIGN LAYER
GOVERNMENT AGENCIES Jurisdictional Immunity

Eliminate Foreign
Jurisdiction Exposure.

"Your organization's data should never be subject to foreign intelligence access requests via the CLOUD Act. Hansel enables government bodies to deploy sovereign infrastructure on local servers within your own national borders, establishing jurisdictional immunity for public records, policy discussions, and citizen data."

01
The Problem

Jurisdictional Risk

Google and Microsoft are US companies subject to the CLOUD Act, which allows US authorities to compel access to data regardless of where it physically resides. For government agencies outside the US — and within it — foreign jurisdictional exposure is a disqualifying characteristic.

CLOUD Act Exposure
Foreign compulsion regardless of data location

When a government body's communications run through Google or Microsoft infrastructure, those communications become legally accessible to US authorities under CLOUD Act provisions — regardless of where the physical servers are located, and regardless of bilateral agreements.

For municipal, regional, and national government bodies handling citizen records, public policy discussions, and sensitive administrative communications, this is not a theoretical risk. It is an active operational vulnerability that contradicts legal data sovereignty mandates in most jurisdictions.

CLOUD Act Compulsion Foreign Intelligence Risk Extraterritorial Warrants

Hansel resolves this by enabling government agencies to deploy their own communication infrastructure on servers physically located inside their own jurisdiction running Hansel's encrypted protocol and administrative tooling under direct institutional control.

The infrastructure belongs to the government body. No US company holds the keys. No foreign court order can reach what a foreign company does not possess. Communications governed by local law —vendor terms and conditions.

On-Premises Deployment National Border Data Residency Institutional Key Ownership
02
The Solution

Local Server Deployment

☑️

Servers within national borders

☑️

Hansel protocol & tooling on your hardware

☑️

No foreign entity holds keys or data

03
The Result

Total Territorial Control

100%
Jurisdictional Immunity

No foreign authority can compel access to infrastructure your government physically owns and operates.

The result is complete territorial control. Public records, policy discussions, and citizen data are governed exclusively by the laws and institutions of the jurisdiction in which they reside —by the corporate terms of a foreign technology vendor.

Every administrative action is logged in an immutable, tamper-evident audit trail. eDiscovery tools enable public records requests without third-party platform delays. The government body is, for the first time, the actual owner of its own communication infrastructure.

eDiscovery
Native public records request processing
365-Day
Immutable audit retention built-in

"Public records under the sole authority
of the people they serve."

Education Institutions Institutional Stewardship

Protecting Academic
Discourse and
Student Trust.

"Student records and faculty correspondence are under increasing scrutiny. Instead of relying on free commercial platforms with opaque data practices, establish genuine sovereignty over your institution's intellectual property and staff communications — fulfilling strict data privacy mandates from the ground up."

Free offerings from Google and Microsoft dominate education because they're convenient. But their centralized infrastructure creates persistent data sovereignty questions that regulators are increasingly scrutinizing. Platform terms are not architected around sovereign student data protection. Hansel is.

🎓
FERPA

Student records privacy — US education institutions

🧒
COPPA

Children's online privacy — under-13 data protection

🇪🇺
GDPR

EU data sovereignty — territorial residency mandates

🌐
SOVEREIGN

Institutional infrastructure ownership — guaranteed exit

"School communications and student records
should never be treated as commoditized platform data."

UNIFIED TECHNICAL CAPABILITY Business Professional

Forensic-Ready Compliance,
Built into the Workflow.

Across all three sectors — large enterprises, government agencies, and educational institutions — Hansel delivers a unified command center for verification and regulatory compliance.

🏛️
eDiscovery

Search & Export

Process public records requests and legal holds natively. Full-text and pattern search across all organizational email and messaging history. Export results in JSON or CSV format for legal counsel or regulatory submission — with complete chain-of-custody logging for every action.

JSON CSV PST MBOX Legal Hold
📦
Audit Trails

365-Day Immutable Retention

Tamper-evident visibility into every admin action and data handoff. Authentication events, email activity, DLP triggers, eDiscovery searches, legal hold applications — every significant action is logged with precise timestamps. Immutable: no user or admin can alter or delete records.

Retention Period
365 Days
Tamper-Evident
🛡️
DLP Enforcement

Architectural Pattern Blocking

Prevent accidental leakage of sensitive IP or citizen data before it ever leaves your organization. Configurable patterns SSNs, health identifiers, API keys, custom regex scanned on every outbound email. Policy actions: Block, Flag, Approve, or Redact. Every trigger generates an immutable compliance record.

Block Transmission ☑️
Auto-Redact Content ☑️
Custom Regex Patterns ☑️
Unified Across All Three Sectors

"Whether you're a multinational enterprise protecting M&A conversations, a government agency processing public records requests, or a university fulfilling FERPA obligations the same forensic-grade compliance toolkit is available at a single tier."

STRATEGIC CLOSING Regulated Growth

Build a Compliant Infrastructure
That Outlasts Platform Trends.

"For enterprises, government bodies, and institutions, sovereignty isn't a featureit's the baseline requirement for operational longevity. Establish your sovereign communication layer today on a stack designed for regulatory adherence and absolute control."

🏛️ eDiscovery + Legal Hold
📦 365-Day Audit Trails
🛡️ DLP Pattern Blocking
🌐 Sovereign Key Ownership
Business Professional
$12
per seat / month
No bolt-on fees · No tier fragmentation
All compliance tools included at this tier
Download Admin Brief

Part of the Seedling ecosystem Let's Grow Together.

SECURITY & COMPLIANCE

Infrastructure Ownership
vs. Platform Dependency.

The difference isn't a featureit's a fundamental architectural choice that determines whether you control your communication or merely rent access to it.

Origin

The Origin Story

Hansel was founded after a real organization was locked out of their Google Workspace account overnight. No warning, no appeal window, no data access. Every email, every file, every communication - inaccessible. This is the vendor lock-in trap. Hansel was architected so this can never happen to you.

Own the Infrastructure

Your SMTP, your relay, your servers not shared Google infrastructure.

Own the Keys

Device-bound cryptographic keys. Hansel never sees plaintext.

Own the Exit

Sovereign Reset: local wipe, server cleanup, factory-fresh state.

Warning

The Vendor Lock-In Anatomy

When you use Google Workspace or Microsoft 365, they control your encryption keys, your data residency, your account access, and your compliance evidence. A Terms of Service violation — real or automated — and your organization loses everything, with no recourse. This is by design, not accident.

Platform Dependency Risks

  • ☑️ Account suspension without appeal
  • ☑️ Keys held by vendor
  • ☑️ Data residency not guaranteed
  • ☑️ Compliance tools locked to highest tiers
  • ☑️ No exit without data loss risk
PROTOCOL INDEPENDENCE POLICY RESILIENCE

Architecture That Doesn't Blink
When Platforms Change.

Commercial cloud suites operate on centralized control. They update APIs, throttle deliverability, shift pricing models, or sunset features without warning. Sovereign infrastructure breaks this dependency chain by design.

🔗
01 — Platform Volatility

API updates, pricing model shifts, feature sunsets without warning, without consent.

🔗
02 — Vendor Roadmap Dependency

Your operational continuity becomes hostage to their product decisions and release cadence.

🎛️
03 — Sovereign Determinism

Your stack runs on open standards. You control the deployment cadence. No consent required.

Sovereign infrastructure breaks the dependency chain by design. Your communication stack runs on deterministic, open standards — SMTP routing, Wicked Crumbs cryptographic exchange, local-first serialization — that don't require consent from a third-party vendor to function.

When market volatility hits, policies fracture, or platform roadmaps drift, your infrastructure operates deterministically. You don't adapt to their updates — you control your own deployment cadence.

📤
SMTP Routing

Open standard. No vendor permission required to route your email.

🌐
Wicked Crumbs

Proprietary cryptographic exchange. Device-bound. Platform-independent.

💾
Local-First

Serialized, encrypted, restorable on demand. You hold the keys.

"You don't adapt to their updates —
you control your own deployment cadence."

SOVEREIGN STACK — DETERMINISTIC PLATFORM VOLATILITY API changes · pricing shifts · feature sunsets policy fractures · vendor roadmap drift SOVEREIGN SHIELD YOUR INFRASTRUCTURE — DETERMINISTIC 📤 SMTP 🌐 WICKED CRUMBS 💾 LOCAL-FIRST YOU CONTROL THE DEPLOYMENT CADENCE Open standards · No vendor consent required OPERATIONAL CONTINUITY Regardless of market volatility · policy fracture · roadmap drift HANSEL · SOVEREIGN ARCHITECTURE
The Real Cost Shared Tenancy

The Invisible Debt of
Shared Infrastructure.

Platform dependency is rarely just about the monthly subscription. It's about feature fragmentation, data gravity, and integration debt. Third-party suites force you through a vendor's routing logic, unified UI layers, and bundled feature sets that prioritize their ecosystem over your operational needs.

Sovereign infrastructure eliminates this gravity model. Every component — custom domain provisioning, cryptographic identity, backup serialization, and DLP enforcement — operates independently under your governance. This clears hidden TCO: no forced bundle upgrades, no feature rot as vendor priorities shift, and zero exit friction when your organization outgrows the platform's designed perimeter.

True ownership compounds; shared tenancy depreciates.

🚫
No Forced Upgrades

Features you need don't disappear behind a higher tier you didn't budget for.

🛡️
No Feature Rot

Vendor priority shifts don't erode the capabilities your operations depend on.

🚪
Zero Exit Friction

Sovereign Reset gives you a clean architectural exit — always, on your terms.

"True ownership compounds;
shared tenancy depreciates."

Technical Sovereignty Matrix

Architectural Layer Legacy Cloud
(Google / Microsoft)
Zero-Knowledge Cloud
(Proton)
Open Cloud
(Fastmail)
Hansel
(Seedling.io)
Cryptography & Key Custody Server-side management. Provider generates, holds, and rotates keys; content is accessible to internal automated systems for indexing. Client-side PGP. Keys generated in-browser/app. Encrypted key blobs are backed up to centralized remote servers. Transport/Rest Encryption. Standard server-controlled data keys. No built-in client-side zero-knowledge framework. Local-First Asymmetric. Keys are generated and stored exclusively on local physical hardware. Zero remote backup footprint or external exposure.
DLP & Auditing Enterprise Tier Add-on. Complete compliance logging, dictionary matching, and eDiscovery via expensive corporate custom licensing. Highly Restricted. Zero-knowledge architecture natively conflicts with standard server-side deep content inspection and global compliance filtering. Basic Rules Engine. Standard sieve filtering, custom headers, and retention controls, but lacks native behavior-based corporate policy triggers. Local Deterministic DLP. Local pattern-matching engines process streaming content natively on-device before sync queues. Ingests without central leaks at <$12/seat.
Identity & Control Centralized Provider. Profile is tied directly to vendor identity systems. The platform reserves administrative rights to suspend or terminate access. Centralized Identity. While data is encrypted, account authentication depends on hosted identity clusters. Subject to remote vendor lockouts. Centralized Independent. Private infrastructure provider. Full customer service path for account recovery, but access remains vendor-dependent. Sovereign Instance. System operates as an isolated node. No parent organization or central identity registry possesses a remote kill switch or exit block.
Mail Transport (SMTP) Proprietary Relays. Outbound/Inbound traffic travels exclusively through massive centralized IP pools with built-in metadata profiling. Central Private Relays. Fully hosted infrastructure routed through secure, private network pipelines controlled by a single company. Open Protocol Clusters. Standard cloud-hosted MX infrastructure utilizing modern open extensions (JMAP, IMAP). Sovereign Local Relay. Operates containerized local SMTP configurations. Integrates direct P2P validation vectors to isolate outbound transport.
Spam Mitigation Heuristic / AI Scanning. Massive centralized ML models ingest and parse global inbound message bodies to calculate probability scores. Content-Blind Filters. Relies heavily on network reputation, IP blocklists, and user-defined sender/domain logic due to encrypted bodies. Heuristic Bayesian Engine. Standard collaborative cloud spam networks analyzing message header properties and known bad attachment fingerprints. Cryptographic Verification. Rejects untrusted incoming network requests at the perimeter connection layer unless signed by authorized validation keys.
DLP & LEGAL CONTROLS

Data Loss Prevention
& Legal Controls.

Pattern-based DLP, legal hold, eDiscovery export, message tracing forensics, and 365-day immutable audit logs built into Business Professional.

DLP Pattern Library & Policy Actions

Define custom patterns or use the pre-built library: SSN, credit card numbers, IBAN, API keys, health identifiers (PHI). Each pattern maps to a policy action: Block transmission, Flag for review, Auto-approve with logging, or Redact before delivery.

DLP
eDiscovery

eDiscovery Search, Hold & Export

Full-text and pattern search across email and messaging history. Apply legal holds instantly content is preserved immutably. Export packages support PST (Outlook-compatible), MBOX (universal), JSON (structured), and CSV (tabular) formats for legal counsel and compliance submissions.

DLP PATTERN LIBRARY Business Professional

Precision Rule Matching with
Configurable Policy Execution

Every outbound message is evaluated against a layered rule engine before transmission. Administrators deploy five pre-configured recognition patterns (credit card numbers, Social Security numbers, API keys/credentials, plaintext passwords, phone numbers) or define unlimited custom regex rules tailored to organizational identifiers.

Each pattern triggers a strictly configurable policy action. Every action captures sender identity, matched pattern type, timestamp, and routing context into the immutable audit log. DLP rules operate deterministically against traffic at the SMTP relay layer reactive post-hoc audits.

🚫

Block

The message is withheld from sending at the client endpoint. The sender receives a contextual prompt explaining the violation, and the event is logged with full metadata.

🚩

Flag

The message routes normally but generates a compliance alert for administrator review, preserving workflow continuity while capturing risk exposure.

Pre-Configured Pattern Library
💳 Credit Card Numbers 🏛️¢ Social Security Numbers 🔒 API Keys / Credentials 🌐 Plaintext Passwords 📞 Phone Numbers ✏️ Unlimited Custom Regex

"DLP rules operate deterministically against traffic at the SMTP relay layer —
not as reactive post-hoc audits."

HanselDLPScreenshot
Active Pattern Rules
SSN Pattern BLOCK
Credit Card BLOCK
API Key FLAG
Custom Regex #1 FLAG
eDISCOVERY CHAIN-OF-CUSTODY EXPORT Business Professional

eDiscovery Search Scope &
Chain-of-Custody Export

Targeted Historical Retrieval with Preserved Legal Integrity

When compliance or litigation requires structured record production, the eDiscovery engine executes cross-mailbox searches across the entire organization. Admins filter by sender, recipient, subject keywords, date ranges, and attachment metadata to isolate relevant correspondence.

Targeted mailboxes can be placed under legal hold, freezing both existing and newly received messages from deletion until explicitly released. Retrieved records export natively in PST, MBOX, JSON, or CSV formats, preserving original message headers, thread mappings, and cryptographic crumb chain verification markers.

Every search query, hold creation/modification, and export action is logged with tamper-evident timestamps to establish court-admissible chain of custody. Compliance tools operate as architecturally enforced layers bolt-on third-party connectors.

🏛️
Search Scope

Cross-Mailbox Search

Execute cross-mailbox searches across the entire organization. Filter by sender, recipient, subject keywords, date ranges, and attachment metadata to isolate relevant correspondence with precision.

Sender Recipient Keywords Date Range Attachments
🔒
Legal Hold State

Immutable Hold Management

Place targeted mailboxes under legal hold, freezing both existing and newly received messages from deletion until explicitly released. Hold status is invisible to the end user — preventing tampering while preserving legal integrity.

Hold Status
Admin-Only
Invisible to User
📦
Chain-of-Custody Export

Court-Admissible Record Production

Export in PST, MBOX, JSON, or CSV preserving original headers, thread mappings, and cryptographic crumb chain verification markers. Every action logged with tamper-evident timestamps.

PST MBOX JSON CSV

"Compliance tools operate as architecturally enforced layers bolt-on third-party connectors."

Message Tracing Delivery Path Forensics

Full Routing Transparency
& Authentication Diagnostics

Every sent or received message generates a complete delivery trace, mapping each routing hop from sender infrastructure through external gateways to final reception. Admins inspect SPF/DKIM/DMARC authentication results at every stage, latency metrics per gateway, and bounce/reject codes with root-cause breakdowns.

When paired with DLP events or deliverability disputes, tracing logs isolate whether failures stem from policy blocking, DNS misconfiguration, recipient server filtering, or path bottlenecks. This forensic layer replaces guesswork in routing incidents, accelerates threat response for spoofing attempts, and provides verifiable proof of message handling for regulatory audits.

📤
Routing Hops

Full delivery path from sender SMTP through every external gateway to final reception.

🌐
Auth Results

SPF / DKIM / DMARC pass/fail at every stage with granular per-hop diagnostics.

🫩
Latency Breakdown

Latency metrics per gateway and bounce/reject codes with root-cause breakdowns.

"This forensic layer replaces guesswork in routing incidents
and provides verifiable proof of message handling for regulatory audits."

ANSWERS

Find the Answers
that you need.

Everything you need to know about Hansel's features, pricing, encryption, and sovereignty principles.

"Sovereign" means you own and control the infrastructure your communications run on —a third-party vendor. When you use Google Workspace or Microsoft 365, those platforms hold your encryption keys, control your data residency, and can revoke your access without warning. Hansel was built to ensure your email server remains entirely yours, your encryption keys never leave your physical device hardware, and you retain absolute data ownership.

Your asymmetric encryption keys are generated and stored exclusively on your device—the central system architecture never sees your plaintext. Messages are pinned with tamper-evident cryptographic hashes so any modification to historical data is detected instantly client-side. This eliminates intermediate cloud decryption risks entirely.

Yes, Hansel features fully native mobile clients. Because there is no centralized third-party cloud server caching your messages, synchronization uses a secure local-first, peer-to-peer (P2P) replication architecture. When your mobile device and desktop are on the same network—or securely linked via your team's self-hosted instance node—they securely stream delta-sync updates directly to each other without intermediate platform exposures.

Traditional Data Loss Prevention requires a centralized cloud server to decrypt, read, and inspect the body of every email before it is sent. Hansel breaks this reliance by performing Local Deterministic DLP directly on the client machine. Corporate compliance rules, keyword dictionary patterns, and regex string matchers are distributed securely to your team's local devices, scanning payloads in memory before asymmetric encryption wraps them.

A core tenet of architectural sovereignty is that you are never locked into a single software vendor. The Sovereign Reset feature allows your team to perform a complete, clean exit at a moment's notice. With a single administrative command, you can export your entire database of historical threads, contacts, and calendar configurations into standard, open formats (like MBOX, EML, and vCard) without platform friction.

Hansel relies entirely on self-hosted local execution parameters. Because computing power, network bandwidth, database management, and transport pipelines run on your own private infrastructure hardware nodes instead of a centralized cloud service cluster, you pay nothing to external providers. There are no corporate API keys required, no structural token dependencies, and no remote operational profiles to maintain.

Hansel utilizes a decentralized fallback architecture. Standard sending servers automatically queue message retries for up to 5 days under standard SMTP rules if your node is temporarily unreachable. Additionally, you can configure lightweight, encrypted secondary backup relays that buffer incoming data packages without gaining technical ability to decrypt or read your historical archive payloads.

Instead of evaluating content formatting post-delivery, Hansel’s edge layer drops connections from unauthenticated senders at the perimeter interface. Inbound connection systems require valid structural signatures matching your trusted domain network or automated public key handshakes, isolating your server instance from corporate phishing networks and automated bulk blast scripts entirely.

COMPLIANCE READINESS

Architecture Aligned.
Posture Ready.

Hansel is architecturally aligned with HIPAA, GDPR, and SOC 2 requirements. We do not claim certifications we provide the infrastructure that enables your compliance posture.

Policy Config

Admin Policy Enforcement

Compliance posture requires consistent policy enforcement. Hansel's admin console enables retention window mandates, external domain restrictions, encryption tier requirements, and legal hold configurationcreating the audit-ready evidence your compliance team needs.

HIPAA
Architectural alignment
GDPR
Data residency & erasure
SOC 2
Audit trail readiness
IMMUTABLE AUDIT TRAILS FORENSIC VISIBILITY Business Professional

Tamper-Evident Logging.
Every Action. Every Timestamp.

Compliance isn't about what you say happensit's about the proof that it did.

Hansel generates a continuous, tamper-evident audit trail covering authentication events, email routing actions, backup state changes, seat provisioning, permission updates, DLP violations, and eDiscovery queries. Each log entry carries cryptographic timestamps and operator context, making alteration mathematically impossible.

Business Professional tenants retain these records for up to 365 days, searchable by user, event type, date range, or severity. Exports are machine-readable and preserved exactly as logged no formatting drift, no vendor-side aggregation. When regulators ask "was this system breached?" or "did admin X override policy Y?", your audit log provides the answer on day one.

🔗
01 🔗Event Occurs

Admin action, auth event, DLP violation, routing decision — captured at origin.

🕐
02 🕵️ Cryptographic Timestamp Added

Each entry receives an immutable cryptographic timestamp. Alteration becomes mathematically impossible.

🔒
03 🔒 Immutable Log Stored

Records written to tamper-evident store. No user or admin can alter or delete entries.

📤
04 📤 Searchable / Exportable

Filter by user, event type, date range, or severity. Export machine-readable records exactly as logged.

365
Days Immutable Retention

Business Professional tenants retain tamper-evident audit records for a full year — searchable, exportable, court-admissible.

0
Vendor-Side Aggregation

Exports preserved exactly as logged. No formatting drift. Machine-readable records with full cryptographic integrity intact.

Audit Trail Coverage
🌐 Authentication Events 📬 Email Routing Actions 💾 Backup State Changes 🪪 Seat Provisioning 🎛️ Permission Updates 🛡️ DLP Violations 🏛️ eDiscovery Queries

"When regulators ask 'was this system breached?' or 'did admin X override policy Y?', your audit log provides the answer on day one."

TAMPER-EVIDENT AUDIT CHAIN AUTH_EVENT admin@org.com · login · 2024-01-15T09:12:44Z hash: 0x4f3a9c... · ☑️ VERIFIED DLP_VIOLATION user@org.com · SSN_PATTERN · BLOCKED hash: 0x8b2e1d... · prev: 0x4f3a9c... · ☑️ EDISCOVERY_QUERY admin@org.com · keyword: "acquisition" · 47 results hash: 0x2c7f4e... · prev: 0x8b2e1d... · ☑️ PERMISSION_UPDATE superadmin · role_change · dept_admin 📧 standard hash: 0x9a3c6f... · prev: 0x2c7f4e... · ☑️ 🌐 CHAIN INTEGRITY: VERIFIED Any modification breaks the cryptographic chain 365-Day Immutable Retention
Architectural Alignment Transparent Path to Verification

Compliance-Ready Architecture.
Transparent Path
to Verification.

Hansel is architecturally positioned to align with SOC 2, GDPR, HIPAA, and other regulated frameworks through its foundational design: device-level encryption boundaries, sovereign data custody, verifiable audit capture, and strict policy enforcement layers. This isn't a compliance "add-on"it's structural by default.

However, Hansel draws a clear line between capability and credential. Specific regulatory certifications are not claimed until formally audited, issued, and publicly documented. What is documented today is the baseline: your organization gets the architectural controls required to meet those frameworks on day one, with certification status updated transparently as verification milestones are completed. No marketing spin. Just verifiable readiness.

🎛️
SOC 2

Immutable audit trails, access control, and policy enforcement layers map directly to SOC 2 Trust Service Criteria.

Architecturally Aligned
🇪🇺
GDPR

Sovereign data custody, Sovereign Reset (right to erasure), and data residency configuration support GDPR territorial requirements.

Architecturally Aligned
🏥
HIPAA

Device-level encryption, DLP PHI pattern blocking, 365-day audit retention, and access controls support HIPAA safeguard requirements.

Architecturally Aligned
📦
Certification Policy

Certifications not claimed until formally audited, issued, and publicly documented. Status updated transparently as milestones are completed.

No Marketing Spin

"Your organization gets the architectural controls required to meet those frameworks on day one. No marketing spin. Just verifiable readiness."

SOVEREIGN DATA RESIDENCY POLICY LOCKDOWN Business Professional

Data Borders & Policy Enforcement.
Built for Regulated Environments.

Regulated organizations don't just need compliance tools — they need jurisdictional control.

Hansel's infrastructure model supports data-residency requirements by allowing deployment configuration and storage routing to align with the regulatory geography where permitted. Paired with admin policy enforcement, operators can lock down 2FA mandates, password complexity baselines, session timeouts, email retention windows, and DLP redactions across every seat or scope overrides per department.

These policies run architecturally; they don't rely on "trust me" UI toggles or revocable platform permissions. When legal counsel demands proof that sensitive data never left authorized boundaries, your policy engine provides the deterministic guardrails.

Step 01

Data Residency Configuration

Deployment configuration and storage routing aligned to regulatory geography.

Jurisdictional Control

Infrastructure routing aligned to
your regulatory geography.

Hansel's infrastructure model supports data-residency requirements by allowing deployment configuration and storage routing to align with the regulatory geography where permitted. This means your communication data is processed and stored within the jurisdictional boundaries required by your compliance mandate wherever a shared cloud vendor's capacity happens to be cheapest that day.

🌍 EU Data Residency 🎛️ National Border Compliance 🗺️ Deployment Routing Config
Architectural Policy Engine

Lock down every seat, every policy,
architecturally —by toggle.

Operators can lock down 2FA mandates, password complexity baselines, session timeouts, email retention windows, and DLP redactions across every seat or scope overrides per department. These policies run architecturally; they don't rely on "trust me" UI toggles or revocable platform permissions.

🔒 2FA Mandates
🔒 Password Complexity Baselines
🫩 Session Timeouts
📦 Email Retention Windows
🛡️ DLP Redaction Policies
🎛️ Per-Department Scoped Overrides
POLICY
Step 02

Architectural Policy Lockdown

Policies enforced at the infrastructure layer revocable UI toggles.

☑️
Step 03

Deterministic Guardrails

Legal counsel gets proof. Data never left authorized boundaries.

Provable Compliance Posture

When legal counsel demands proof,
your policy engine provides it.

When legal counsel demands proof that sensitive data never left authorized boundaries, your policy engine provides the deterministic guardrails platform promise, not a vendor attestation letter. The policies run architecturally, generating verifiable evidence that is logged, timestamped, and tamper-evident by design.

Regulated Environment Ready
Architectural
Policies enforced at infrastructure —UI layer
Verifiable
Tamper-evident logs prove every enforcement action

"These policies run architecturally; they don't rely on 'trust me' UI toggles or revocable platform permissions."

FAQS

Compliance Readiness
Questions Answered.

Common questions about Hansel's compliance posture, certifications, audit trails, and regulatory alignment.

Hansel draws a clear line between capability and credential. Hansel is architecturally positioned to align with SOC 2, GDPR, HIPAA, and other regulated frameworks through its foundational design: device-level encryption boundaries, sovereign data custody, verifiable audit capture, and strict policy enforcement layers. However, specific regulatory certifications are not claimed until formally audited, issued, and publicly documented. What is available today is the architectural baseline — your organization gets the infrastructure controls required to meet those frameworks on day one, with certification status updated transparently as verification milestones are completed.

Business Professional retains 365 days of immutable audit logs — no user or admin can alter or delete them. Every significant event across the organization is captured: authentication events (logins, failed attempts, device changes), email activity, backup events (created/restored/deleted), administrative actions (user provisioning, domain changes, DLP rule modifications, eDiscovery searches, legal holds applied/lifted), billing events, DLP trigger events, and permission changes. Logs are searchable by user, event type, date range, and severity, and are fully exportable for external compliance reporting.

Hansel's Sovereign Reset function directly supports GDPR's right to erasure. When executed, it performs a complete cryptographic purge: local device profiles are securely wiped, server-side serialized records are permanently decommissioned, and associated encryption keys are revoked. No orphaned data, no dormant tenant liabilities, no vendor-held archives remain. For data residency, Hansel's infrastructure model supports deployment configuration and storage routing aligned to the regulatory geography where applicable — meaning your communication data can be processed and stored within the jurisdictional boundaries required by your GDPR mandate.

Hansel's admin console enables a comprehensive set of policy controls that run architecturally —as revocable UI toggles. Operators can mandate 2FA across all seats, set password complexity baselines, enforce session timeouts, define email retention windows, configure DLP redaction policies, and scope per-department overrides. These policies are enforced at the infrastructure layer and generate tamper-evident audit trail entries for every enforcement action, providing verifiable proof that your compliance posture is actively maintained.

Hansel's Business Professional tier delivers DLP pattern blocking, eDiscovery with legal hold, 365-day immutable audit logs, and message tracing forensics as built-in capabilities bolt-on add-ons. For many regulated SMBs and mid-market organizations, this replaces the need for separate compliance monitoring tools or expensive enterprise tier upsells from Google or Microsoft. For organizations with existing SIEM or compliance platforms, Hansel's exportable, machine-readable audit logs (with full metadata preservation) are designed to integrate cleanly into those workflows.

Shared cloud platforms create a structural compliance gap: the vendor holds your encryption keys, controls your data residency, and can modify platform terms retroactively. This means your compliance posture depends on their promises, not architectural guarantees. Sovereign infrastructure eliminates this dependency. With Hansel, your encryption keys never leave your devices, your audit trail is cryptographically tamper-evident, your policies run at the infrastructure layer, and your data can be exported or purged on your terms. Compliance becomes a verifiable architectural property —a vendor attestation you have to trust.

Want to explore the full compliance and audit architecture?

PRICING & PLANS

Pricing Built for
Sovereignty.

From personal privacy to enterprise-grade compliance. No lock-in. You own everything.

Sovereign
Free
Forever yours
  • ☑️ Personal email (1 domain)
  • ☑️ Wicked Crumbs messaging
  • ☑️ Local storage
  • ☑️ Device-bound keys
Get Started Free
Sovereign Connected
Free
+ Group messaging
  • ☑️ Everything in Sovereign
  • ☑️ Wicked Crumbs group messaging
  • ☑️ 1 connected integration
  • ☑️ Priority message delivery
Get Started Free
Most Popular
Sovereign Pro
$4/mo
Per user, billed monthly
  • ☑️ Everything in Connected
  • ☑️ 15GB cloud storage
  • ☑️ Unlimited integrations
  • ☑️ Advanced encryption tiers
  • ☑️ Priority support
Business Essentials
$7/seat/mo
For growing teams
  • ☑️ Custom domain email
  • ☑️ Seat management & RBAC
  • ☑️ 30GB/seat storage
  • ☑️ Team admin console
  • ☑️ DLP engine
Business Professional
$12/seat/mo
Full enterprise flagship
  • ☑️ Everything in Essentials
  • ☑️ Full DLP & eDiscovery
  • ☑️ 100GB/seat storage
  • ☑️ 365-day immutable audit logs
  • ☑️ Org backup compliance
  • ☑️ Message tracing forensics
Book a Call

Full Feature Comparison

Feature Sovereign Connected Pro Essentials Professional
Communication
Personal Email 1 domain 1 domain ✓ ✓ Custom ✓ Custom
Wicked Crumbs Messaging ✓ ✓ + Groups — ✓ ✓
Encrypted Messaging Device-side Device-side — Plan dependent Plan dependent
Cryptographic Message Verification ✓ ✓ — — —
Tamper-Evident Message History ✓ ✓ — — —
Offline Operation ✓ ✓ Limited Limited Limited
Privacy & Encryption
Device-Side Encryption ✓ ✓ — — Plan dependent
Encryption Key Ownership You You — Provider / plan dependent Provider / contract
Hansel Plaintext Access None None — Service dependent Service dependent
Cryptographic Identity ✓ ✓ — — —
Message Authenticity Verification ✓ ✓ — — —
Data & Storage
Storage Local Local 15 GB 30 GB / seat 100 GB / seat
Local-First Architecture ✓ ✓ — — —
Peer-to-Peer Synchronization ✓ ✓ — — —
Self-Hosted Infrastructure ✓ ✓ — — Plan dependent
Data Residency Control You control it You control it Provider Provider Provider / contract
Ownership & Portability
Sovereign Reset ✓ ✓ ✓ ✓ ✓
Full Data Export ✓ ✓ ✓ ✓ ✓
Migration to Open Formats ✓ ✓ ✓ ✓ ✓
Vendor Lock-In Protection ✓ ✓ Limited Limited Contract / platform dependent
Architecture Ownership You You Provider Provider Provider
Enterprise Controls
RBAC / Seat Management — — — ✓ ✓
DLP Engine — — — ✓ ✓
Local DLP Inspection ✓ ✓ — ✓ ✓
eDiscovery — — — — ✓
Message Tracing — — — — ✓
365-Day Audit Logs — — — — ✓ Immutable
Organization Backup Compliance — — — — ✓
Economics
Recurring Per-Seat SaaS Fee $0 $0 ✓ ✓ ✓

Have questions about pricing?

Pricing FAQ

Hansel AI
Hansel AI
Online

Hey there! I'm Hansel AI your guide to sovereign communication.
Ask me anything about pricing, encryption, or how Hansel stacks up against Google & Microsoft.

Hansel
Hansel AI
Online

Ask me anything about Hansel: